Interconnecting EVPN VXLAN to MPLS
This chapter includes step-by-step configurations for Interconnecting EVPN VXLAN to MPLS.
Overview
Interconnecting EVPN VXLAN to MPLS provides seamless Layer-2 and Layer-3 interworking between a VXLAN-based data center (DC) fabric and an MPLS-based Wide Area Network (WAN) or Data Center Interconnect (DCI) domain. Deployed on Border Gateways (BGWs), the interconnecting gateway performs encapsulation translation (VXLAN ↔ MPLS) while maintaining unified EVPN control-plane reachability and route semantics (Type-1, Type-2, Type-3, Type-4, and Type-5)
Feature Characteristics
• The Interconnecting EVPN VXLAN to MPLS solution allows separate Route Distinguishers (RDs) and Route Targets (RTs) to be configured independently for LAN (DC) and WAN (DCI) domains under MAC-VRF and IP-VRF interconnecting blocks.
• To prevent routing loops during inter-domain route re-origination, the system implements a 6-byte BGP Domain Path (D-PATH) attribute across EVPN, IPVPN, and local BGP routes. Resilient DCI connectivity and load balancing are provided through the Interconnect Ethernet Segment Identifier (iESI), which supports All-Active multihoming and aliasing across dual Border Gateways.
• Additionally, per-MAC-VRF options control proxy ARP/ND caching and suppress broadcast flooding toward the WAN and DC fabrics, while Layer 3 route re-origination enables seamless prefix exchange between EVPN Type-5 or Type-2 routes and IPVPN (VPNv4/VPNv6) or IPv4/IPv6 VRF unicast routes.
Benefits
• Seamless Data Center to WAN Interworking: Enables transparent Layer-2 and Layer-3 service extension between VXLAN-based data center fabrics and MPLS-based WAN/DCI transport networks without requiring protocol conversions or static configuration overhead.Control-Plane Integrity & Route Preservation: Preserves end-to-end BGP EVPN route semantics across domains (Type-1, Type-2, Type-3, Type-4, and Type-5 routes).
• High Availability & Resiliency: Supports Interconnect Ethernet Segment Identifiers (iESI) with All-Active multihoming and aliasing across dual Border Gateways, ensuring load balancing and fault tolerance.
• Loop Prevention Across Domains: Implements the BGP Domain Path (D-PATH) attribute to automatically detect and discard looped routes during multi-domain route re-origination.
Limitations
• Not supported on Qumran 1 devices.
• EVPN-VPWS (E-LINE) is not supported.
• EVPN unnumbered mode is not supported
• EVPN asymmetric-IRB is not supported on the Border Gateway (BGW).
• Anycast BGW deployment is not supported.
• Not applicable for static VXLAN or MPLS tunnel configurations.
• Using the same Route Distinguisher (RD) on both DC and WAN sides is not supported; separate RDs must be configured.
• Interconnecting L3 is done via EVPN-VXLAN to MPLS L3VPN (IPVPN), not EVPN-MPLS.
• The BGW operates as an ingress/PE router (RFC 9014); it cannot act as an ASBR or RR for Inter-AS Option A/B/C.
• Only All-Active multihoming redundancy mode is supported (Single-Active is not supported).
• Multi-homing on the gateway is constrained to dual-homing (maximum of 2 Border Gateways per iESI).
• The Unicast label is reused and advertised as the Alias label.
• LLF is not supported for stitched E-LAN/E-TREE services.
• Multi-homing for local ACs directly connected to the BGW is not supported.
• EOAM and CFM to detect individual AC failures between gateway and WAN edge routers are not supported.
• A MAC-VRF cannot be independently shared between VXLAN and MPLS unless configured in EVPN interconnecting mode.
• EVPN L3 Gateway with VXLAN Interconnecting is not supported on Qumran 2 platforms.
• When an interconnect gateway is configured for EVPN VXLAN and L3VPN interconnecting, it cannot simultaneously host independent L3 EVPN MPLS services.
• Removing EVPN interconnecting configuration from an active VRF (that was bridging VxLAN to L3VPN) prevents LAN routes from withdrawing correctly, which may lead to improper routing.
Workaround: To safely remove EVPN interconnecting from an active VRF, delete the entire VRF configuration and then re-create it without the EVPN interconnecting settings.
Workaround: To safely remove EVPN interconnecting from an active VRF, delete the entire VRF configuration and then re-create it without the EVPN interconnecting settings.
• When EVPN interconnecting is operational on a VRF, adding or modifying route-targets dynamically will not trigger an automatic update to LAN or WAN peers.
Workaround: After adding or modifying route-targets, manually run the "clear ip bgp all *" command to push the update to your peers:
Workaround: After adding or modifying route-targets, manually run the "clear ip bgp all *" command to push the update to your peers:
• Removing EVPN interconnecting under a MAC VRF or executing "no router bgp" may trigger HSL errors related to ESEM deletion. These messages can be safely ignored, as they do not affect traffic forwarding or network operations.
Prerequisites
Before configuring VXLAN and EVPN-MPLS multihoming, ensure that the following prerequisites are configured:
1. Enable the required hardware-profile filters:
hardware-profile filter evpn-arp-nd enable
hardware-profile filter evpn-stitch enable
hardware-profile filter vxlan-mh enable
hardware-profile filter evpn-mpls-mh enable
hardware-profile filter evpn-arp-nd enable
hardware-profile filter evpn-stitch enable
hardware-profile filter vxlan-mh enable
hardware-profile filter evpn-mpls-mh enable
2. Enable the global VXLAN and EVPN-MPLS features:
nvo vxlan enable
evpn mpls enable
nvo vxlan enable
evpn mpls enable
3. Configure the global VTEP source IP addresses:
nvo vxlan vtep-ip-global <DC-VTEP-IP>
evpn mpls vtep-ip-global <WAN-VTEP-IP>
nvo vxlan vtep-ip-global <DC-VTEP-IP>
evpn mpls vtep-ip-global <WAN-VTEP-IP>
Note: It is recommended to use different VTEP IP addresses for the VXLAN (DCI) and MPLS (WAN) domains to clearly distinguish between the two domains. For example:
nvo vxlan vtep-ip-global 77.77.77.77
evpn mpls vtep-ip-global 101.10.10.10
nvo vxlan vtep-ip-global 77.77.77.77
evpn mpls vtep-ip-global 101.10.10.10
4. Enable VXLAN and EVPN-MPLS multihoming:
evpn vxlan multihoming enable
evpn mpls multihoming enable
evpn vxlan multihoming enable
evpn mpls multihoming enable
Note: Both multihoming features are required for the iESI configuration to form successfully. The multihoming commands are rejected if the corresponding vxlan-mh and evpn-mpls-mh hardware-profile filters are not enabled.
5. Enable the evpn stitch hardware-profile filter on the interconnect gateway node for EVPN interconnecting to function.
Topology
The diagram depicts a multi-site data center fabric topology with Spine–Bleaf architecture, showing inter-site connectivity between Site A and Site B using EVPN VxLAN to MPLS interconnecting.
Figure 1-1 displays a sample EVPN VxLAN to MPLS interconnecting topology.
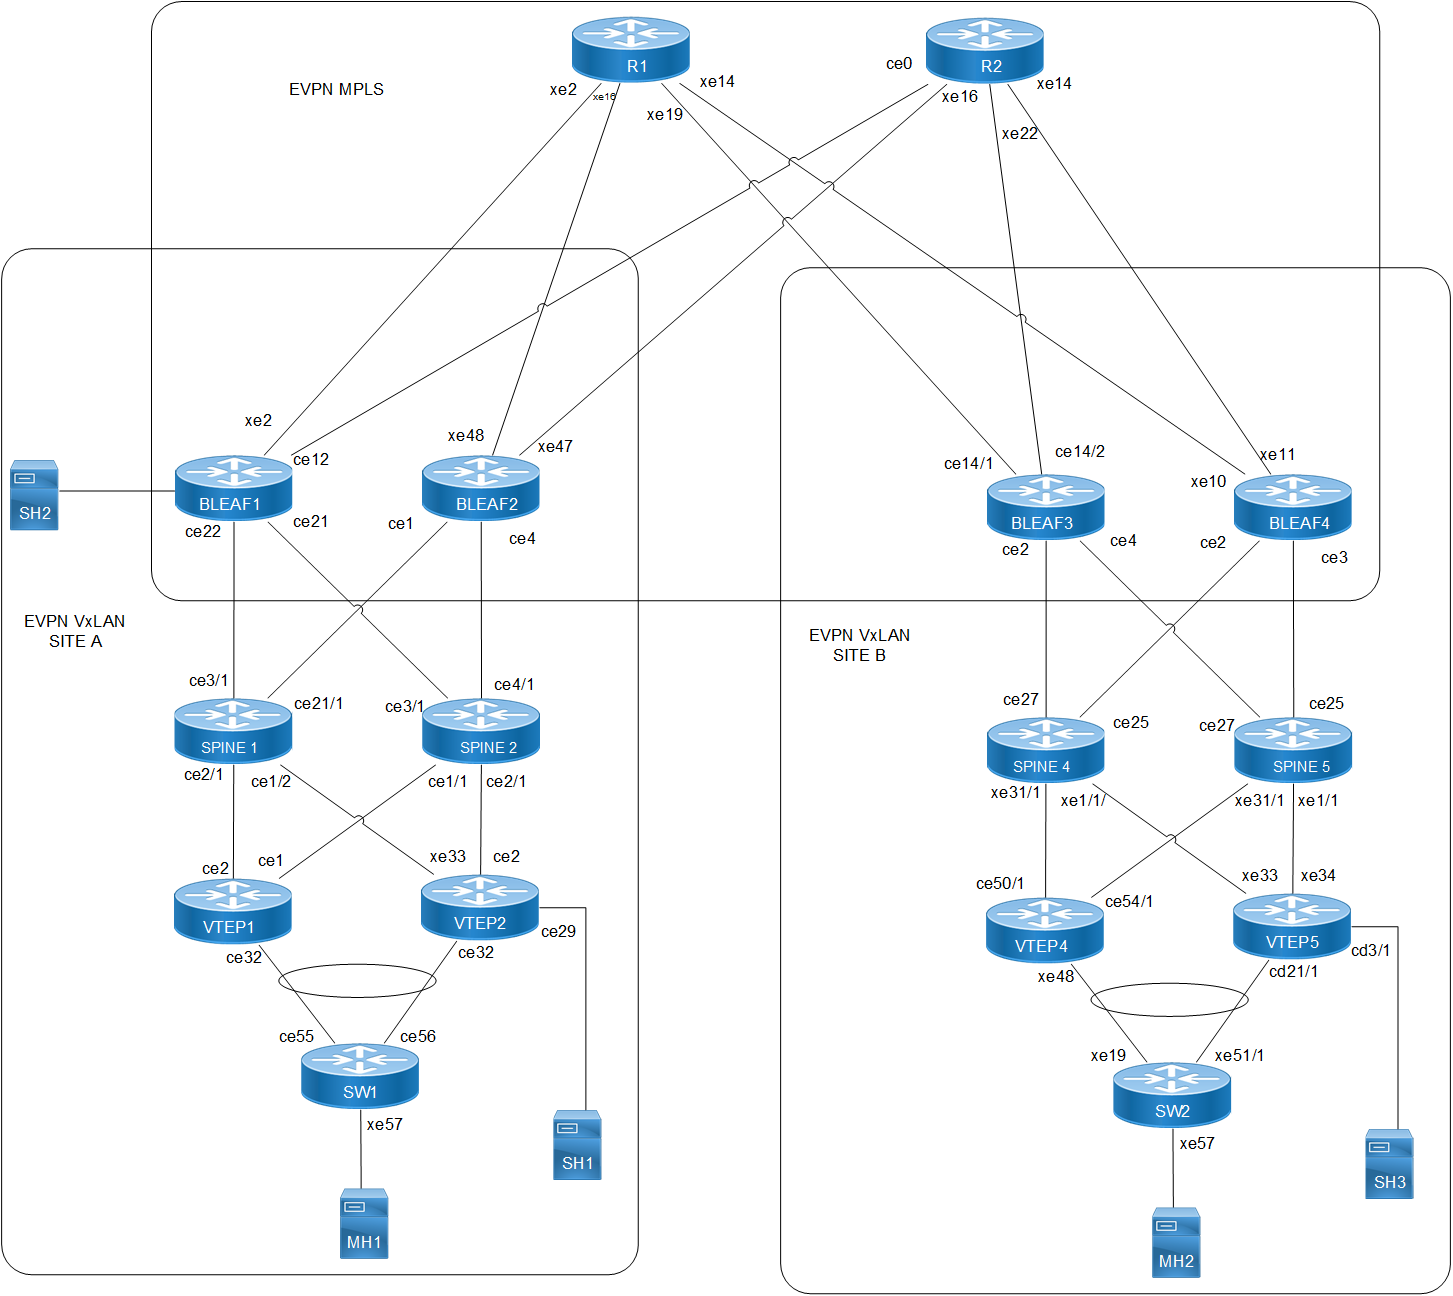
EVPN VxLAN to MPLS Interconnecting
Configuration
VTEP1
1. Enable VXLAN and IRB and EVPN VXLAN multihoming.
#configure terminal
(config)#nvo vxlan enable
(config)#nvo vxlan irb
(config)#evpn esi hold-time 100
(config)#evpn vxlan multihoming enable
(config)#evpn irb-forwarding anycast-gateway-mac 0000.0000.abcd
2. Configure L3 VRF with EVPN Interconnecting and enable EVPN Interconnecting.
(config)#ip vrf L3_VRF1
(config-vrf)#rd 1.1.1.1:101
(config-vrf)#route-target both 100:1
(config-vrf)#l3vni 1000
(config-vrf)#commit
(config-vrf)#exit
3. Configure MAC VRF.
(config)#mac vrf L2_VRF1
(config-vrf)#rd 1.1.1.1:1
(config-vrf)#route-target both 1:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF10
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 1.1.1.1:10
(config-vrf)#route-target both 10:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF2
(config-vrf)#rd 1.1.1.1:2
(config-vrf)#route-target both 2:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF3
(config-vrf)#rd 1.1.1.1:3
(config-vrf)#route-target both 3:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF4
(config-vrf)#rd 1.1.1.1:4
(config-vrf)#route-target both 4:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF5
(config-vrf)#rd 1.1.1.1:5
(config-vrf)#route-target both 5:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF6
(config-vrf)#rd 1.1.1.1:6
(config-vrf)#route-target both 6:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF7
(config-vrf)#rd 1.1.1.1:7
(config-vrf)#route-target both 7:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF8
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 1.1.1.1:8
(config-vrf)#route-target both 8:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF9
(config-vrf)#rd 1.1.1.1:9
(config-vrf)#route-target both 9:1
(config-vrf)#commit
(config-vrf)#exit
4. Configure global VTEP IP.
(config)#nvo vxlan vtep-ip-global 1.1.1.1
5. Enter the NVO VXLAN instance sub-mode for each VNI and bind it to its MAC-VRF and optional IRB interface.
(config)#nvo vxlan id 1001 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF1
(config-nvo)#evpn irb1001
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1002 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF2
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1003 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF3
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1004 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF4
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1005 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF5
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1006 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF6
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1007 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF7
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1008 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF8
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1009 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF9
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1010 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF10
(config-nvo)#commit
(config-nvo)#exit
6. Configure interfaces.
(config)#interface po100
(config-if)#switchport
(config-if)#load-interval 30
(config-if)#evpn multi-homed system-mac 0000.9999.1111
(config-if)#commit
(config-if)#exit
(config)#interface ce1
(config-if)#load-interval 30
(config-if)#ip address 10.1.2.1/24
(config-if)#commit
(config-if)#exit
(config)#interface ce2
(config-if)#load-interval 30
(config-if)#ip address 10.1.1.1/24
(config-if)#commit
(config-if)#exit
(config)#interface ce32
(config-if)#channel-group 100 mode active
(config-if)#commit
(config-if)#exit
(config)#interface irb1001
(config-if)#ip vrf forwarding L3_VRF1
(config-if)#evpn irb-if-forwarding anycast-gateway-mac
(config-if)#ip address 101.101.1.1/24 anycast
(config-if)#ipv6 address 101::1/64 anycast
(config-if)#commit
(config-if)#exit
(config)#interface lo
(config-if)#ip address 127.0.0.1/8
(config-if)#ip address 1.1.1.1/32 secondary
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
7. Configure OSPF underlay routing.
(config)#router ospf 100
(config-router)#ospf router-id 1.1.1.1
(config-router)#network 1.1.1.1/32 area 0.0.0.0
(config-router)#network 10.1.1.0/24 area 0.0.0.0
(config-router)#network 10.1.2.0/24 area 0.0.0.0
(config-router)#commit
(config-router)#exit
8. Configure BGP global parameters and neighbors.
(config)#router bgp 65001
(config-router)#bgp router-id 1.1.1.1
(config-router)#neighbor 2.2.2.2 remote-as 65001
(config-router)#neighbor 2.2.2.2 update-source lo
(config-router)#neighbor 13.13.13.13 remote-as 65002
(config-router)#neighbor 13.13.13.13 ebgp-multihop
(config-router)#neighbor 13.13.13.13 update-source lo
(config-router)#neighbor 14.14.14.14 remote-as 65002
(config-router)#neighbor 14.14.14.14 ebgp-multihop
(config-router)#neighbor 14.14.14.14 update-source lo
9. Configure BGP L2VPN EVPN address family.
(config-router)#address-family l2vpn evpn
(config-router-af)#neighbor 2.2.2.2 activate
(config-router-af)#neighbor 13.13.13.13 activate
(config-router-af)#neighbor 14.14.14.14 activate
(config-router-af)#commit
(config-router-af)#exit-address-family
10. Configure BGP IPv4 VRF address family.
(config-router)#address-family ipv4 vrf L3_VRF1
(config-router-af)#max-paths ebgp 4
(config-router-af)#max-paths ibgp 4
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#commit
(config-router-af)#exit-address-family
11. Configure BGP IPv6 VRF address family.
(config-router)#address-family ipv6 vrf L3_VRF1
(config-router-af)#max-paths ebgp 4
(config-router-af)#max-paths ibgp 4
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#commit
(config-router-af)#exit-address-family
(config-router)#commit
(config-router)#exit
12. Disable the cache.
(config)#nvo vxlan max-cache-disable 5
13. Enter into VxLAN MH access-port with VLAN and map vnid to access interface.
(config)#nvo vxlan access-if port-vlan po100 1001
(config-access-if)#map vnid 1001
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po100 1002
(config-access-if)#map vnid 1002
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po100 1003
(config-access-if)#map vnid 1003
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po100 1004
(config-access-if)#map vnid 1004
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po100 1005
(config-access-if)#map vnid 1005
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po100 1006
(config-access-if)#map vnid 1006
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po100 1007
(config-access-if)#map vnid 1007
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po100 1008
(config-access-if)#map vnid 1008
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po100 1009
(config-access-if)#map vnid 1009
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po100 1010
(config-access-if)#map vnid 1010
(config-access-if)#commit
(config-access-if)#exit
VTEP2
1. Enable VXLAN and IRB and EVPN VXLAN multihoming.
#configure terminal
(config)#nvo vxlan enable
(config)#nvo vxlan irb
(config)#evpn esi hold-time 100
(config)#evpn vxlan multihoming enable
(config)#evpn irb-forwarding anycast-gateway-mac 0000.0000.abcd
2. Configure L3 VRF.
(config)#ip vrf L3_VRF1
(config-vrf)#rd 2.2.2.2:101
(config-vrf)#route-target both 100:1
(config-vrf)#l3vni 1000
(config-vrf)#commit
(config-vrf)#exit
3. Configure MAC VRF.
(config)#mac vrf L2_VRF1
(config-vrf)#rd 2.2.2.2:1
(config-vrf)#route-target both 1:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF10
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 2.2.2.2:10
(config-vrf)#route-target both 10:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF2
(config-vrf)#rd 2.2.2.2:2
(config-vrf)#route-target both 2:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF3
(config-vrf)#rd 2.2.2.2:3
(config-vrf)#route-target both 3:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF4
(config-vrf)#rd 2.2.2.2:4
(config-vrf)#route-target both 4:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF5
(config-vrf)#rd 2.2.2.2:5
(config-vrf)#route-target both 5:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF6
(config-vrf)#rd 2.2.2.2:6
(config-vrf)#route-target both 6:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF7
(config-vrf)#rd 2.2.2.2:7
(config-vrf)#route-target both 7:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF8
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 2.2.2.2:8
(config-vrf)#route-target both 8:1
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF9
(config-vrf)#rd 2.2.2.2:9
(config-vrf)#route-target both 9:1
(config-vrf)#commit
(config-vrf)#exit
4. Configure global VTEP IP.
(config)#nvo vxlan vtep-ip-global 2.2.2.2
5. Enter the NVO VXLAN instance sub-mode for each VNI and bind it to its MAC-VRF and optional IRB interface.
(config)#nvo vxlan id 1001 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF1
(config-nvo)#evpn irb1001
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1002 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF2
(config-nvo)#evpn irb1002
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1003 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF3
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1004 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF4
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1005 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF5
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1006 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF6
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1007 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF7
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1008 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF8
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1009 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF9
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1010 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF10
(config-nvo)#commit
(config-nvo)#exit
6. Configure interfaces.
(config)#interface po100
(config-if)#switchport
(config-if)#load-interval 30
(config-if)#evpn multi-homed system-mac 0000.9999.1111
(config-if)#commit
(config-if)#exit
(config)#interface ce2
(config-if)#load-interval 30
(config-if)#ip address 20.1.2.1/24
(config-if)#commit
(config-if)#exit
(config)#interface ce29
(config-if)#switchport
(config-if)#load-interval 30
(config-if)#commit
(config-if)#exit
(config)#interface ce32
(config-if)#channel-group 100 mode active
(config-if)#commit
(config-if)#exit
(config)#interface irb1001
(config-if)#ip vrf forwarding L3_VRF1
(config-if)#evpn irb-if-forwarding anycast-gateway-mac
(config-if)#ip address 101.101.1.1/24 anycast
(config-if)#ipv6 address 101::1/64 anycast
(config-if)#commit
(config-if)#exit
(config)#interface irb1002
(config-if)#ip vrf forwarding L3_VRF1
(config-if)#ip address 201.101.1.1/24
(config-if)#ipv6 address 201::1/64
(config-if)#commit
(config-if)#exit
(config)#interface lo
(config-if)#ip address 127.0.0.1/8
(config-if)#ip address 2.2.2.2/32 secondary
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
(config)#interface xe33
(config-if)#load-interval 30
(config-if)#ip address 20.1.1.1/24
(config-if)#commit
(config-if)#exit
7. Configure OSPF underlay routing.
(config)#router ospf 100
(config-router)#ospf router-id 2.2.2.2
(config-router)#network 2.2.2.2/32 area 0.0.0.0
(config-router)#network 20.1.1.0/24 area 0.0.0.0
(config-router)#network 20.1.2.0/24 area 0.0.0.0
(config-router)#commit
(config-router)#exit
8. Configure BGP global parameters and neighbors.
(config)#router bgp 65001
(config-router)#bgp router-id 2.2.2.2
(config-router)#neighbor 1.1.1.1 remote-as 65001
(config-router)#neighbor 1.1.1.1 update-source lo
(config-router)#neighbor 13.13.13.13 remote-as 65002
(config-router)#neighbor 13.13.13.13 ebgp-multihop
(config-router)#neighbor 13.13.13.13 update-source lo
(config-router)#neighbor 14.14.14.14 remote-as 65002
(config-router)#neighbor 14.14.14.14 ebgp-multihop
(config-router)#neighbor 14.14.14.14 update-source lo
9. Configure BGP L2VPN EVPN address family.
(config-router)#address-family l2vpn evpn
(config-router-af)#neighbor 1.1.1.1 activate
(config-router-af)#neighbor 13.13.13.13 activate
(config-router-af)#neighbor 14.14.14.14 activate
(config-router-af)#commit
(config-router-af)#exit-address-family
(config-router)#address-family ipv4 vrf L3_VRF1
(config-router-af)#max-paths ebgp 4
(config-router-af)#max-paths ibgp 4
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#commit
(config-router-af)#exit-address-family
(config-router)#address-family ipv6 vrf L3_VRF1
(config-router-af)#max-paths ebgp 4
(config-router-af)#max-paths ibgp 4
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#commit
(config-router-af)#exit-address-family
10. Disable the cache.
(config)#nvo vxlan max-cache-disable 5
11. Enter into VxLAN MH access-port with VLAN and map vnid to access interface.
(config)#nvo vxlan access-if port-vlan ce29 1001
(config-nvo)#map vnid 1001
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan ce29 1002
(config-nvo)#map vnid 1002
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan ce29 1003
(config-nvo)#map vnid 1003
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan ce29 1004
(config-nvo)#map vnid 1004
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan ce29 1005
(config-nvo)#map vnid 1005
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan ce29 1006
(config-nvo)#map vnid 1006
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan ce29 1007
(config-nvo)#map vnid 1007
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan ce29 1008
(config-nvo)#map vnid 1008
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan ce29 1009
(config-nvo)#map vnid 1009
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan ce29 1010
(config-nvo)#map vnid 1010
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po100 1001
(config-nvo)#map vnid 1001
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po100 1002
(config-nvo)#map vnid 1002
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po100 1003
(config-nvo)#map vnid 1003
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po100 1004
(config-nvo)#map vnid 1004
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po100 1005
(config-nvo)#map vnid 1005
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po100 1006
(config-nvo)#map vnid 1006
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po100 1007
(config-nvo)#map vnid 1007
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po100 1008
(config-nvo)#map vnid 1008
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po100 1009
(config-nvo)#map vnid 1009
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po100 1010
(config-nvo)#map vnid 1010
(config-nvo)#commit
(config-nvo)#exit
VTEP4
1. Enable VXLAN and IRB and EVPN VXLAN multihoming.
#configure terminal
(config)#nvo vxlan enable
(config)#nvo vxlan irb
(config)#evpn esi hold-time 100
(config)#evpn vxlan multihoming enable
(config)#evpn irb-forwarding anycast-gateway-mac 0000.0001.abcd
2. Configure L3 VRF.
(config)#ip vrf L3_VRF1
(config-vrf)#rd 4.4.4.4:101
(config-vrf)#route-target both 100:2
(config-vrf)#l3vni 1000
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF1
(config-vrf)#rd 4.4.4.4:1
(config-vrf)#route-target both 1:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF10
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 4.4.4.4:10
(config-vrf)#route-target both 10:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF2
(config-vrf)#rd 4.4.4.4:2
(config-vrf)#route-target both 2:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF3
(config-vrf)#rd 4.4.4.4:3
(config-vrf)#route-target both 3:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF4
(config-vrf)#rd 4.4.4.4:4
(config-vrf)#route-target both 4:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF5
(config-vrf)#rd 4.4.4.4:5
(config-vrf)#route-target both 5:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF6
(config-vrf)#rd 4.4.4.4:6
(config-vrf)#route-target both 6:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF7
(config-vrf)#rd 4.4.4.4:7
(config-vrf)#route-target both 7:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF8
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 4.4.4.4:8
(config-vrf)#route-target both 8:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF9
(config-vrf)#rd 4.4.4.4:9
(config-vrf)#route-target both 9:2
(config-vrf)#commit
(config-vrf)#exit
3. Configure global VTEP IP.
(config)#nvo vxlan vtep-ip-global 4.4.4.4
4. Enter the NVO VXLAN instance sub-mode for each VNI (1001 to 1010) and bind it to its MAC-VRF and optional IRB interface.
(config)#nvo vxlan id 1001 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF1
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1002 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF2
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1003 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF3
(config-nvo)#evpn irb1003
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1004 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF4
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1005 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF5
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1006 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF6
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1007 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF7
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1008 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF8
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1009 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF9
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1010 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF10
(config-nvo)#commit
(config-nvo)#exit
5. Configure interfaces.
(config)#interface po200
(config-if)#switchport
(config-if)#load-interval 30
(config-if)#evpn multi-homed system-mac 0000.9999.2222
(config-if)#commit
(config-if)#exit
(config)#interface ce50/1
(config-if)#load-interval 30
(config-if)#ip address 40.1.1.1/24
(config-if)#commit
(config-if)#exit
(config)#interface ce54/1
(config-if)#load-interval 30
(config-if)#ip address 40.1.2.1/24
(config-if)#commit
(config-if)#exit
(config)#interface irb1003
(config-if)#ip vrf forwarding L3_VRF1
(config-if)#evpn irb-if-forwarding anycast-gateway-mac
(config-if)#ip address 102.101.1.1/24 anycast
(config-if)#ipv6 address 102::1/64 anycast
(config-if)#commit
(config-if)#exit
(config)#interface lo
(config-if)#ip address 127.0.0.1/8
(config-if)#ip address 4.4.4.4/32 secondary
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
(config)#interface xe48
(config-if)#channel-group 200 mode active
(config-if)#commit
(config-if)#exit
6. Configure OSPF underlay routing.
(config)#router ospf 100
(config-router)#ospf router-id 4.4.4.4
(config-router)#network 4.4.4.4/32 area 0.0.0.0
(config-router)#network 40.1.1.0/24 area 0.0.0.0
(config-router)#network 40.1.2.0/24 area 0.0.0.0
!
(config)#router bgp 65003
(config-router)#bgp router-id 4.4.4.4
(config-router)#neighbor 5.5.5.5 remote-as 65003
(config-router)#neighbor 5.5.5.5 update-source lo
(config-router)#neighbor 15.15.15.15 remote-as 65002
(config-router)#neighbor 15.15.15.15 ebgp-multihop
(config-router)#neighbor 15.15.15.15 update-source lo
(config-router)#neighbor 16.16.16.16 remote-as 65002
(config-router)#neighbor 16.16.16.16 ebgp-multihop
(config-router)#neighbor 16.16.16.16 update-source lo
(config-router)#address-family l2vpn evpn
(config-router-af)#neighbor 5.5.5.5 activate
(config-router-af)#neighbor 15.15.15.15 activate
(config-router-af)#neighbor 16.16.16.16 activate
(config-router-af)#commit
(config-router-af)#exit-address-family
(config-router)#address-family ipv4 vrf L3_VRF1
(config-router-af)#max-paths ebgp 4
(config-router-af)#max-paths ibgp 4
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#commit
(config-router-af)#exit-address-family
!
(config-router)#address-family ipv6 vrf L3_VRF1
(config-router-af)#max-paths ebgp 4
(config-router-af)#max-paths ibgp 4
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#commit
(config-router-af)#exit-address-family
7. Disable the cache.
(config)#nvo vxlan max-cache-disable 5
8. Enter into VxLAN MH access-port with VLAN and map vnid to access interface.
(config)#nvo vxlan access-if port-vlan po200 1001
(config-nvo)#map vnid 1001
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po200 1002
(config-nvo)#map vnid 1002
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po200 1003
(config-nvo)#map vnid 1003
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po200 1004
(config-nvo)#map vnid 1004
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po200 1005
(config-nvo)#map vnid 1005
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po200 1006
(config-nvo)#map vnid 1006
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po200 1007
(config-nvo)#map vnid 1007
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po200 1008
(config-nvo)#map vnid 1008
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po200 1009
(config-nvo)#map vnid 1009
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan access-if port-vlan po200 1010
(config-nvo)#map vnid 1010
(config-nvo)#commit
(config-nvo)#exit
VTEP5
1. Enable VXLAN and IRB and EVPN VXLAN multihoming.
#configure terminal
(config)#nvo vxlan enable
(config)#nvo vxlan irb
(config)#evpn esi hold-time 100
(config)#evpn vxlan multihoming enable
(config)#evpn irb-forwarding anycast-gateway-mac 0000.0001.abcd
2. Configure L3 VRF.
(config)#ip vrf L3_VRF1
(config-vrf)#rd 5.5.5.5:101
(config-vrf)#route-target both 100:2
(config-vrf)#l3vni 1000
(config-vrf)#commit
(config-vrf)#exit
3. Configure MAC VRF.
(config)#mac vrf L2_VRF1
(config-vrf)#rd 5.5.5.5:1
(config-vrf)#route-target both 1:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF10
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 5.5.5.5:10
(config-vrf)#route-target both 10:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF2
(config-vrf)#rd 5.5.5.5:2
(config-vrf)#route-target both 2:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF3
(config-vrf)#rd 5.5.5.5:3
(config-vrf)#route-target both 3:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF4
(config-vrf)#rd 5.5.5.5:4
(config-vrf)#route-target both 4:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF5
(config-vrf)#rd 5.5.5.5:5
(config-vrf)#route-target both 5:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF6
(config-vrf)#rd 5.5.5.5:6
(config-vrf)#route-target both 6:2
(config-vrf)#commit
(config-vrf)#exit
(config)#mac vrf L2_VRF7
(config-vrf)#rd 5.5.5.5:7
(config-vrf)#route-target both 7:2
!
(config)#mac vrf L2_VRF8
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 5.5.5.5:8
(config-vrf)#route-target both 8:2
!
(config)#mac vrf L2_VRF9
(config-vrf)#rd 5.5.5.5:9
(config-vrf)#route-target both 9:2
(config-vrf)#commit
(config-vrf)#exit
4. Configure global VTEP IP.
(config)#nvo vxlan vtep-ip-global 5.5.5.5
5. Enter the NVO VXLAN instance sub-mode for each VNI and bind it to its MAC-VRF and optional IRB interface.
(config)#nvo vxlan id 1001 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF1
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1002 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF2
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1003 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF3
(config-nvo)#evpn irb1003
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1004 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF4
(config-nvo)#evpn irb1004
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1005 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF5
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1006 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF6
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1007 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF7
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1008 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF8
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1009 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF9
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1010 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF10
(config-nvo)#commit
(config-nvo)#exit
6. Configure interfaces.
(config)#interface po200
(config-if)#switchport
(config-if)#load-interval 30
(config-if)#evpn multi-homed system-mac 0000.9999.2222
(config-if)#commit
(config-if)#exit
(config)#interface cd3/1
(config-if)#switchport
(config-if)#load-interval 30
(config-if)#commit
(config-if)#exit
(config)#interface cd21/1
(config-if)#channel-group 200 mode active
(config-if)#commit
(config-if)#exit
(config)#interface irb1003
(config-if)#ip vrf forwarding L3_VRF1
(config-if)#evpn irb-if-forwarding anycast-gateway-mac
(config-if)#ip address 102.101.1.1/24 anycast
(config-if)#ipv6 address 102::1/64 anycast
(config-if)#commit
(config-if)#exit
(config)#interface irb1004
(config-if)#ip vrf forwarding L3_VRF1
(config-if)#ip address 202.101.1.1/24
(config-if)#ipv6 address 202::1/64
(config-if)#commit
(config-if)#exit
(config)#interface lo
(config-if)#ip address 127.0.0.1/8
(config-if)#ip address 5.5.5.5/32 secondary
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
(config)#interface xe33
(config-if)#ip address 50.1.1.1/24
(config-if)#commit
(config-if)#exit
(config)#interface xe34
(config-if)#load-interval 30
(config-if)#ip address 50.1.2.1/24
(config-if)#commit
(config-if)#exit
7. Configure OSPF underlay routing.
(config)#router ospf 100
(config-router)#ospf router-id 5.5.5.5
(config-router)#network 5.5.5.5/32 area 0.0.0.0
(config-router)#network 50.1.1.0/24 area 0.0.0.0
(config-router)#network 50.1.2.0/24 area 0.0.0.0
!
(config-router)#router bgp 65003
(config-router)#bgp router-id 5.5.5.5
(config-router)#neighbor 4.4.4.4 remote-as 65003
(config-router)#neighbor 4.4.4.4 update-source lo
(config-router)#neighbor 15.15.15.15 remote-as 65002
(config-router)#neighbor 15.15.15.15 ebgp-multihop
(config-router)#neighbor 15.15.15.15 update-source lo
(config-router)#neighbor 16.16.16.16 remote-as 65002
(config-router)#neighbor 16.16.16.16 ebgp-multihop
(config-router)#neighbor 16.16.16.16 update-source lo
8. Configure BGP L2VPN EVPN address family.
(config-router)#address-family l2vpn evpn
(config-router-af)#neighbor 4.4.4.4 activate
(config-router-af)#neighbor 15.15.15.15 activate
(config-router-af)#neighbor 16.16.16.16 activate
(config-router-af)#commit
(config-router-af)#exit-address-family
(config-router)#address-family ipv4 vrf L3_VRF1
(config-router-af)#max-paths ebgp 4
(config-router-af)#max-paths ibgp 4
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#commit
(config-router-af)#exit-address-family
(config-router)#address-family ipv6 vrf L3_VRF1
(config-router-af)#max-paths ebgp 4
(config-router-af)#max-paths ibgp 4
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#commit
(config-router-af)#exit-address-family
(config-router)#commit
(config-router)#exit
9. Disable the cache.
(config)#nvo vxlan max-cache-disable 5
10. Enter into VxLAN MH access-port with VLAN and map vnid to access interface.
(config)#nvo vxlan access-if port-vlan cd3/1 1001
(config-access-if)#map vnid 1001
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan cd3/1 1002
(config-access-if)#map vnid 1002
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan cd3/1 1003
(config-access-if)#map vnid 1003
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan cd3/1 1004
(config-access-if)#map vnid 1004
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan cd3/1 1005
(config-access-if)#map vnid 1005
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan cd3/1 1006
(config-access-if)#map vnid 1006
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan cd3/1 1007
(config-access-if)#map vnid 1007
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan cd3/1 1008
(config-access-if)#map vnid 1008
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan cd3/1 1009
(config-access-if)#map vnid 1009
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan cd3/1 1010
(config-access-if)#map vnid 1010
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po200 1001
(config-access-if)#map vnid 1001
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po200 1002
(config-access-if)#map vnid 1002
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po200 1003
(config-access-if)#map vnid 1003
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po200 1004
(config-access-if)#map vnid 1004
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po200 1005
(config-access-if)#map vnid 1005
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po200 1006
(config-access-if)#map vnid 1006
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po200 1007
(config-access-if)#map vnid 1007
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po200 1008
(config-access-if)#map vnid 1008
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po200 1009
(config-access-if)#map vnid 1009
(config-access-if)#commit
(config-access-if)#exit
(config)#nvo vxlan access-if port-vlan po200 1010
(config-access-if)#map vnid 1010
(config-access-if)#commit
(config-access-if)#exit
R1
1. Configure the LDP.
#configure terminal
(config)#router ldp
(config-router)#router-id 17.17.17.17
(config-router)#transport-address ipv4 17.17.17.17
(config-router)#commit
(config-router)#exit
2. Configure interfaces.
(config)#interface lo
(config-if)#ip address 127.0.0.1/8
(config-if)#ip address 17.17.17.17/32 secondary
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
(config)#interface xe2
(config-if)#load-interval 30
(config-if)#ip address 103.1.1.2/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
(config)#interface xe14
(config-if)#load-interval 30
(config-if)#ip address 106.1.1.2/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
(config)#interface xe16
(config-if)#load-interval 30
(config-if)#ip address 104.1.1.2/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
(config)#interface xe19
(config-if)#load-interval 30
(config-if)#ip address 105.1.1.2/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
3. Configure router.
(config)#router ospf 100
(config-router)#ospf router-id 17.17.17.17
(config-router)#network 17.17.17.17/32 area 0.0.0.1
(config-router)#network 103.1.1.0/24 area 0.0.0.1
(config-router)#network 104.1.1.0/24 area 0.0.0.1
(config-router)#network 105.1.1.0/24 area 0.0.0.1
(config-router)#network 106.1.1.0/24 area 0.0.0.1
(config-router)#commit
(config-router)#exit
R2
1. Configure LDP.
#configure terminal
(config)#router ldp
(config-router)#router-id 18.18.18.18
(config-router)#transport-address ipv4 18.18.18.18
(config-router)#commit
(config-router)#exit
2. Configure interfaces.
(config)#interface ce0
(config-if)#load-interval 30
(config-if)#ip address 103.1.2.2/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
(config)#interface lo
(config-if)#ip address 127.0.0.1/8
(config-if)#ip address 18.18.18.18/32 secondary
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
(config)#interface lo.management
(config-if)#ip vrf forwarding management
(config-if)#ip address 127.0.0.1/8
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
(config)#interface xe14
(config-if)#load-interval 30
(config-if)#ip address 106.1.2.2/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
(config)#interface xe16
(config-if)#load-interval 30
(config-if)#ip address 104.1.2.2/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
(config)#interface xe22
(config-if)#load-interval 30
(config-if)#ip address 105.1.2.2/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
3. Configure router.
(config)#router ospf 100
(config-router)#ospf router-id 18.18.18.18
(config-router)#network 18.18.18.18/32 area 0.0.0.1
(config-router)#network 103.1.2.0/24 area 0.0.0.1
(config-router)#network 104.1.2.0/24 area 0.0.0.1
(config-router)#network 105.1.2.0/24 area 0.0.0.1
(config-router)#network 106.1.2.0/24 area 0.0.0.1
SWITCH1
1. Configure bridge.
#configure terminal
(config)#bridge 1 protocol ieee vlan-bridge
2. Configure VLAN.
(config)#vlan database
(config-vlan)#vlan 1001-1010 bridge 1 state enable
3. Configure interfaces.
(config)#interface po100
(config-if)#switchport
(config-if)#bridge-group 1 spanning-tree disable
(config-if)#switchport mode trunk
(config-if)#switchport trunk allowed vlan add 1001-1010
(config-if)#load-interval 30
(config-if)#commit
(config-if)#exit
(config)#interface ce55
(config-if)#channel-group 100 mode active
(config-if)#commit
(config-if)#exit
(config)#interface ce56
(config-if)#channel-group 100 mode active
(config-if)#commit
(config-if)#exit
(config)#interface xe57
(config-if)#switchport
(config-if)#bridge-group 1 spanning-tree disable
(config-if)#switchport mode trunk
(config-if)#switchport trunk allowed vlan add 1001-1010
(config-if)#load-interval 30
(config-if)#commit
(config-if)#exit
SWITCH2
1. Configure bridge.
#configure terminal
(config)#bridge 1 protocol ieee vlan-bridge
2. Configure VALN.
(config)#vlan database
(config-valn)#vlan 1001-1010 bridge 1 state enable
(config-valn)#commit
(config-valn)#exit
3. Configure interfaces.
(config)#interface po200
(config-if)#switchport
(config-if)#bridge-group 1 spanning-tree disable
(config-if)#switchport mode trunk
(config-if)#switchport trunk allowed vlan add 1001-1010
(config-if)#load-interval 30
(config-if)#commit
(config-if)#exit
(config)#interface xe19
(config-if)#channel-group 200 mode active
(config-if)#commit
(config-if)#exit
(config)#interface xe51/1
(config-if)#channel-group 200 mode active
(config-if)#commit
(config-if)#exit
(config)#interface xe57
(config-if)#switchport
(config-if)#bridge-group 1 spanning-tree disable
(config-if)#switchport mode trunk
(config-if)#switchport trunk allowed vlan add 1001-1010
(config-if)#load-interval 30
(config-if)#commit
(config-if)#exit
SPINE1
1. Configure interfaces.
#configure terminal
(config)#interface ce1/2
(config-if)#load-interval 30
(config-if)#ip address 20.1.1.2/24
(config-if)#commit
(config-if)#exit
(config)#interface ce2/1
(config-if)#ip address 10.1.1.2/24
(config-if)#commit
(config-if)#exit
(config)#interface ce3/1
(config-if)#load-interval 30
(config-if)#ip address 101.1.1.1/24
(config-if)#commit
(config-if)#exit
(config)#interface ce21/1
(config-if)#load-interval 30
(config-if)#ip address 101.1.2.1/24
(config-if)#commit
(config-if)#exit
(config)#interface lo
(config-if)#ip address 127.0.0.1/8
(config-if)#ip address 11.11.11.11/32 secondary
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
2. Configure router.
(config)#router ospf 100
(config-router)#ospf router-id 11.11.11.11
(config-router)#network 10.1.1.0/24 area 0.0.0.0
(config-router)#network 11.11.11.11/32 area 0.0.0.0
(config-router)#network 20.1.1.0/24 area 0.0.0.0
(config-router)#network 101.1.1.0/24 area 0.0.0.0
(config-router)#network 101.1.2.0/24 area 0.0.0.0
(config-router)#commit
(config-router)#exit
SPINE2
1. Configure interfaces.
(config)#interface ce1/1
(config-if)#load-interval 30
(config-if)#ip address 10.1.2.2/24
(config-if)#commit
(config-if)#exit
(config)#interface ce2/1
(config-if)#load-interval 30
(config-if)#ip address 20.1.2.2/24
(config-if)#commit
(config-if)#exit
(config)#interface ce3/1
(config-if)#load-interval 30
(config-if)#ip address 102.1.1.1/24
(config-if)#commit
(config-if)#exit
(config)#interface ce4/1
(config-if)#load-interval 30
(config-if)#ip address 102.1.2.1/24
(config-if)#commit
(config-if)#exit
(config)#interface lo
(config-if)#ip address 127.0.0.1/8
(config-if)#ip address 12.12.12.12/32 secondary
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
2. Configure router.
(config)#router ospf 100
(config-router)#ospf router-id 12.12.12.12
(config-router)#network 10.1.2.0/24 area 0.0.0.0
(config-router)#network 12.12.12.12/32 area 0.0.0.0
(config-router)#network 20.1.2.0/24 area 0.0.0.0
(config-router)#network 102.1.1.0/24 area 0.0.0.0
(config-router)#network 102.1.2.0/24 area 0.0.0.0
(config-router)#commit
(config-router)#exit
SPINE4
1. Configure interfaces.
(config)#interface ce25
(config-if)#ip address 90.1.2.1/24
(config-if)#commit
(config-if)#exit
(config)#interface ce27
(config-if)#ip address 90.1.1.1/24
(config-if)#commit
(config-if)#exit
(config)#interface lo
(config-if)#ip address 127.0.0.1/8
(config-if)#ip address 9.9.9.9/32 secondary
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
(config)#interface xe1/1
(config-if)#ip address 50.1.1.2/24
(config-if)#commit
(config-if)#exit
(config)#interface xe31/1
(config-if)#ip address 40.1.1.2/24
(config-if)#commit
(config-if)#exit
2. Configure router.
(config)#router ospf 100
(config-router)#ospf router-id 9.9.9.9
(config-router)#network 9.9.9.9/32 area 0.0.0.0
(config-router)#network 40.1.1.0/24 area 0.0.0.0
(config-router)#network 50.1.1.0/24 area 0.0.0.0
(config-router)#network 90.1.1.0/24 area 0.0.0.0
(config-router)#network 90.1.2.0/24 area 0.0.0.0
(config-router)#commit
(config-router)#exit
SPINE5
1. Configure interfaces.
(config)#interface ce25
(config-if)#load-interval 30
(config-if)#ip address 100.1.2.1/24
(config-if)#commit
(config-if)#exit
(config)#interface ce27
(config-if)#load-interval 30
(config-if)#ip address 100.1.1.1/24
(config-if)#commit
(config-if)#exit
(config)#interface lo
(config-if)#ip address 127.0.0.1/8
(config-if)#ip address 10.10.10.10/32 secondary
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
(config)#interface xe1/1
(config-if)#load-interval 30
(config-if)#ip address 50.1.2.2/24
(config-if)#commit
(config-if)#exit
(config)#interface xe31/1
(config-if)#load-interval 30
(config-if)#ip address 40.1.2.2/24
(config-if)#commit
(config-if)#exit
2. Configure router.
(config)#router ospf 100
(config-router)#ospf router-id 10.10.10.10
(config-router)#network 10.10.10.10/32 area 0.0.0.0
(config-router)#network 40.1.2.0/24 area 0.0.0.0
(config-router)#network 50.1.2.0/24 area 0.0.0.0
(config-router)#network 100.1.1.0/24 area 0.0.0.0
(config-router)#network 100.1.2.0/24 area 0.0.0.0
(config-router)#commit
(config-router)#exit
BLEAF1
1. Configure GW VTEP IP.
(config)#evpn interconnect-mh gw-vtep-ip vxlan 14.14.14.14 mpls 24.24.24.24
Note: Configure this command before enabling other multihoming parameters (multi-homed iesi / MH enables). It is mandatory for EVPN interconnect multihoming; omitting or removing it causes forwarding loops, traffic duplication, and flood suppression failures. If applied after initial peering, run clear ip bgp * to reclassify peer-GW routes into their respective DC/WAN domains.
2. Enable hardware filter profiles.
(config)#hardware-profile filter evpn-arp-nd enable
(config)#hardware-profile filter vxlan-mh enable
(config)#hardware-profile filter evpn-mpls-mh enable
(config)#hardware-profile filter evpn-stitch enable
3. Enable VXLAN and IRB and EVPN VXLAN multihoming.
(config)#nvo vxlan enable
(config)#nvo vxlan irb
(config)#evpn mpls enable
(config)#evpn vxlan multihoming enable
(config)#evpn irb-forwarding anycast-gateway-mac 0000.0002.abcd
(config)#evpn mpls multihoming enable
4. Configure L3 VRF with EVPN interconnecting and enable EVPN interconnecting.
(config)#ip vrf L3_VRF1
(config-vrf)#rd 13.13.13.13:101
(config-vrf)#route-target both 100:1
(config-vrf)#l3vni 1000
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 13.13.13.13:951
(config-vrf-evpn)#route-target both 951:1
(config-vrf-evpn)#host-route-extend-l2vni 1001-1002
(config-vrf-evpn)#commit
(config-vrf-evpn)#exit-config-vrf-evpn-mode
5. Configure MAC VRF.
(config)#mac vrf L2_VRF1
(config-vrf)#rd 13.13.13.13:1
(config-vrf)#route-target both 1:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 13.13.13.13:901
(config-vrf-evpn)#route-target both 901:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:11:11:11:11:11:11:11 all-active
(config-vrf-evpn)#commit
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF10
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 13.13.13.13:10
(config-vrf)#route-target both 10:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 13.13.13.13:910
(config-vrf-evpn)#route-target both 910:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:99:11:11:11:11:11:11 all-active
(config-vrf-evpn)#commit
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF2
(config-vrf)#rd 13.13.13.13:2
(config-vrf)#route-target both 2:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 13.13.13.13:902
(config-vrf-evpn)#route-target both 902:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:22:11:11:11:11:11:11 all-active
(config-vrf-evpn)#commit
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF3
(config-vrf)#rd 13.13.13.13:3
(config-vrf)#route-target both 3:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 13.13.13.13:903
(config-vrf-evpn)#route-target both 903:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:33:11:11:11:11:11:11 all-active
(config-vrf-evpn)#commit
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF4
(config-vrf)#rd 13.13.13.13:4
(config-vrf)#route-target both 4:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 13.13.13.13:904
(config-vrf-evpn)#route-target both 904:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:44:11:11:11:11:11:11 all-active
(config-vrf-evpn)#commit
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF5
(config-vrf)#rd 13.13.13.13:5
(config-vrf)#route-target both 5:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 13.13.13.13:905
(config-vrf-evpn)#route-target both 905:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:55:11:11:11:11:11:11 all-active
(config-vrf-evpn)#commit
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF6
(config-vrf)#rd 13.13.13.13:6
(config-vrf)#route-target both 6:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 13.13.13.13:906
(config-vrf-evpn)#route-target both 906:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:66:11:11:11:11:11:11 all-active
(config-vrf-evpn)#commit
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF7
(config-vrf)#rd 13.13.13.13:7
(config-vrf)#route-target both 7:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 13.13.13.13:907
(config-vrf-evpn)#route-target both 907:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:77:11:11:11:11:11:11 all-active
(config-vrf-evpn)#commit
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF8
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 13.13.13.13:8
(config-vrf)#route-target both 8:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 13.13.13.13:908
(config-vrf-evpn)#route-target both 908:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:88:11:11:11:11:11:11 all-active
(config-vrf-evpn)#commit
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF9
(config-vrf)#rd 13.13.13.13:9
(config-vrf)#route-target both 9:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 13.13.13.13:909
(config-vrf-evpn)#route-target both 909:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:99:11:11:11:11:11:11 all-active
(config-vrf-evpn)#commit
(config-vrf-evpn)#exit-config-vrf-evpn-mode
6. Configure global VTEP IP.
(config)#nvo vxlan vtep-ip-global 13.13.13.13
7. Configure NVO VXLAN.
(config)#nvo vxlan id 1001 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF1
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1002 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF2
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1003 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF3
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1004 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF4
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1005 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF5
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1006 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF6
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1007 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF7
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1008 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF8
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1009 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF9
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1010 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF10
(config-nvo)#commit
(config-nvo)#exit
8. Configure global MPLS VTEP source.
(config)#evpn mpls vtep-ip-global 23.23.23.23
9. Configure EVPN MPLS instance stitched to VXLAN VNI under L2_VRF.
(config)#evpn mpls id 100001 interconnect-vnid 1001
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF1
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100002 interconnect-vnid 1002
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF2
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100003 interconnect-vnid 1003
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF3
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100004 interconnect-vnid 1004
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF4
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100005 control-word interconnect-vnid 1005
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF5
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100006 interconnect-vnid 1006
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF6
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100007 flow-label interconnect-vnid 1007
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF7
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100008 control-word flow-label interconnect-vnid 1008
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF8
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100009 interconnect-vnid 1009
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF9
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100010 interconnect-vnid 1010
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF10
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
10. Configure LDP.
(config)#router ldp
(config-router)#router-id 13.13.13.13
(config-router)#transport-address ipv4 13.13.13.13
(config-router)#targeted-peer ipv4 14.14.14.14
(config-router-targeted-peer)#exit-targeted-peer-mode
(config-router)#targeted-peer ipv4 15.15.15.15
(config-router-targeted-peer)#exit-targeted-peer-mode
(config-router)#targeted-peer ipv4 16.16.16.16
(config-router-targeted-peer)#exit-targeted-peer-mode
.(config-router)#commit
(config-router)#exit
11. Configure interfaces.
(config)#interface ce4/4
(config-if)#load-interval 30
(config-if)#commit
(config-if)#exit
(config)#interface ce4/4.1001 switchport
(config-if)#encapsulation dot1q 1001
(config-if)#rewrite pop
(config-if)#load-interval 30
(config-if)#access-if-evpn
(config-access-if)#map vpn-id 1001
(config-access-if)#commit
(config-access-if)#exit
(config)#interface ce4/4.1002 switchport
(config-if)#encapsulation dot1q 1002
(config-if)#rewrite pop
(config-if)#load-interval 30
(config-if)#access-if-evpn
(config-access-if)#map vpn-id 1002
(config-access-if)#commit
(config-access-if)#exit
(config)#interface ce4/4.1003 switchport
(config-if)#encapsulation dot1q 1003
(config-if)#rewrite pop
(config-if)#load-interval 30
(config-if)#access-if-evpn
(config-access-if)#map vpn-id 1003
(config-access-if)#commit
(config-access-if)#exit
(config)#interface ce4/4.1004 switchport
(config-if)#encapsulation dot1q 1004
(config-if)#rewrite pop
(config-if)#load-interval 30
(config-if)#access-if-evpn
(config-access-if)#map vpn-id 1004
(config-access-if)#commit
(config-access-if)#exit
(config)#interface ce4/4.1005 switchport
(config-if)#encapsulation dot1q 1005
(config-if)#rewrite pop
(config-if)#load-interval 30
(config-if)#access-if-evpn
(config-access-if)#map vpn-id 1005
(config-access-if)#commit
(config-access-if)#exit
(config)#interface ce4/4.1006 switchport
(config-if)#encapsulation dot1q 1006
(config-if)#rewrite pop
(config-if)#load-interval 30
(config-if)#access-if-evpn
(config-access-if)#map vpn-id 1006
(config-access-if)#commit
(config-access-if)#exit
(config)#interface ce4/4.1007 switchport
(config-if)#encapsulation dot1q 1007
(config-if)#rewrite pop
(config-if)#load-interval 30
(config-if)#access-if-evpn
(config-access-if)#map vpn-id 1007
(config-access-if)#commit
(config-access-if)#exit
(config)#interface ce4/4.1008 switchport
(config-if)#encapsulation dot1q 1008
(config-if)#rewrite pop
(config-if)#load-interval 30
(config-if)#access-if-evpn
(config-access-if)#map vpn-id 1008
(config-access-if)#commit
(config-access-if)#exit
(config)#interface ce4/4.1009 switchport
(config-if)#encapsulation dot1q 1009
(config-if)#rewrite pop
(config-if)#load-interval 30
(config-if)#access-if-evpn
(config-access-if)#map vpn-id 1009
(config-access-if)#commit
(config-access-if)#exit
(config)#interface ce4/4.1010 switchport
(config-if)#encapsulation dot1q 1010
(config-if)#rewrite pop
(config-if)#load-interval 30
(config-if)#access-if-evpn
(config-access-if)#map vpn-id 1010
(config-access-if)#commit
(config-access-if)#exit
(config)#interface ce12
(config-if)#load-interval 30
(config-if)#ip address 103.1.2.1/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
(config)#interface ce21
(config-if)#load-interval 30
(config-if)#ip address 102.1.1.2/24
(config-if)#commit
(config-if)#exit
(config)#interface ce22
(config-if)#load-interval 30
(config-if)#ip address 101.1.1.2/24
(config-if)#commit
(config-if)#exit
(config)#interface lo
(config-if)#ip address 127.0.0.1/8
(config-if)#ip address 13.13.13.13/32 secondary
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
(config)#interface loopback1
(config-if)#ip address 23.23.23.23/32 secondary
(config-if)#commit
(config-if)#exit
(config)#interface xe2
(config-if)#load-interval 30
(config-if)#ip address 103.1.1.1/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
12. Configure router OSPF.
(config)#router ospf 100
(config-router)#ospf router-id 13.13.13.13
(config-router)#network 13.13.13.13/32 area 0.0.0.0
(config-router)#network 23.23.23.23/32 area 0.0.0.1
(config-router)#network 101.1.1.0/24 area 0.0.0.0
(config-router)#network 102.1.1.0/24 area 0.0.0.0
(config-router)#network 103.1.1.0/24 area 0.0.0.1
(config-router)#network 103.1.2.0/24 area 0.0.0.1
(config-router)#commit
(config-router)#exit
13. Configure router BGP.
(config)#router bgp 65002
(config-router)#bgp router-id 13.13.13.13
(config-router)#bgp bestpath domain-path-id
(config-router)#bgp domain-path-id ipvpn 2323:23
(config-router)#bgp domain-path-id evpn 2324:24
(config-router)#bgp domain-path-id local 2325:25
(config-router)#neighbor 1.1.1.1 remote-as 65001
(config-router)#neighbor 1.1.1.1 ebgp-multihop
(config-router)#neighbor 1.1.1.1 update-source lo
(config-router)#neighbor 2.2.2.2 remote-as 65001
(config-router)#neighbor 2.2.2.2 ebgp-multihop
(config-router)#neighbor 2.2.2.2 update-source lo
(config-router)#neighbor 24.24.24.24 remote-as 65002
(config-router)#neighbor 24.24.24.24 update-source loopback1
(config-router)#neighbor 25.25.25.25 remote-as 65002
(config-router)#neighbor 25.25.25.25 update-source loopback1
(config-router)#neighbor 26.26.26.26 remote-as 65002
(config-router)#neighbor 26.26.26.26 update-source loopback1
(config-router)#address-family ipv4 unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#exit-address-family
(config-router)#address-family vpnv4 unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths install
(config-router-af)#multi-path
(config-router-af)#neighbor 24.24.24.24 activate
(config-router-af)#neighbor 24.24.24.24 peer-type fabric-external
(config-router-af)#neighbor 24.24.24.24 allowas-in 1
(config-router-af)#neighbor 25.25.25.25 activate
(config-router-af)#neighbor 25.25.25.25 peer-type fabric-external
(config-router-af)#neighbor 25.25.25.25 allowas-in 1
(config-router-af)#neighbor 26.26.26.26 activate
(config-router-af)#neighbor 26.26.26.26 peer-type fabric-external
(config-router-af)#neighbor 26.26.26.26 allowas-in 1
(config-router-af)#exit-address-family
(config-router)#address-family l2vpn evpn
(config-router-af)#neighbor 1.1.1.1 activate
(config-router-af)#neighbor 2.2.2.2 activate
(config-router-af)#neighbor 24.24.24.24 activate
(config-router-af)#neighbor 24.24.24.24 peer-type fabric-external
(config-router-af)#neighbor 24.24.24.24 allowas-in 1
(config-router-af)#neighbor 25.25.25.25 activate
(config-router-af)#neighbor 25.25.25.25 peer-type fabric-external
(config-router-af)#neighbor 25.25.25.25 allowas-in 1
(config-router-af)#neighbor 26.26.26.26 activate
(config-router-af)#neighbor 26.26.26.26 peer-type fabric-external
(config-router-af)#neighbor 26.26.26.26 allowas-in 1
(config-router-af)#exit-address-family
(config-router)#address-family vpnv6 unicast
(config-router-af)#multi-path
(config-router-af)#neighbor 24.24.24.24 activate
(config-router-af)#neighbor 24.24.24.24 peer-type fabric-external
(config-router-af)#neighbor 24.24.24.24 allowas-in 1
(config-router-af)#neighbor 25.25.25.25 activate
(config-router-af)#neighbor 25.25.25.25 peer-type fabric-external
(config-router-af)#neighbor 25.25.25.25 allowas-in 1
(config-router-af)#neighbor 26.26.26.26 activate
(config-router-af)#neighbor 26.26.26.26 peer-type fabric-external
(config-router-af)#neighbor 26.26.26.26 allowas-in 1
(config-router-af)#exit-address-family
(config-router)#address-family ipv4 vrf L3_VRF1
(config-router-af)#max-paths ibgp 4
(config-router-af)#re-originate vpnv4-unicast as l2vpn-evpn
(config-router-af)#re-originate l2vpn-evpn as vpnv4-unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#exit-address-family
(config-router)#address-family ipv6 vrf L3_VRF1
(config-router-af)#max-paths ibgp 4
(config-router-af)#re-originate vpnv6-unicast as l2vpn-evpn
(config-router-af)#re-originate l2vpn-evpn as vpnv6-unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#exit-address-family
(config-router)#commit
(config-router)#exit
BLEAF2
1. Configure GW VTEP IP.
(config)#evpn interconnect-mh gw-vtep-ip vxlan 13.13.13.13 mpls 23.23.23.23
Note: Configure this command before enabling other multihoming parameters (multi-homed iesi / MH enables). It is mandatory for EVPN interconnect multihoming; omitting or removing it causes forwarding loops, traffic duplication, and flood suppression failures. If applied after initial peering, run clear ip bgp * to reclassify peer-GW routes into their respective DC/WAN domains.
2. Enable hardware filter profiles.
(config)#hardware-profile filter evpn-arp-nd enable
(config)#hardware-profile filter vxlan-mh enable
(config)#hardware-profile filter evpn-mpls-mh enable
(config)#hardware-profile filter evpn-stitch enable
3. Enable VXLAN and IRB and EVPN VXLAN multihoming.
(config)#nvo vxlan enable
(config)#nvo vxlan irb
(config)#evpn mpls enable
(config)#evpn vxlan multihoming enable
(config)#evpn irb-forwarding anycast-gateway-mac 0000.0002.abcd
(config)#evpn mpls multihoming enable
4. Configure L3 VRF with EVPN interconnecting and enable EVPN interconnecting.
(config)#ip c L3_VRF1
(config-vrf)#rd 14.14.14.14:101
(config-vrf)#route-target both 100:1
(config-vrf)#l3vni 1000
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 14.14.14.14:951
(config-vrf-evpn)#route-target both 951:1
(config-vrf-evpn)#host-route-extend-l2vni 1001-1002
(config-vrf-evpn)#exit-config-vrf-evpn-mode
5. Configure MAC VRF.
(config)#mac vrf L2_VRF1
(config-vrf)#rd 14.14.14.14:1
(config-vrf)#route-target both 1:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 14.14.14.14:901
(config-vrf-evpn)#route-target both 901:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:11:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF10
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 14.14.14.14:10
(config-vrf)#route-target both 10:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 14.14.14.14:910
(config-vrf-evpn)#route-target both 910:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:99:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF2
(config-vrf)#rd 14.14.14.14:2
(config-vrf)#route-target both 2:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 14.14.14.14:902
(config-vrf-evpn)#route-target both 902:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:22:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF3
(config-vrf)#rd 14.14.14.14:3
(config-vrf)#route-target both 3:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 14.14.14.14:903
(config-vrf-evpn)#route-target both 903:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:33:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF4
(config-vrf)#rd 14.14.14.14:4
(config-vrf)#route-target both 4:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 14.14.14.14:904
(config-vrf-evpn)#route-target both 904:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:44:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF5
(config-vrf)#rd 14.14.14.14:5
(config-vrf)#route-target both 5:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 14.14.14.14:905
(config-vrf-evpn)#route-target both 905:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:55:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF6
(config-vrf)#rd 14.14.14.14:6
(config-vrf)#route-target both 6:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 14.14.14.14:906
(config-vrf-evpn)#route-target both 906:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:66:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF7
(config-vrf)#rd 14.14.14.14:7
(config-vrf)#route-target both 7:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 14.14.14.14:907
(config-vrf-evpn)#route-target both 907:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:77:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF8
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 14.14.14.14:8
(config-vrf)#route-target both 8:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 14.14.14.14:908
(config-vrf-evpn)#route-target both 908:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:88:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF9
(config-vrf)#rd 14.14.14.14:9
(config-vrf)#route-target both 9:1
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 14.14.14.14:909
(config-vrf-evpn)#route-target both 909:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:11:99:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
6. Configure global VTEP IP.
(config)#nvo vxlan vtep-ip-global 14.14.14.14
7. Configure NVO VXLAN.
(config)#nvo vxlan id 1001 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF1
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1002 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF2
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1003 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF3
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1004 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF4
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1005 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF5
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1006 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF6
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1007 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF7
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1008 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF8
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1009 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF9
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1010 ingress-replication
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF10
(config-nvo)#commit
(config-nvo)#exit
8. Configure global MPLS VTEP source.
(config)#evpn mpls vtep-ip-global 24.24.24.24
9. Configure EVPN MPLS instance stitched to VXLAN VNI under L2_VRF.
(config)#evpn mpls id 100001 interconnect-vnid 1001
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF1
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100002 interconnect-vnid 1002
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF2
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100003 interconnect-vnid 1003
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF3
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100004 interconnect-vnid 1004
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF4
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100005 control-word interconnect-vnid 1005
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF5
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100006 interconnect-vnid 1006
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF6
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100007 flow-label interconnect-vnid 1007
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF7
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100008 control-word flow-label interconnect-vnid 1008
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF8
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100009 interconnect-vnid 1009
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF9
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100010 interconnect-vnid 1010
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF10
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
10. Configure router LDP.
(config)#router ldp
(config-router)#router-id 14.14.14.14
(config-router)#transport-address ipv4 14.14.14.14
(config-router)#targeted-peer ipv4 13.13.13.13
(config-router-targeted-peer)#exit-targeted-peer-mode
(config-router)#targeted-peer ipv4 15.15.15.15
(config-router-targeted-peer)#exit-targeted-peer-mode
(config-router)#targeted-peer ipv4 16.16.16.16
(config-router-targeted-peer)#exit-targeted-peer-mode
11. Configure interfaces.
(config)#interface ce1
(config-if)#load-interval 30
(config-if)#ip address 101.1.2.2/24
(config-if)#commit
(config-if)#exit
(config)#interface ce4
(config-if)#load-interval 30
(config-if)#ip address 102.1.2.2/24
(config-if)#commit
(config-if)#exit
(config)#interface lo
(config-if)#ip address 127.0.0.1/8
(config-if)#ip address 14.14.14.14/32 secondary
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
(config)#interface loopback1
(config-if)#ip address 24.24.24.24/32 secondary
(config-if)#commit
(config-if)#exit
(config)#interface xe47
(config-if)#load-interval 30
(config-if)#ip address 104.1.2.1/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
(config)#interface xe48
(config-if)#load-interval 30
(config-if)#ip address 104.1.1.1/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
12. Configure router OSPF.
(config)#router ospf 100
(config-router)#ospf router-id 14.14.14.14
(config-router)#network 14.14.14.14/32 area 0.0.0.0
(config-router)#network 24.24.24.24/32 area 0.0.0.1
(config-router)#network 101.1.2.0/24 area 0.0.0.0
(config-router)#network 102.1.2.0/24 area 0.0.0.0
(config-router)#network 104.1.1.0/24 area 0.0.0.1
(config-router)#network 104.1.2.0/24 area 0.0.0.1
(config-router)#commit
(config-router)#exit
13. Configure router BGP.
(config)#router bgp 65002
(config-router)#bgp router-id 14.14.14.14
(config-router)#bgp bestpath domain-path-id
(config-router)#bgp domain-path-id ipvpn 2323:23
(config-router)#bgp domain-path-id evpn 2324:24
(config-router)#bgp domain-path-id local 2326:26
(config-router)#neighbor 1.1.1.1 remote-as 65001
(config-router)#neighbor 1.1.1.1 ebgp-multihop
(config-router)#neighbor 1.1.1.1 update-source lo
(config-router)#neighbor 2.2.2.2 remote-as 65001
(config-router)#neighbor 2.2.2.2 ebgp-multihop
(config-router)#neighbor 2.2.2.2 update-source lo
(config-router)#neighbor 23.23.23.23 remote-as 65002
(config-router)#neighbor 23.23.23.23 update-source loopback1
(config-router)#neighbor 25.25.25.25 remote-as 65002
(config-router)#neighbor 25.25.25.25 update-source loopback1
(config-router)#neighbor 26.26.26.26 remote-as 65002
(config-router)#neighbor 26.26.26.26 update-source loopback1
(config-router-af)#address-family ipv4 unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#exit-address-family
(config-router)#address-family vpnv4 unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths install
(config-router-af)#multi-path
(config-router-af)#neighbor 23.23.23.23 activate
(config-router-af)#neighbor 23.23.23.23 peer-type fabric-external
(config-router-af)#neighbor 23.23.23.23 allowas-in 1
(config-router-af)#neighbor 25.25.25.25 activate
(config-router-af)#neighbor 25.25.25.25 peer-type fabric-external
(config-router-af)#neighbor 25.25.25.25 allowas-in 1
(config-router-af)#neighbor 26.26.26.26 activate
(config-router-af)#neighbor 26.26.26.26 peer-type fabric-external
(config-router-af)#neighbor 26.26.26.26 allowas-in 1
(config-router-af)#exit-address-family
(config-router)#address-family l2vpn evpn
(config-router-af)#neighbor 1.1.1.1 activate
(config-router-af)#neighbor 2.2.2.2 activate
(config-router-af)#neighbor 23.23.23.23 activate
(config-router-af)#neighbor 23.23.23.23 peer-type fabric-external
(config-router-af)#neighbor 23.23.23.23 allowas-in 1
(config-router-af)#neighbor 25.25.25.25 activate
(config-router-af)#neighbor 25.25.25.25 peer-type fabric-external
(config-router-af)#neighbor 25.25.25.25 allowas-in 1
(config-router-af)#neighbor 26.26.26.26 activate
(config-router-af)#neighbor 26.26.26.26 peer-type fabric-external
(config-router-af)#neighbor 26.26.26.26 allowas-in 1
(config-router-af)#exit-address-family
(config-router)#address-family vpnv6 unicast
(config-router-af)#multi-path
(config-router-af)#neighbor 23.23.23.23 activate
(config-router-af)#neighbor 23.23.23.23 peer-type fabric-external
(config-router-af)#neighbor 23.23.23.23 allowas-in 1
(config-router-af)#neighbor 25.25.25.25 activate
(config-router-af)#neighbor 25.25.25.25 peer-type fabric-external
(config-router-af)#neighbor 25.25.25.25 allowas-in 1
(config-router-af)#neighbor 26.26.26.26 activate
(config-router-af)#neighbor 26.26.26.26 peer-type fabric-external
(config-router-af)#neighbor 26.26.26.26 allowas-in 1
(config-router-af)#exit-address-family
(config-router)#address-family ipv4 vrf L3_VRF1
(config-router-af)#max-paths ibgp 4
(config-router-af)#re-originate vpnv4-unicast as l2vpn-evpn
(config-router-af)#re-originate l2vpn-evpn as vpnv4-unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#exit-address-family
(config-router)#address-family ipv6 vrf L3_VRF1
(config-router-af)#max-paths ibgp 4
(config-router-af)#re-originate vpnv6-unicast as l2vpn-evpn
(config-router-af)#re-originate l2vpn-evpn as vpnv6-unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#exit-address-family
(config-router)#commit
(config-router)#exit
BLEAF3
1. Configure GW VTEP IP.
(config)#evpn interconnect-mh gw-vtep-ip vxlan 16.16.16.16 mpls 26.26.26.26
Note: Configure this command before enabling other multihoming parameters (multi-homed iesi / MH enables). It is mandatory for EVPN interconnect multihoming; omitting or removing it causes forwarding loops, traffic duplication, and flood suppression failures. If applied after initial peering, run clear ip bgp * to reclassify peer-GW routes into their respective DC/WAN domains.
2. Enable hardware filter profiles.
(config)#hardware-profile filter evpn-arp-nd enable
(config)#hardware-profile filter vxlan-mh enable
(config)#hardware-profile filter evpn-mpls-mh enable
(config)#hardware-profile filter evpn-stitch enable
3. Enable VXLAN and IRB and EVPN VXLAN multihoming.
(config)#nvo vxlan enable
(config)#nvo vxlan irb
(config)#evpn mpls enable
(config)#evpn vxlan multihoming enable
(config)#evpn irb-forwarding anycast-gateway-mac 0000.0003.abcd
(config)#evpn mpls multihoming enable
4. Configure L3 VRF with EVPN interconnecting and enable EVPN interconnecting.
(config)#ip vrf L3_VRF1
(config-vrf)#rd 15.15.15.15:101
(config-vrf)#route-target both 100:2
(config-vrf)#l3vni 1000
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 15.15.15.15:951
(config-vrf-evpn)#route-target both 951:1
(config-vrf-evpn)#host-route-extend-l2vni 1003-1004
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF1
(config-vrf)#rd 15.15.15.15:1
(config-vrf)#route-target both 1:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 15.15.15.15:901
(config-vrf-evpn)#route-target both 901:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:11:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF10
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 15.15.15.15:10
(config-vrf)#route-target both 10:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 15.15.15.15:910
(config-vrf-evpn)#route-target both 910:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:99:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF2
(config-vrf)#rd 15.15.15.15:2
(config-vrf)#route-target both 2:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 15.15.15.15:902
(config-vrf-evpn)#route-target both 902:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:22:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF3
(config-vrf)#rd 15.15.15.15:3
(config-vrf)#route-target both 3:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 15.15.15.15:903
(config-vrf-evpn)#route-target both 903:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:33:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF4
(config-vrf)#rd 15.15.15.15:4
(config-vrf)#route-target both 4:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 15.15.15.15:904
(config-vrf-evpn)#route-target both 904:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:44:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF5
(config-vrf)#rd 15.15.15.15:5
(config-vrf)#route-target both 5:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 15.15.15.15:905
(config-vrf-evpn)#route-target both 905:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:55:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF6
(config-vrf)#rd 15.15.15.15:6
(config-vrf)#route-target both 6:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 15.15.15.15:906
(config-vrf-evpn)#route-target both 906:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:66:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF7
(config-vrf)#rd 15.15.15.15:7
(config-vrf)#route-target both 7:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 15.15.15.15:907
(config-vrf-evpn)#route-target both 907:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:77:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF8
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 15.15.15.15:8
(config-vrf)#route-target both 8:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 15.15.15.15:908
(config-vrf-evpn)#route-target both 908:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:88:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF9
(config-vrf)#rd 15.15.15.15:9
(config-vrf)#route-target both 9:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 15.15.15.15:909
(config-vrf-evpn)#route-target both 909:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:99:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
5. Configure global VTEP IP.
(config)#nvo vxlan vtep-ip-global 15.15.15.15
6. Configure NVO VXLAN.
(config)#nvo vxlan id 1001 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF1
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1002 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF2
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1003 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF3
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1004 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF4
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1005 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF5
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1006 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF6
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1007 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF7
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1008 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF8
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1009 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF9
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1010 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF10
(config-nvo)#commit
(config-nvo)#exit
7. Configure global MPLS VTEP source.
(config)#evpn mpls vtep-ip-global 25.25.25.25
8. Configure EVPN MPLS instance stitched to VXLAN VNI under L2_VRF.
(config)#evpn mpls id 100001 interconnect-vnid 1001
(config-evpn)#host-reachability-protocol evpn-bgp L2_VRF1
(config-evpn)#commit
(config-evpn)#exit
(config)#evpn mpls id 100002 interconnect-vnid 1002
(config-evpn)#host-reachability-protocol evpn-bgp L2_VRF2
(config-evpn)#commit
(config-evpn)#exit
(config)#evpn mpls id 100003 interconnect-vnid 1003
(config-evpn)#host-reachability-protocol evpn-bgp L2_VRF3
(config-evpn)#commit
(config-evpn)#exit
(config)#evpn mpls id 100004 interconnect-vnid 1004
(config-evpn)#host-reachability-protocol evpn-bgp L2_VRF4
(config-evpn)#commit
(config-evpn)#exit
(config)#evpn mpls id 100005 control-word interconnect-vnid 1005
(config-evpn)#host-reachability-protocol evpn-bgp L2_VRF5
(config-evpn)#commit
(config-evpn)#exit
(config)#evpn mpls id 100006 interconnect-vnid 1006
(config-evpn)#host-reachability-protocol evpn-bgp L2_VRF6
(config-evpn)#commit
(config-evpn)#exit
(config)#evpn mpls id 100007 flow-label interconnect-vnid 1007
(config-evpn)#host-reachability-protocol evpn-bgp L2_VRF7
(config-evpn)#commit
(config-evpn)#exit
(config)#evpn mpls id 100008 control-word flow-label interconnect-vnid 1008
(config-evpn)#host-reachability-protocol evpn-bgp L2_VRF8
(config-evpn)#commit
(config-evpn)#exit
(config)#evpn mpls id 100009 interconnect-vnid 1009
(config-evpn)#host-reachability-protocol evpn-bgp L2_VRF9
(config-evpn)#commit
(config-evpn)#exit
(config)#evpn mpls id 100010 interconnect-vnid 1010
(config-evpn)#host-reachability-protocol evpn-bgp L2_VRF10
(config-evpn)#commit
(config-evpn)#exit
9. Configure LDP.
(config)#router ldp
(config-router)#router-id 15.15.15.15
(config-router)#transport-address ipv4 15.15.15.15
(config-router)#targeted-peer ipv4 13.13.13.13
(config-router-targeted-peer)#exit-targeted-peer-mode
(config-router)#targeted-peer ipv4 14.14.14.14
(config-router-targeted-peer)#exit-targeted-peer-mode
(config-router)#targeted-peer ipv4 16.16.16.16
(config-router-targeted-peer)#exit-targeted-peer-mode
10. Configure interfaces.
(config)#interface ce2
(config-if)#load-interval 30
(config-if)#ip address 90.1.1.2/24
(config-if)#commit
(config-if)#exit
(config)#interface ce4
(config-if)#load-interval 30
(config-if)#ip address 100.1.1.2/24
(config-if)#commit
(config-if)#exit
(config)#interface ce14/1
(config-if)#load-interval 30
(config-if)#ip address 105.1.1.1/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
(config)#interface ce14/2
(config-if)#load-interval 30
(config-if)#ip address 105.1.2.1/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
(config)#interface lo
(config-if)#ip address 127.0.0.1/8
(config-if)#ip address 15.15.15.15/32 secondary
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
(config)#interface loopback1
(config-if)#ip address 25.25.25.25/32 secondary
(config-if)#commit
(config-if)#exit
11. Configure router OSPF.
(config)#router ospf 100
(config-router)#ospf router-id 15.15.15.15
(config-router)#network 15.15.15.15/32 area 0.0.0.0
(config-router)#network 25.25.25.25/32 area 0.0.0.1
(config-router)#network 90.1.1.0/24 area 0.0.0.0
(config-router)#network 100.1.1.0/24 area 0.0.0.0
(config-router)#network 105.1.1.0/24 area 0.0.0.1
(config-router)#network 105.1.2.0/24 area 0.0.0.1
(config-router)#commit
(config-router)#exit
12. Configure router BGP.
(config)#router bgp 65002
(config-router)#bgp router-id 15.15.15.15
(config-router)#bgp bestpath domain-path-id
(config-router)#bgp domain-path-id ipvpn 2523:23
(config-router)#bgp domain-path-id evpn 2524:24
(config-router)#bgp domain-path-id local 2525:25
(config-router)#neighbor 4.4.4.4 remote-as 65003
(config-router)#neighbor 4.4.4.4 ebgp-multihop
(config-router)#neighbor 4.4.4.4 update-source lo
(config-router)#neighbor 5.5.5.5 remote-as 65003
(config-router)#neighbor 5.5.5.5 ebgp-multihop
(config-router)#neighbor 5.5.5.5 update-source lo
(config-router)#neighbor 23.23.23.23 remote-as 65002
(config-router)#neighbor 23.23.23.23 update-source loopback1
(config-router)#neighbor 24.24.24.24 remote-as 65002
(config-router)#neighbor 24.24.24.24 update-source loopback1
(config-router)#neighbor 26.26.26.26 remote-as 65002
(config-router)#neighbor 26.26.26.26 update-source loopback1
(config-router)#address-family ipv4 unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#exit-address-family
(config-router)#address-family vpnv4 unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths install
(config-router-af)#multi-path
(config-router-af)#neighbor 23.23.23.23 activate
(config-router-af)#neighbor 23.23.23.23 peer-type fabric-external
(config-router-af)#neighbor 23.23.23.23 allowas-in 1
(config-router-af)#neighbor 24.24.24.24 activate
(config-router-af)#neighbor 24.24.24.24 peer-type fabric-external
(config-router-af)#neighbor 24.24.24.24 allowas-in 1
(config-router-af)#neighbor 26.26.26.26 activate
(config-router-af)#neighbor 26.26.26.26 peer-type fabric-external
(config-router-af)#neighbor 26.26.26.26 allowas-in 1
(config-router-af)#exit-address-family
(config-router)#address-family l2vpn evpn
(config-router-af)#neighbor 4.4.4.4 activate
(config-router-af)#neighbor 5.5.5.5 activate
(config-router-af)#neighbor 23.23.23.23 activate
(config-router-af)#neighbor 23.23.23.23 peer-type fabric-external
(config-router-af)#neighbor 23.23.23.23 allowas-in 1
(config-router-af)#neighbor 24.24.24.24 activate
(config-router-af)#neighbor 24.24.24.24 peer-type fabric-external
(config-router-af)#neighbor 24.24.24.24 allowas-in 1
(config-router-af)#neighbor 26.26.26.26 activate
(config-router-af)#neighbor 26.26.26.26 peer-type fabric-external
(config-router-af)#neighbor 26.26.26.26 allowas-in 1
(config-router-af)#exit-address-family
(config-router)#address-family vpnv6 unicast
(config-router-af)#multi-path
(config-router-af)#neighbor 23.23.23.23 activate
(config-router-af)#neighbor 23.23.23.23 peer-type fabric-external
(config-router-af)#neighbor 23.23.23.23 allowas-in 1
(config-router-af)#neighbor 24.24.24.24 activate
(config-router-af)#neighbor 24.24.24.24 peer-type fabric-external
(config-router-af)#neighbor 24.24.24.24 allowas-in 1
(config-router-af)#neighbor 26.26.26.26 activate
(config-router-af)#neighbor 26.26.26.26 peer-type fabric-external
(config-router-af)#neighbor 26.26.26.26 allowas-in 1
(config-router-af)#exit-address-family
(config-router)#address-family ipv4 vrf L3_VRF1
(config-router-af)#max-paths ibgp 4
(config-router-af)#re-originate vpnv4-unicast as l2vpn-evpn
(config-router-af)#re-originate l2vpn-evpn as vpnv4-unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#exit-address-family
(config-router)#address-family ipv6 vrf L3_VRF1
(config-router-af)#max-paths ibgp 4
(config-router-af)#re-originate vpnv6-unicast as l2vpn-evpn
(config-router-af)#re-originate l2vpn-evpn as vpnv6-unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#exit-address-family
(config-router)#commit
(config-router)#exit
BLEAF4
1. Configure GW VTEP IP.
(config)#evpn interconnect-mh gw-vtep-ip vxlan 15.15.15.15 mpls 25.25.25.25
Note: Configure this command before enabling other multihoming parameters (multi-homed iesi / MH enables). It is mandatory for EVPN interconnect multihoming; omitting or removing it causes forwarding loops, traffic duplication, and flood suppression failures. If applied after initial peering, run clear ip bgp * to reclassify peer-GW routes into their respective DC/WAN domains.
2. Enable hardware filter profiles.
(config)#hardware-profile filter evpn-arp-nd enable
(config)#hardware-profile filter vxlan-mh enable
(config)#hardware-profile filter evpn-mpls-mh enable
(config)#hardware-profile filter evpn-stitch enable
3. Enable VXLAN and IRB and EVPN VXLAN multihoming.
(config)#nvo vxlan enable
(config)#nvo vxlan irb
(config)#evpn mpls enable
(config)#evpn vxlan multihoming enable
(config)#evpn irb-forwarding anycast-gateway-mac 0000.0003.abcd
(config)#evpn mpls multihoming enable
4. Configure L3 VRF with EVPN interconnecting and enable EVPN interconnecting.
(config)#ip vrf L3_VRF1
(config-vrf)#rd 16.16.16.16:101
(config-vrf)#route-target both 100:2
(config-vrf)#l3vni 1000
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 16.16.16.16:951
(config-vrf-evpn)#route-target both 951:1
(config-vrf-evpn)#host-route-extend-l2vni 1003-1004
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF1
(config-vrf)#rd 16.16.16.16:1
(config-vrf)#route-target both 1:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 16.16.16.16:901
(config-vrf-evpn)#route-target both 901:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:11:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF10
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 16.16.16.16:10
(config-vrf)#route-target both 10:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 16.16.16.16:910
(config-vrf-evpn)#route-target both 910:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:99:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF2
(config-vrf)#rd 16.16.16.16:2
(config-vrf)#route-target both 2:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 16.16.16.16:902
(config-vrf-evpn)#route-target both 902:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:22:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF3
(config-vrf)#rd 16.16.16.16:3
(config-vrf)#route-target both 3:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 16.16.16.16:903
(config-vrf-evpn)#route-target both 903:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:33:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF4
(config-vrf)#rd 16.16.16.16:4
(config-vrf)#route-target both 4:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 16.16.16.16:904
(config-vrf-evpn)#route-target both 904:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:44:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF5
(config-vrf)#rd 16.16.16.16:5
(config-vrf)#route-target both 5:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 16.16.16.16:905
(config-vrf-evpn)#route-target both 905:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:55:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF6
(config-vrf)#rd 16.16.16.16:6
(config-vrf)#route-target both 6:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 16.16.16.16:906
(config-vrf-evpn)#route-target both 906:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:66:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF7
(config-vrf)#rd 16.16.16.16:7
(config-vrf)#route-target both 7:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 16.16.16.16:907
(config-vrf-evpn)#route-target both 907:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:77:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF8
(config-vrf)#evpn-vlan-service vlan-based
(config-vrf)#rd 16.16.16.16:8
(config-vrf)#route-target both 8:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 16.16.16.16:908
(config-vrf-evpn)#route-target both 908:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:88:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
(config)#mac vrf L2_VRF9
(config-vrf)#rd 16.16.16.16:9
(config-vrf)#route-target both 9:2
(config-vrf)#evpn stitching
(config-vrf-evpn)#rd 16.16.16.16:909
(config-vrf-evpn)#route-target both 909:1
(config-vrf-evpn)#encapsulation mpls
(config-vrf-evpn)#multi-homed iesi 00:22:99:11:11:11:11:11:11 all-active
(config-vrf-evpn)#exit-config-vrf-evpn-mode
5. Configure global VTEP IP.
(config)#nvo vxlan vtep-ip-global 16.16.16.16
6. Configure NVO VXLAN.
(config)#nvo vxlan id 1001 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF1
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1002 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF2
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1003 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF3
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1004 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF4
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1005 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF5
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1006 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF6
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1007 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF7
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1008 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF8
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1009 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF9
(config-nvo)#commit
(config-nvo)#exit
(config)#nvo vxlan id 1010 ingress-replication inner-vid-disabled
(config-nvo)#vxlan host-reachability-protocol evpn-bgp L2_VRF10
(config-nvo)#commit
(config-nvo)#exit
7. Configure global MPLS VTEP source.
(config)#evpn mpls vtep-ip-global 26.26.26.26
8. Configure EVPN MPLS instance stitched to VXLAN VNI under L2_VRF.
(config)#evpn mpls id 100001 interconnect-vnid 1001
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF1
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100002 interconnect-vnid 1002
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF2
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100003 interconnect-vnid 1003
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF3
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100004 interconnect-vnid 1004
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF4
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100005 control-word interconnect-vnid 1005
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF5
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100006 interconnect-vnid 1006
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF6
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100007 flow-label interconnect-vnid 1007
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF7
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100008 control-word flow-label interconnect-vnid 1008
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF8
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100009 interconnect-vnid 1009
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF9
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
(config)#evpn mpls id 100010 interconnect-vnid 1010
(config-evpn-mpls)#host-reachability-protocol evpn-bgp L2_VRF10
(config-evpn-mpls)#commit
(config-evpn-mpls)#exit
9. Configure LDP.
(config)#router ldp
(config)#router-id 16.16.16.16
(config)#transport-address ipv4 16.16.16.16
(config)#targeted-peer ipv4 13.13.13.13
(config-router-targeted-peer)#exit-targeted-peer-mode
(config)#targeted-peer ipv4 14.14.14.14
(config-router-targeted-peer)#exit-targeted-peer-mode
(config)# targeted-peer ipv4 15.15.15.15
(config-router-targeted-peer)#exit-targeted-peer-mode
10. Configure interfaces.
(config)#interface ce2
(config-if)#load-interval 30
(config-if)#ip address 90.1.2.2/24
(config-if)#commit
(config-if)#exit
(config)#interface ce3
(config-if)#load-interval 30
(config-if)#ip address 100.1.2.2/24
(config-if)#commit
(config-if)#exit
(config)#interface lo
(config-if)#ip address 127.0.0.1/8
(config-if)#ip address 16.16.16.16/32 secondary
(config-if)#ipv6 address ::1/128
(config-if)#commit
(config-if)#exit
(config)#interface loopback1
(config-if)#ip address 26.26.26.26/32 secondary
(config-if)#commit
(config-if)#exit
(config)#interface xe10
(config-if)#load-interval 30
(config-if)#ip address 106.1.1.1/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
(config)#interface xe11
(config-if)#load-interval 30
(config-if)#ip address 106.1.2.1/24
(config-if)#label-switching
(config-if)#enable-ldp ipv4
(config-if)#commit
(config-if)#exit
11. Configure router OSPF.
(config)#router ospf 100
(config-router)#ospf router-id 16.16.16.16
(config-router)#network 16.16.16.16/32 area 0.0.0.0
(config-router)#network 26.26.26.26/32 area 0.0.0.1
(config-router)#network 90.1.2.0/24 area 0.0.0.0
(config-router)#network 100.1.2.0/24 area 0.0.0.0
(config-router)#network 106.1.1.0/24 area 0.0.0.1
(config-router)#network 106.1.2.0/24 area 0.0.0.1
(config-router)#commit
(config-router)#exit
12. Configure router BGP.
(config)#router bgp 65002
(config-router)#bgp router-id 16.16.16.16
(config-router)#bgp bestpath domain-path-id
(config-router)#bgp domain-path-id ipvpn 2523:23
(config-router)#bgp domain-path-id evpn 2524:24
(config-router)#bgp domain-path-id local 2526:26
(config-router)#neighbor 4.4.4.4 remote-as 65003
(config-router)#neighbor 4.4.4.4 ebgp-multihop
(config-router)#neighbor 4.4.4.4 update-source lo
(config-router)#neighbor 5.5.5.5 remote-as 65003
(config-router)#neighbor 5.5.5.5 ebgp-multihop
(config-router)#neighbor 5.5.5.5 update-source lo
(config-router)#neighbor 23.23.23.23 remote-as 65002
(config-router)#neighbor 23.23.23.23 update-source loopback1
(config-router)#neighbor 24.24.24.24 remote-as 65002
(config-router)#neighbor 24.24.24.24 update-source loopback1
(config-router)#neighbor 25.25.25.25 remote-as 65002
(config-router)#neighbor 25.25.25.25 update-source loopback1
(config-router)#address-family ipv4 unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#exit-address-family
(config-router)#address-family vpnv4 unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths install
(config-router-af)#multi-path
(config-router-af)#neighbor 23.23.23.23 activate
(config-router-af)#neighbor 23.23.23.23 peer-type fabric-external
(config-router-af)#neighbor 23.23.23.23 allowas-in 1
(config-router-af)#neighbor 24.24.24.24 activate
(config-router-af)#neighbor 24.24.24.24 peer-type fabric-external
(config-router-af)#neighbor 24.24.24.24 allowas-in 1
(config-router-af)#neighbor 25.25.25.25 activate
(config-router-af)#neighbor 25.25.25.25 peer-type fabric-external
(config-router-af)#neighbor 25.25.25.25 allowas-in 1
(config-router-af)#exit-address-family
(config-router)#address-family l2vpn evpn
(config-router-af)#neighbor 4.4.4.4 activate
(config-router-af)#neighbor 5.5.5.5 activate
(config-router-af)#neighbor 23.23.23.23 activate
(config-router-af)#neighbor 23.23.23.23 peer-type fabric-external
(config-router-af)#neighbor 23.23.23.23 allowas-in 1
(config-router-af)#neighbor 24.24.24.24 activate
(config-router-af)#neighbor 24.24.24.24 peer-type fabric-external
(config-router-af)#neighbor 24.24.24.24 allowas-in 1
(config-router-af)#neighbor 25.25.25.25 activate
(config-router-af)#neighbor 25.25.25.25 peer-type fabric-external
(config-router-af)#neighbor 25.25.25.25 allowas-in 1
(config-router-af)#exit-address-family
(config-router)#address-family vpnv6 unicast
(config-router-af)#multi-path
(config-router-af)#neighbor 23.23.23.23 activate
(config-router-af)#neighbor 23.23.23.23 peer-type fabric-external
(config-router-af)#neighbor 23.23.23.23 allowas-in 1
(config-router-af)#neighbor 24.24.24.24 activate
(config-router-af)#neighbor 24.24.24.24 peer-type fabric-external
(config-router-af)#neighbor 24.24.24.24 allowas-in 1
(config-router-af)#neighbor 25.25.25.25 activate
(config-router-af)#neighbor 25.25.25.25 peer-type fabric-external
(config-router-af)#neighbor 25.25.25.25 allowas-in 1
(config-router-af)#exit-address-family
(config-router)#address-family ipv4 vrf L3_VRF1
(config-router-af)#max-paths ibgp 4
(config-router-af)#re-originate vpnv4-unicast as l2vpn-evpn
(config-router-af)#re-originate l2vpn-evpn as vpnv4-unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#exit-address-family
(config-router)#address-family ipv6 vrf L3_VRF1
(config-router-af)#max-paths ibgp 4
(config-router-af)#re-originate vpnv6-unicast as l2vpn-evpn
(config-router-af)#re-originate l2vpn-evpn as vpnv6-unicast
(config-router-af)#bgp additional-paths send-receive
(config-router-af)#bgp additional-paths select all
(config-router-af)#redistribute connected
(config-router-af)#bgp bestpath as-path multipath-relax
(config-router-af)#exit-address-family
(config-router)#commit
(config-router)#exit
Running Configuration
VTEP1
!
nvo vxlan enable
!
nvo vxlan irb
!
evpn esi hold-time 100
!
evpn vxlan multihoming enable
!
evpn irb-forwarding anycast-gateway-mac 0000.0000.abcd
!
ip vrf L3_VRF1
rd 1.1.1.1:101
route-target both 100:1
l3vni 1000
!
mac vrf L2_VRF1
rd 1.1.1.1:1
route-target both 1:1
!
mac vrf L2_VRF10
evpn-vlan-service vlan-based
rd 1.1.1.1:10
route-target both 10:1
!
mac vrf L2_VRF2
rd 1.1.1.1:2
route-target both 2:1
!
mac vrf L2_VRF3
rd 1.1.1.1:3
route-target both 3:1
!
mac vrf L2_VRF4
rd 1.1.1.1:4
route-target both 4:1
!
mac vrf L2_VRF5
rd 1.1.1.1:5
route-target both 5:1
!
mac vrf L2_VRF6
rd 1.1.1.1:6
route-target both 6:1
!
mac vrf L2_VRF7
rd 1.1.1.1:7
route-target both 7:1
!
mac vrf L2_VRF8
evpn-vlan-service vlan-based
rd 1.1.1.1:8
route-target both 8:1
!
mac vrf L2_VRF9
rd 1.1.1.1:9
route-target both 9:1
!
nvo vxlan vtep-ip-global 1.1.1.1
!
nvo vxlan id 1001 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF1
evpn irb1001
!
nvo vxlan id 1002 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF2
!
nvo vxlan id 1003 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF3
!
nvo vxlan id 1004 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF4
!
nvo vxlan id 1005 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF5
!
nvo vxlan id 1006 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF6
!
nvo vxlan id 1007 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF7
!
nvo vxlan id 1008 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF8
!
nvo vxlan id 1009 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF9
!
nvo vxlan id 1010 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF10
!
interface po100
switchport
load-interval 30
evpn multi-homed system-mac 0000.9999.1111
!
interface ce1
load-interval 30
ip address 10.1.2.1/24
!
interface ce2
load-interval 30
ip address 10.1.1.1/24
!
interface ce32
channel-group 100 mode active
!
interface irb1001
ip vrf forwarding L3_VRF1
evpn irb-if-forwarding anycast-gateway-mac
ip address 101.101.1.1/24 anycast
ipv6 address 101::1/64 anycast
!
interface lo
ip address 127.0.0.1/8
ip address 1.1.1.1/32 secondary
ipv6 address ::1/128
!
exit
!
router ospf 100
ospf router-id 1.1.1.1
network 1.1.1.1/32 area 0.0.0.0
network 10.1.1.0/24 area 0.0.0.0
network 10.1.2.0/24 area 0.0.0.0
!
router bgp 65001
bgp router-id 1.1.1.1
neighbor 2.2.2.2 remote-as 65001
neighbor 2.2.2.2 update-source lo
neighbor 13.13.13.13 remote-as 65002
neighbor 13.13.13.13 ebgp-multihop
neighbor 13.13.13.13 update-source lo
neighbor 14.14.14.14 remote-as 65002
neighbor 14.14.14.14 ebgp-multihop
neighbor 14.14.14.14 update-source lo
!
address-family l2vpn evpn
neighbor 2.2.2.2 activate
neighbor 13.13.13.13 activate
neighbor 14.14.14.14 activate
exit-address-family
!
address-family ipv4 vrf L3_VRF1
max-paths ebgp 4
max-paths ibgp 4
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
address-family ipv6 vrf L3_VRF1
max-paths ebgp 4
max-paths ibgp 4
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
exit
!
nvo vxlan max-cache-disable 5
!
nvo vxlan access-if port-vlan po100 1001
map vnid 1001
!
nvo vxlan access-if port-vlan po100 1002
map vnid 1002
!
nvo vxlan access-if port-vlan po100 1003
map vnid 1003
!
nvo vxlan access-if port-vlan po100 1004
map vnid 1004
!
nvo vxlan access-if port-vlan po100 1005
map vnid 1005
!
nvo vxlan access-if port-vlan po100 1006
map vnid 1006
!
nvo vxlan access-if port-vlan po100 1007
map vnid 1007
!
nvo vxlan access-if port-vlan po100 1008
map vnid 1008
!
nvo vxlan access-if port-vlan po100 1009
map vnid 1009
!
nvo vxlan access-if port-vlan po100 1010
map vnid 1010
!
VTEP2
!
nvo vxlan enable
!
nvo vxlan irb
!
evpn esi hold-time 100
!
evpn vxlan multihoming enable
!
evpn irb-forwarding anycast-gateway-mac 0000.0000.abcd
!
ip vrf L3_VRF1
rd 2.2.2.2:101
route-target both 100:1
l3vni 1000
!
mac vrf L2_VRF1
rd 2.2.2.2:1
route-target both 1:1
!
mac vrf L2_VRF10
evpn-vlan-service vlan-based
rd 2.2.2.2:10
route-target both 10:1
!
mac vrf L2_VRF2
rd 2.2.2.2:2
route-target both 2:1
!
mac vrf L2_VRF3
rd 2.2.2.2:3
route-target both 3:1
!
mac vrf L2_VRF4
rd 2.2.2.2:4
route-target both 4:1
!
mac vrf L2_VRF5
rd 2.2.2.2:5
route-target both 5:1
!
mac vrf L2_VRF6
rd 2.2.2.2:6
route-target both 6:1
!
mac vrf L2_VRF7
rd 2.2.2.2:7
route-target both 7:1
!
mac vrf L2_VRF8
evpn-vlan-service vlan-based
rd 2.2.2.2:8
route-target both 8:1
!
mac vrf L2_VRF9
rd 2.2.2.2:9
route-target both 9:1
!
nvo vxlan vtep-ip-global 2.2.2.2
!
nvo vxlan id 1001 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF1
evpn irb1001
!
nvo vxlan id 1002 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF2
evpn irb1002
!
nvo vxlan id 1003 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF3
!
nvo vxlan id 1004 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF4
!
nvo vxlan id 1005 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF5
!
nvo vxlan id 1006 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF6
!
nvo vxlan id 1007 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF7
!
nvo vxlan id 1008 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF8
!
nvo vxlan id 1009 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF9
!
nvo vxlan id 1010 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF10
!
interface po100
switchport
load-interval 30
evpn multi-homed system-mac 0000.9999.1111
!
interface ce2
load-interval 30
ip address 20.1.2.1/24
!
interface ce29
switchport
load-interval 30
!
interface ce32
channel-group 100 mode active
!
interface irb1001
ip vrf forwarding L3_VRF1
evpn irb-if-forwarding anycast-gateway-mac
ip address 101.101.1.1/24 anycast
ipv6 address 101::1/64 anycast
!
interface irb1002
ip vrf forwarding L3_VRF1
ip address 201.101.1.1/24
ipv6 address 201::1/64
!
interface lo
ip address 127.0.0.1/8
ip address 2.2.2.2/32 secondary
ipv6 address ::1/128
!
interface xe33
load-interval 30
ip address 20.1.1.1/24
!
exit
!
router ospf 100
ospf router-id 2.2.2.2
network 2.2.2.2/32 area 0.0.0.0
network 20.1.1.0/24 area 0.0.0.0
network 20.1.2.0/24 area 0.0.0.0
!
router bgp 65001
bgp router-id 2.2.2.2
neighbor 1.1.1.1 remote-as 65001
neighbor 1.1.1.1 update-source lo
neighbor 13.13.13.13 remote-as 65002
neighbor 13.13.13.13 ebgp-multihop
neighbor 13.13.13.13 update-source lo
neighbor 14.14.14.14 remote-as 65002
neighbor 14.14.14.14 ebgp-multihop
neighbor 14.14.14.14 update-source lo
!
address-family l2vpn evpn
neighbor 1.1.1.1 activate
neighbor 13.13.13.13 activate
neighbor 14.14.14.14 activate
exit-address-family
!
address-family ipv4 vrf L3_VRF1
max-paths ebgp 4
max-paths ibgp 4
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
address-family ipv6 vrf L3_VRF1
max-paths ebgp 4
max-paths ibgp 4
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
exit
!
nvo vxlan max-cache-disable 5
!
nvo vxlan access-if port-vlan ce29 1001
map vnid 1001
!
nvo vxlan access-if port-vlan ce29 1002
map vnid 1002
!
nvo vxlan access-if port-vlan ce29 1003
map vnid 1003
!
nvo vxlan access-if port-vlan ce29 1004
map vnid 1004
!
nvo vxlan access-if port-vlan ce29 1005
map vnid 1005
!
nvo vxlan access-if port-vlan ce29 1006
map vnid 1006
!
nvo vxlan access-if port-vlan ce29 1007
map vnid 1007
!
nvo vxlan access-if port-vlan ce29 1008
map vnid 1008
!
nvo vxlan access-if port-vlan ce29 1009
map vnid 1009
!
nvo vxlan access-if port-vlan ce29 1010
map vnid 1010
!
nvo vxlan access-if port-vlan po100 1001
map vnid 1001
!
nvo vxlan access-if port-vlan po100 1002
map vnid 1002
!
nvo vxlan access-if port-vlan po100 1003
map vnid 1003
!
nvo vxlan access-if port-vlan po100 1004
map vnid 1004
!
nvo vxlan access-if port-vlan po100 1005
map vnid 1005
!
nvo vxlan access-if port-vlan po100 1006
map vnid 1006
!
nvo vxlan access-if port-vlan po100 1007
map vnid 1007
!
nvo vxlan access-if port-vlan po100 1008
map vnid 1008
!
nvo vxlan access-if port-vlan po100 1009
map vnid 1009
!
nvo vxlan access-if port-vlan po100 1010
map vnid 1010
!
VTEP4
!
nvo vxlan enable
!
nvo vxlan irb
!
evpn esi hold-time 100
!
evpn vxlan multihoming enable
!
evpn irb-forwarding anycast-gateway-mac 0000.0001.abcd
!
ip vrf L3_VRF1
rd 4.4.4.4:101
route-target both 100:2
l3vni 1000
!
mac vrf L2_VRF1
rd 4.4.4.4:1
route-target both 1:2
!
mac vrf L2_VRF10
evpn-vlan-service vlan-based
rd 4.4.4.4:10
route-target both 10:2
!
mac vrf L2_VRF2
rd 4.4.4.4:2
route-target both 2:2
!
mac vrf L2_VRF3
rd 4.4.4.4:3
route-target both 3:2
!
mac vrf L2_VRF4
rd 4.4.4.4:4
route-target both 4:2
!
mac vrf L2_VRF5
rd 4.4.4.4:5
route-target both 5:2
!
mac vrf L2_VRF6
rd 4.4.4.4:6
route-target both 6:2
!
mac vrf L2_VRF7
rd 4.4.4.4:7
route-target both 7:2
!
mac vrf L2_VRF8
evpn-vlan-service vlan-based
rd 4.4.4.4:8
route-target both 8:2
!
mac vrf L2_VRF9
rd 4.4.4.4:9
route-target both 9:2
!
nvo vxlan vtep-ip-global 4.4.4.4
!
nvo vxlan id 1001 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF1
!
nvo vxlan id 1002 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF2
!
nvo vxlan id 1003 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF3
evpn irb1003
!
nvo vxlan id 1004 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF4
!
nvo vxlan id 1005 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF5
!
nvo vxlan id 1006 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF6
!
nvo vxlan id 1007 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF7
!
nvo vxlan id 1008 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF8
!
nvo vxlan id 1009 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF9
!
nvo vxlan id 1010 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF10
!
interface po200
switchport
load-interval 30
evpn multi-homed system-mac 0000.9999.2222
!
interface ce50/1
load-interval 30
ip address 40.1.1.1/24
!
interface ce54/1
load-interval 30
ip address 40.1.2.1/24
!
interface irb1003
ip vrf forwarding L3_VRF1
evpn irb-if-forwarding anycast-gateway-mac
ip address 102.101.1.1/24 anycast
ipv6 address 102::1/64 anycast
!
interface lo
ip address 127.0.0.1/8
ip address 4.4.4.4/32 secondary
ipv6 address ::1/128
!
interface xe48
channel-group 200 mode active
!
exit
!
router ospf 100
ospf router-id 4.4.4.4
network 4.4.4.4/32 area 0.0.0.0
network 40.1.1.0/24 area 0.0.0.0
network 40.1.2.0/24 area 0.0.0.0
!
router bgp 65003
bgp router-id 4.4.4.4
neighbor 5.5.5.5 remote-as 65003
neighbor 5.5.5.5 update-source lo
neighbor 15.15.15.15 remote-as 65002
neighbor 15.15.15.15 ebgp-multihop
neighbor 15.15.15.15 update-source lo
neighbor 16.16.16.16 remote-as 65002
neighbor 16.16.16.16 ebgp-multihop
neighbor 16.16.16.16 update-source lo
!
address-family l2vpn evpn
neighbor 5.5.5.5 activate
neighbor 15.15.15.15 activate
neighbor 16.16.16.16 activate
exit-address-family
!
address-family ipv4 vrf L3_VRF1
max-paths ebgp 4
max-paths ibgp 4
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
address-family ipv6 vrf L3_VRF1
max-paths ebgp 4
max-paths ibgp 4
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
exit
!
nvo vxlan max-cache-disable 5
!
nvo vxlan access-if port-vlan po200 1001
map vnid 1001
!
nvo vxlan access-if port-vlan po200 1002
map vnid 1002
!
nvo vxlan access-if port-vlan po200 1003
map vnid 1003
!
nvo vxlan access-if port-vlan po200 1004
map vnid 1004
!
nvo vxlan access-if port-vlan po200 1005
map vnid 1005
!
nvo vxlan access-if port-vlan po200 1006
map vnid 1006
!
nvo vxlan access-if port-vlan po200 1007
map vnid 1007
!
nvo vxlan access-if port-vlan po200 1008
map vnid 1008
!
nvo vxlan access-if port-vlan po200 1009
map vnid 1009
!
nvo vxlan access-if port-vlan po200 1010
map vnid 1010
!
VTEP5
!
nvo vxlan enable
!
nvo vxlan irb
!
evpn esi hold-time 100
!
evpn vxlan multihoming enable
!
evpn irb-forwarding anycast-gateway-mac 0000.0001.abcd
!
ip vrf L3_VRF1
rd 5.5.5.5:101
route-target both 100:2
l3vni 1000
!
mac vrf L2_VRF1
rd 5.5.5.5:1
route-target both 1:2
!
mac vrf L2_VRF10
evpn-vlan-service vlan-based
rd 5.5.5.5:10
route-target both 10:2
!
mac vrf L2_VRF2
rd 5.5.5.5:2
route-target both 2:2
!
mac vrf L2_VRF3
rd 5.5.5.5:3
route-target both 3:2
!
mac vrf L2_VRF4
rd 5.5.5.5:4
route-target both 4:2
!
mac vrf L2_VRF5
rd 5.5.5.5:5
route-target both 5:2
!
mac vrf L2_VRF6
rd 5.5.5.5:6
route-target both 6:2
!
mac vrf L2_VRF7
rd 5.5.5.5:7
route-target both 7:2
!
mac vrf L2_VRF8
evpn-vlan-service vlan-based
rd 5.5.5.5:8
route-target both 8:2
!
mac vrf L2_VRF9
rd 5.5.5.5:9
route-target both 9:2
!
nvo vxlan vtep-ip-global 5.5.5.5
!
nvo vxlan id 1001 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF1
!
nvo vxlan id 1002 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF2
!
nvo vxlan id 1003 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF3
evpn irb1003
!
nvo vxlan id 1004 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF4
evpn irb1004
!
nvo vxlan id 1005 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF5
!
nvo vxlan id 1006 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF6
!
nvo vxlan id 1007 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF7
!
nvo vxlan id 1008 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF8
!
nvo vxlan id 1009 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF9
!
nvo vxlan id 1010 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF10
!
interface po200
switchport
load-interval 30
evpn multi-homed system-mac 0000.9999.2222
!
interface cd3/1
switchport
load-interval 30
!
interface cd21/1
channel-group 200 mode active
!
interface irb1003
ip vrf forwarding L3_VRF1
evpn irb-if-forwarding anycast-gateway-mac
ip address 102.101.1.1/24 anycast
ipv6 address 102::1/64 anycast
!
interface irb1004
ip vrf forwarding L3_VRF1
ip address 202.101.1.1/24
ipv6 address 202::1/64
!
interface lo
ip address 127.0.0.1/8
ip address 5.5.5.5/32 secondary
ipv6 address ::1/128
!
interface xe33
ip address 50.1.1.1/24
!
interface xe34
load-interval 30
ip address 50.1.2.1/24
!
exit
!
router ospf 100
ospf router-id 5.5.5.5
network 5.5.5.5/32 area 0.0.0.0
network 50.1.1.0/24 area 0.0.0.0
network 50.1.2.0/24 area 0.0.0.0
!
router bgp 65003
bgp router-id 5.5.5.5
neighbor 4.4.4.4 remote-as 65003
neighbor 4.4.4.4 update-source lo
neighbor 15.15.15.15 remote-as 65002
neighbor 15.15.15.15 ebgp-multihop
neighbor 15.15.15.15 update-source lo
neighbor 16.16.16.16 remote-as 65002
neighbor 16.16.16.16 ebgp-multihop
neighbor 16.16.16.16 update-source lo
!
address-family l2vpn evpn
neighbor 4.4.4.4 activate
neighbor 15.15.15.15 activate
neighbor 16.16.16.16 activate
exit-address-family
!
address-family ipv4 vrf L3_VRF1
max-paths ebgp 4
max-paths ibgp 4
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
address-family ipv6 vrf L3_VRF1
max-paths ebgp 4
max-paths ibgp 4
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
exit
!
nvo vxlan max-cache-disable 5
!
nvo vxlan access-if port-vlan cd3/1 1001
map vnid 1001
!
nvo vxlan access-if port-vlan cd3/1 1002
map vnid 1002
!
nvo vxlan access-if port-vlan cd3/1 1003
map vnid 1003
!
nvo vxlan access-if port-vlan cd3/1 1004
map vnid 1004
!
nvo vxlan access-if port-vlan cd3/1 1005
map vnid 1005
!
nvo vxlan access-if port-vlan cd3/1 1006
map vnid 1006
!
nvo vxlan access-if port-vlan cd3/1 1007
map vnid 1007
!
nvo vxlan access-if port-vlan cd3/1 1008
map vnid 1008
!
nvo vxlan access-if port-vlan cd3/1 1009
map vnid 1009
!
nvo vxlan access-if port-vlan cd3/1 1010
map vnid 1010
!
nvo vxlan access-if port-vlan po200 1001
map vnid 1001
!
nvo vxlan access-if port-vlan po200 1002
map vnid 1002
!
nvo vxlan access-if port-vlan po200 1003
map vnid 1003
!
nvo vxlan access-if port-vlan po200 1004
map vnid 1004
!
nvo vxlan access-if port-vlan po200 1005
map vnid 1005
!
nvo vxlan access-if port-vlan po200 1006
map vnid 1006
!
nvo vxlan access-if port-vlan po200 1007
map vnid 1007
!
nvo vxlan access-if port-vlan po200 1008
map vnid 1008
!
nvo vxlan access-if port-vlan po200 1009
map vnid 1009
!
nvo vxlan access-if port-vlan po200 1010
map vnid 1010
!
R1
!
router ldp
router-id 17.17.17.17
transport-address ipv4 17.17.17.17
!
interface lo
ip address 127.0.0.1/8
ip address 17.17.17.17/32 secondary
ipv6 address ::1/128
!
interface xe2
load-interval 30
ip address 103.1.1.2/24
label-switching
enable-ldp ipv4
!
interface xe14
load-interval 30
ip address 106.1.1.2/24
label-switching
enable-ldp ipv4
!
interface xe16
load-interval 30
ip address 104.1.1.2/24
label-switching
enable-ldp ipv4
!
interface xe19
load-interval 30
ip address 105.1.1.2/24
label-switching
enable-ldp ipv4
!
exit
!
router ospf 100
ospf router-id 17.17.17.17
network 17.17.17.17/32 area 0.0.0.1
network 103.1.1.0/24 area 0.0.0.1
network 104.1.1.0/24 area 0.0.0.1
network 105.1.1.0/24 area 0.0.0.1
network 106.1.1.0/24 area 0.0.0.1
===================================================
R2
===================================================
router ldp
router-id 18.18.18.18
transport-address ipv4 18.18.18.18
!
interface ce0
load-interval 30
ip address 103.1.2.2/24
label-switching
enable-ldp ipv4
!
interface lo
ip address 127.0.0.1/8
ip address 18.18.18.18/32 secondary
ipv6 address ::1/128
!
interface lo.management
ip vrf forwarding management
ip address 127.0.0.1/8
ipv6 address ::1/128
!
interface xe14
load-interval 30
ip address 106.1.2.2/24
label-switching
enable-ldp ipv4
!
interface xe16
load-interval 30
ip address 104.1.2.2/24
label-switching
enable-ldp ipv4
!
interface xe22
load-interval 30
ip address 105.1.2.2/24
label-switching
enable-ldp ipv4
!
exit
!
router ospf 100
ospf router-id 18.18.18.18
network 18.18.18.18/32 area 0.0.0.1
network 103.1.2.0/24 area 0.0.0.1
network 104.1.2.0/24 area 0.0.0.1
network 105.1.2.0/24 area 0.0.0.1
network 106.1.2.0/24 area 0.0.0.1
!
SWITCH1
!
bridge 1 protocol ieee vlan-bridge
!
vlan database
vlan 1001-1010 bridge 1 state enable
!
interface po100
switchport
bridge-group 1 spanning-tree disable
switchport mode trunk
switchport trunk allowed vlan add 1001-1010
load-interval 30
!
interface ce55
channel-group 100 mode active
!
interface ce56
channel-group 100 mode active
!
interface xe57
switchport
bridge-group 1 spanning-tree disable
switchport mode trunk
switchport trunk allowed vlan add 1001-1010
load-interval 30
!
SWITCH2
!
bridge 1 protocol ieee vlan-bridge
!
vlan database
vlan 1001-1010 bridge 1 state enable
!
interface po200
switchport
bridge-group 1 spanning-tree disable
switchport mode trunk
switchport trunk allowed vlan add 1001-1010
load-interval 30
!
interface xe19
channel-group 200 mode active
!
interface xe51/1
channel-group 200 mode active
!
interface xe57
switchport
bridge-group 1 spanning-tree disable
switchport mode trunk
switchport trunk allowed vlan add 1001-1010
load-interval 30
!
SPINE1
!
interface ce1/2
load-interval 30
ip address 20.1.1.2/24
!
interface ce2/1
ip address 10.1.1.2/24
!
interface ce3/1
load-interval 30
ip address 101.1.1.1/24
!
interface ce21/1
load-interval 30
ip address 101.1.2.1/24
!
interface lo
ip address 127.0.0.1/8
ip address 11.11.11.11/32 secondary
ipv6 address ::1/128
!
exit
!
router ospf 100
ospf router-id 11.11.11.11
network 10.1.1.0/24 area 0.0.0.0
network 11.11.11.11/32 area 0.0.0.0
network 20.1.1.0/24 area 0.0.0.0
network 101.1.1.0/24 area 0.0.0.0
network 101.1.2.0/24 area 0.0.0.0
===================================================
SPINE2
===================================================
interface ce1/1
load-interval 30
ip address 10.1.2.2/24
!
interface ce2/1
load-interval 30
ip address 20.1.2.2/24
!
interface ce3/1
load-interval 30
ip address 102.1.1.1/24
!
interface ce4/1
load-interval 30
ip address 102.1.2.1/24
!
interface lo
ip address 127.0.0.1/8
ip address 12.12.12.12/32 secondary
ipv6 address ::1/128
!
exit
!
router ospf 100
ospf router-id 12.12.12.12
network 10.1.2.0/24 area 0.0.0.0
network 12.12.12.12/32 area 0.0.0.0
network 20.1.2.0/24 area 0.0.0.0
network 102.1.1.0/24 area 0.0.0.0
network 102.1.2.0/24 area 0.0.0.0
!
SPINE4
!
interface ce25
ip address 90.1.2.1/24
!
interface ce27
ip address 90.1.1.1/24
!
interface lo
ip address 127.0.0.1/8
ip address 9.9.9.9/32 secondary
ipv6 address ::1/128
!
interface xe1/1
ip address 50.1.1.2/24
!
interface xe31/1
ip address 40.1.1.2/24
!
exit
!
router ospf 100
ospf router-id 9.9.9.9
network 9.9.9.9/32 area 0.0.0.0
network 40.1.1.0/24 area 0.0.0.0
network 50.1.1.0/24 area 0.0.0.0
network 90.1.1.0/24 area 0.0.0.0
network 90.1.2.0/24 area 0.0.0.0
!
SPINE5
!
interface ce25
load-interval 30
ip address 100.1.2.1/24
!
interface ce27
load-interval 30
ip address 100.1.1.1/24
!
interface lo
ip address 127.0.0.1/8
ip address 10.10.10.10/32 secondary
ipv6 address ::1/128
!
interface xe1/1
load-interval 30
ip address 50.1.2.2/24
!
interface xe31/1
load-interval 30
ip address 40.1.2.2/24
!
exit
!
router ospf 100
ospf router-id 10.10.10.10
network 10.10.10.10/32 area 0.0.0.0
network 40.1.2.0/24 area 0.0.0.0
network 50.1.2.0/24 area 0.0.0.0
network 100.1.1.0/24 area 0.0.0.0
network 100.1.2.0/24 area 0.0.0.0
!
BLEAF1
!
evpn interconnect-mh gw-vtep-ip vxlan 14.14.14.14 mpls 24.24.24.24
!
hardware-profile filter evpn-arp-nd enable
hardware-profile filter vxlan-mh enable
hardware-profile filter evpn-mpls-mh enable
hardware-profile filter evpn-stitch enable
!
nvo vxlan enable
!
nvo vxlan irb
!
evpn mpls enable
!
evpn vxlan multihoming enable
!
evpn irb-forwarding anycast-gateway-mac 0000.0002.abcd
!
evpn mpls multihoming enable
!
ip vrf L3_VRF1
rd 13.13.13.13:101
route-target both 100:1
l3vni 1000
evpn stitching
rd 13.13.13.13:951
route-target both 951:1
host-route-extend-l2vni 1001-1002
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF1
rd 13.13.13.13:1
route-target both 1:1
evpn stitching
rd 13.13.13.13:901
route-target both 901:1
encapsulation mpls
multi-homed iesi 00:11:11:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF10
evpn-vlan-service vlan-based
rd 13.13.13.13:10
route-target both 10:1
evpn stitching
rd 13.13.13.13:910
route-target both 910:1
encapsulation mpls
multi-homed iesi 00:11:99:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF2
rd 13.13.13.13:2
route-target both 2:1
evpn stitching
rd 13.13.13.13:902
route-target both 902:1
encapsulation mpls
multi-homed iesi 00:11:22:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF3
rd 13.13.13.13:3
route-target both 3:1
evpn stitching
rd 13.13.13.13:903
route-target both 903:1
encapsulation mpls
multi-homed iesi 00:11:33:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF4
rd 13.13.13.13:4
route-target both 4:1
evpn stitching
rd 13.13.13.13:904
route-target both 904:1
encapsulation mpls
multi-homed iesi 00:11:44:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF5
rd 13.13.13.13:5
route-target both 5:1
evpn stitching
rd 13.13.13.13:905
route-target both 905:1
encapsulation mpls
multi-homed iesi 00:11:55:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF6
rd 13.13.13.13:6
route-target both 6:1
evpn stitching
rd 13.13.13.13:906
route-target both 906:1
encapsulation mpls
multi-homed iesi 00:11:66:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF7
rd 13.13.13.13:7
route-target both 7:1
evpn stitching
rd 13.13.13.13:907
route-target both 907:1
encapsulation mpls
multi-homed iesi 00:11:77:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF8
evpn-vlan-service vlan-based
rd 13.13.13.13:8
route-target both 8:1
evpn stitching
rd 13.13.13.13:908
route-target both 908:1
encapsulation mpls
multi-homed iesi 00:11:88:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF9
rd 13.13.13.13:9
route-target both 9:1
evpn stitching
rd 13.13.13.13:909
route-target both 909:1
encapsulation mpls
multi-homed iesi 00:11:99:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
nvo vxlan vtep-ip-global 13.13.13.13
!
nvo vxlan id 1001 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF1
!
nvo vxlan id 1002 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF2
!
nvo vxlan id 1003 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF3
!
nvo vxlan id 1004 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF4
!
nvo vxlan id 1005 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF5
!
nvo vxlan id 1006 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF6
!
nvo vxlan id 1007 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF7
!
nvo vxlan id 1008 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF8
!
nvo vxlan id 1009 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF9
!
nvo vxlan id 1010 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF10
!
evpn mpls vtep-ip-global 23.23.23.23
!
evpn mpls id 100001 interconnect-vnid 1001
host-reachability-protocol evpn-bgp L2_VRF1
!
evpn mpls id 100002 interconnect-vnid 1002
host-reachability-protocol evpn-bgp L2_VRF2
!
evpn mpls id 100003 interconnect-vnid 1003
host-reachability-protocol evpn-bgp L2_VRF3
!
evpn mpls id 100004 interconnect-vnid 1004
host-reachability-protocol evpn-bgp L2_VRF4
!
evpn mpls id 100005 control-word interconnect-vnid 1005
host-reachability-protocol evpn-bgp L2_VRF5
!
evpn mpls id 100006 interconnect-vnid 1006
host-reachability-protocol evpn-bgp L2_VRF6
!
evpn mpls id 100007 flow-label interconnect-vnid 1007
host-reachability-protocol evpn-bgp L2_VRF7
!
evpn mpls id 100008 control-word flow-label interconnect-vnid 1008
host-reachability-protocol evpn-bgp L2_VRF8
!
evpn mpls id 100009 interconnect-vnid 1009
host-reachability-protocol evpn-bgp L2_VRF9
!
evpn mpls id 100010 interconnect-vnid 1010
host-reachability-protocol evpn-bgp L2_VRF10
!
router ldp
router-id 13.13.13.13
transport-address ipv4 13.13.13.13
targeted-peer ipv4 14.14.14.14
exit-targeted-peer-mode
targeted-peer ipv4 15.15.15.15
exit-targeted-peer-mode
targeted-peer ipv4 16.16.16.16
exit-targeted-peer-mode
!
interface ce4/4
load-interval 30
!
interface ce4/4.1001 switchport
encapsulation dot1q 1001
rewrite pop
load-interval 30
access-if-evpn
map vpn-id 1001
!
interface ce4/4.1002 switchport
encapsulation dot1q 1002
rewrite pop
load-interval 30
access-if-evpn
map vpn-id 1002
!
interface ce4/4.1003 switchport
encapsulation dot1q 1003
rewrite pop
load-interval 30
access-if-evpn
map vpn-id 1003
!
interface ce4/4.1004 switchport
encapsulation dot1q 1004
rewrite pop
load-interval 30
access-if-evpn
map vpn-id 1004
!
interface ce4/4.1005 switchport
encapsulation dot1q 1005
rewrite pop
load-interval 30
access-if-evpn
map vpn-id 1005
!
interface ce4/4.1006 switchport
encapsulation dot1q 1006
rewrite pop
load-interval 30
access-if-evpn
map vpn-id 1006
!
interface ce4/4.1007 switchport
encapsulation dot1q 1007
rewrite pop
load-interval 30
access-if-evpn
map vpn-id 1007
!
interface ce4/4.1008 switchport
encapsulation dot1q 1008
rewrite pop
load-interval 30
access-if-evpn
map vpn-id 1008
!
interface ce4/4.1009 switchport
encapsulation dot1q 1009
rewrite pop
load-interval 30
access-if-evpn
map vpn-id 1009
!
interface ce4/4.1010 switchport
encapsulation dot1q 1010
rewrite pop
load-interval 30
access-if-evpn
map vpn-id 1010
!
interface ce12
load-interval 30
ip address 103.1.2.1/24
label-switching
enable-ldp ipv4
!
interface ce21
load-interval 30
ip address 102.1.1.2/24
!
interface ce22
load-interval 30
ip address 101.1.1.2/24
!
interface lo
ip address 127.0.0.1/8
ip address 13.13.13.13/32 secondary
ipv6 address ::1/128
!
interface loopback1
ip address 23.23.23.23/32 secondary
!
interface xe2
load-interval 30
ip address 103.1.1.1/24
label-switching
enable-ldp ipv4
!
exit
!
router ospf 100
ospf router-id 13.13.13.13
network 13.13.13.13/32 area 0.0.0.0
network 23.23.23.23/32 area 0.0.0.1
network 101.1.1.0/24 area 0.0.0.0
network 102.1.1.0/24 area 0.0.0.0
network 103.1.1.0/24 area 0.0.0.1
network 103.1.2.0/24 area 0.0.0.1
!
router bgp 65002
bgp router-id 13.13.13.13
bgp bestpath domain-path-id
bgp domain-path-id ipvpn 2323:23
bgp domain-path-id evpn 2324:24
bgp domain-path-id local 2325:25
neighbor 1.1.1.1 remote-as 65001
neighbor 1.1.1.1 ebgp-multihop
neighbor 1.1.1.1 update-source lo
neighbor 2.2.2.2 remote-as 65001
neighbor 2.2.2.2 ebgp-multihop
neighbor 2.2.2.2 update-source lo
neighbor 24.24.24.24 remote-as 65002
neighbor 24.24.24.24 update-source loopback1
neighbor 25.25.25.25 remote-as 65002
neighbor 25.25.25.25 update-source loopback1
neighbor 26.26.26.26 remote-as 65002
neighbor 26.26.26.26 update-source loopback1
!
address-family ipv4 unicast
bgp additional-paths send-receive
exit-address-family
!
address-family vpnv4 unicast
bgp additional-paths send-receive
bgp additional-paths install
multi-path
neighbor 24.24.24.24 activate
neighbor 24.24.24.24 peer-type fabric-external
neighbor 24.24.24.24 allowas-in 1
neighbor 25.25.25.25 activate
neighbor 25.25.25.25 peer-type fabric-external
neighbor 25.25.25.25 allowas-in 1
neighbor 26.26.26.26 activate
neighbor 26.26.26.26 peer-type fabric-external
neighbor 26.26.26.26 allowas-in 1
exit-address-family
!
address-family l2vpn evpn
neighbor 1.1.1.1 activate
neighbor 2.2.2.2 activate
neighbor 24.24.24.24 activate
neighbor 24.24.24.24 peer-type fabric-external
neighbor 24.24.24.24 allowas-in 1
neighbor 25.25.25.25 activate
neighbor 25.25.25.25 peer-type fabric-external
neighbor 25.25.25.25 allowas-in 1
neighbor 26.26.26.26 activate
neighbor 26.26.26.26 peer-type fabric-external
neighbor 26.26.26.26 allowas-in 1
exit-address-family
!
address-family vpnv6 unicast
multi-path
neighbor 24.24.24.24 activate
neighbor 24.24.24.24 peer-type fabric-external
neighbor 24.24.24.24 allowas-in 1
neighbor 25.25.25.25 activate
neighbor 25.25.25.25 peer-type fabric-external
neighbor 25.25.25.25 allowas-in 1
neighbor 26.26.26.26 activate
neighbor 26.26.26.26 peer-type fabric-external
neighbor 26.26.26.26 allowas-in 1
exit-address-family
!
address-family ipv4 vrf L3_VRF1
max-paths ibgp 4
re-originate vpnv4-unicast as l2vpn-evpn
re-originate l2vpn-evpn as vpnv4-unicast
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
address-family ipv6 vrf L3_VRF1
max-paths ibgp 4
re-originate vpnv6-unicast as l2vpn-evpn
re-originate l2vpn-evpn as vpnv6-unicast
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
exit
!
BLEAF2
!
evpn interconnect-mh gw-vtep-ip vxlan 13.13.13.13 mpls 23.23.23.23
!
hardware-profile filter evpn-arp-nd enable
hardware-profile filter vxlan-mh enable
hardware-profile filter evpn-mpls-mh enable
hardware-profile filter evpn-stitch enable
!
nvo vxlan enable
!
nvo vxlan irb
!
evpn mpls enable
!
evpn vxlan multihoming enable
!
evpn irb-forwarding anycast-gateway-mac 0000.0002.abcd
!
evpn mpls multihoming enable
!
ip vrf L3_VRF1
rd 14.14.14.14:101
route-target both 100:1
l3vni 1000
evpn stitching
rd 14.14.14.14:951
route-target both 951:1
host-route-extend-l2vni 1001-1002
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF1
rd 14.14.14.14:1
route-target both 1:1
evpn stitching
rd 14.14.14.14:901
route-target both 901:1
encapsulation mpls
multi-homed iesi 00:11:11:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF10
evpn-vlan-service vlan-based
rd 14.14.14.14:10
route-target both 10:1
evpn stitching
rd 14.14.14.14:910
route-target both 910:1
encapsulation mpls
multi-homed iesi 00:11:99:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF2
rd 14.14.14.14:2
route-target both 2:1
evpn stitching
rd 14.14.14.14:902
route-target both 902:1
encapsulation mpls
multi-homed iesi 00:11:22:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF3
rd 14.14.14.14:3
route-target both 3:1
evpn stitching
rd 14.14.14.14:903
route-target both 903:1
encapsulation mpls
multi-homed iesi 00:11:33:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF4
rd 14.14.14.14:4
route-target both 4:1
evpn stitching
rd 14.14.14.14:904
route-target both 904:1
encapsulation mpls
multi-homed iesi 00:11:44:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF5
rd 14.14.14.14:5
route-target both 5:1
evpn stitching
rd 14.14.14.14:905
route-target both 905:1
encapsulation mpls
multi-homed iesi 00:11:55:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF6
rd 14.14.14.14:6
route-target both 6:1
evpn stitching
rd 14.14.14.14:906
route-target both 906:1
encapsulation mpls
multi-homed iesi 00:11:66:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF7
rd 14.14.14.14:7
route-target both 7:1
evpn stitching
rd 14.14.14.14:907
route-target both 907:1
encapsulation mpls
multi-homed iesi 00:11:77:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF8
evpn-vlan-service vlan-based
rd 14.14.14.14:8
route-target both 8:1
evpn stitching
rd 14.14.14.14:908
route-target both 908:1
encapsulation mpls
multi-homed iesi 00:11:88:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF9
rd 14.14.14.14:9
route-target both 9:1
evpn stitching
rd 14.14.14.14:909
route-target both 909:1
encapsulation mpls
multi-homed iesi 00:11:99:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
nvo vxlan vtep-ip-global 14.14.14.14
!
nvo vxlan id 1001 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF1
!
nvo vxlan id 1002 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF2
!
nvo vxlan id 1003 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF3
!
nvo vxlan id 1004 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF4
!
nvo vxlan id 1005 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF5
!
nvo vxlan id 1006 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF6
!
nvo vxlan id 1007 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF7
!
nvo vxlan id 1008 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF8
!
nvo vxlan id 1009 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF9
!
nvo vxlan id 1010 ingress-replication
vxlan host-reachability-protocol evpn-bgp L2_VRF10
!
evpn mpls vtep-ip-global 24.24.24.24
!
evpn mpls id 100001 interconnect-vnid 1001
host-reachability-protocol evpn-bgp L2_VRF1
!
evpn mpls id 100002 interconnect-vnid 1002
host-reachability-protocol evpn-bgp L2_VRF2
!
evpn mpls id 100003 interconnect-vnid 1003
host-reachability-protocol evpn-bgp L2_VRF3
!
evpn mpls id 100004 interconnect-vnid 1004
host-reachability-protocol evpn-bgp L2_VRF4
!
evpn mpls id 100005 control-word interconnect-vnid 1005
host-reachability-protocol evpn-bgp L2_VRF5
!
evpn mpls id 100006 interconnect-vnid 1006
host-reachability-protocol evpn-bgp L2_VRF6
!
evpn mpls id 100007 flow-label interconnect-vnid 1007
host-reachability-protocol evpn-bgp L2_VRF7
!
evpn mpls id 100008 control-word flow-label interconnect-vnid 1008
host-reachability-protocol evpn-bgp L2_VRF8
!
evpn mpls id 100009 interconnect-vnid 1009
host-reachability-protocol evpn-bgp L2_VRF9
!
evpn mpls id 100010 interconnect-vnid 1010
host-reachability-protocol evpn-bgp L2_VRF10
!
router ldp
router-id 14.14.14.14
transport-address ipv4 14.14.14.14
targeted-peer ipv4 13.13.13.13
exit-targeted-peer-mode
targeted-peer ipv4 15.15.15.15
exit-targeted-peer-mode
targeted-peer ipv4 16.16.16.16
exit-targeted-peer-mode
!
interface ce1
load-interval 30
ip address 101.1.2.2/24
!
interface ce4
load-interval 30
ip address 102.1.2.2/24
!
interface lo
ip address 127.0.0.1/8
ip address 14.14.14.14/32 secondary
ipv6 address ::1/128
!
interface loopback1
ip address 24.24.24.24/32 secondary
!
interface xe47
load-interval 30
ip address 104.1.2.1/24
label-switching
enable-ldp ipv4
!
interface xe48
load-interval 30
ip address 104.1.1.1/24
label-switching
enable-ldp ipv4
!
exit
!
router ospf 100
ospf router-id 14.14.14.14
network 14.14.14.14/32 area 0.0.0.0
network 24.24.24.24/32 area 0.0.0.1
network 101.1.2.0/24 area 0.0.0.0
network 102.1.2.0/24 area 0.0.0.0
network 104.1.1.0/24 area 0.0.0.1
network 104.1.2.0/24 area 0.0.0.1
!
router bgp 65002
bgp router-id 14.14.14.14
bgp bestpath domain-path-id
bgp domain-path-id ipvpn 2323:23
bgp domain-path-id evpn 2324:24
bgp domain-path-id local 2326:26
neighbor 1.1.1.1 remote-as 65001
neighbor 1.1.1.1 ebgp-multihop
neighbor 1.1.1.1 update-source lo
neighbor 2.2.2.2 remote-as 65001
neighbor 2.2.2.2 ebgp-multihop
neighbor 2.2.2.2 update-source lo
neighbor 23.23.23.23 remote-as 65002
neighbor 23.23.23.23 update-source loopback1
neighbor 25.25.25.25 remote-as 65002
neighbor 25.25.25.25 update-source loopback1
neighbor 26.26.26.26 remote-as 65002
neighbor 26.26.26.26 update-source loopback1
!
address-family ipv4 unicast
bgp additional-paths send-receive
exit-address-family
!
address-family vpnv4 unicast
bgp additional-paths send-receive
bgp additional-paths install
multi-path
neighbor 23.23.23.23 activate
neighbor 23.23.23.23 peer-type fabric-external
neighbor 23.23.23.23 allowas-in 1
neighbor 25.25.25.25 activate
neighbor 25.25.25.25 peer-type fabric-external
neighbor 25.25.25.25 allowas-in 1
neighbor 26.26.26.26 activate
neighbor 26.26.26.26 peer-type fabric-external
neighbor 26.26.26.26 allowas-in 1
exit-address-family
!
address-family l2vpn evpn
neighbor 1.1.1.1 activate
neighbor 2.2.2.2 activate
neighbor 23.23.23.23 activate
neighbor 23.23.23.23 peer-type fabric-external
neighbor 23.23.23.23 allowas-in 1
neighbor 25.25.25.25 activate
neighbor 25.25.25.25 peer-type fabric-external
neighbor 25.25.25.25 allowas-in 1
neighbor 26.26.26.26 activate
neighbor 26.26.26.26 peer-type fabric-external
neighbor 26.26.26.26 allowas-in 1
exit-address-family
!
address-family vpnv6 unicast
multi-path
neighbor 23.23.23.23 activate
neighbor 23.23.23.23 peer-type fabric-external
neighbor 23.23.23.23 allowas-in 1
neighbor 25.25.25.25 activate
neighbor 25.25.25.25 peer-type fabric-external
neighbor 25.25.25.25 allowas-in 1
neighbor 26.26.26.26 activate
neighbor 26.26.26.26 peer-type fabric-external
neighbor 26.26.26.26 allowas-in 1
exit-address-family
!
address-family ipv4 vrf L3_VRF1
max-paths ibgp 4
re-originate vpnv4-unicast as l2vpn-evpn
re-originate l2vpn-evpn as vpnv4-unicast
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
address-family ipv6 vrf L3_VRF1
max-paths ibgp 4
re-originate vpnv6-unicast as l2vpn-evpn
re-originate l2vpn-evpn as vpnv6-unicast
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
exit
!
BLEAF3
!
evpn interconnect-mh gw-vtep-ip vxlan 16.16.16.16 mpls 26.26.26.26
!
hardware-profile filter evpn-arp-nd enable
hardware-profile filter vxlan-mh enable
hardware-profile filter evpn-mpls-mh enable
hardware-profile filter evpn-stitch enable
!
nvo vxlan enable
!
nvo vxlan irb
!
evpn mpls enable
!
evpn vxlan multihoming enable
!
evpn irb-forwarding anycast-gateway-mac 0000.0003.abcd
!
evpn mpls multihoming enable
!
ip vrf L3_VRF1
rd 15.15.15.15:101
route-target both 100:2
l3vni 1000
evpn stitching
rd 15.15.15.15:951
route-target both 951:1
host-route-extend-l2vni 1003-1004
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF1
rd 15.15.15.15:1
route-target both 1:2
evpn stitching
rd 15.15.15.15:901
route-target both 901:1
encapsulation mpls
multi-homed iesi 00:22:11:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF10
evpn-vlan-service vlan-based
rd 15.15.15.15:10
route-target both 10:2
evpn stitching
rd 15.15.15.15:910
route-target both 910:1
encapsulation mpls
multi-homed iesi 00:22:99:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF2
rd 15.15.15.15:2
route-target both 2:2
evpn stitching
rd 15.15.15.15:902
route-target both 902:1
encapsulation mpls
multi-homed iesi 00:22:22:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF3
rd 15.15.15.15:3
route-target both 3:2
evpn stitching
rd 15.15.15.15:903
route-target both 903:1
encapsulation mpls
multi-homed iesi 00:22:33:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF4
rd 15.15.15.15:4
route-target both 4:2
evpn stitching
rd 15.15.15.15:904
route-target both 904:1
encapsulation mpls
multi-homed iesi 00:22:44:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF5
rd 15.15.15.15:5
route-target both 5:2
evpn stitching
rd 15.15.15.15:905
route-target both 905:1
encapsulation mpls
multi-homed iesi 00:22:55:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF6
rd 15.15.15.15:6
route-target both 6:2
evpn stitching
rd 15.15.15.15:906
route-target both 906:1
encapsulation mpls
multi-homed iesi 00:22:66:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF7
rd 15.15.15.15:7
route-target both 7:2
evpn stitching
rd 15.15.15.15:907
route-target both 907:1
encapsulation mpls
multi-homed iesi 00:22:77:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF8
evpn-vlan-service vlan-based
rd 15.15.15.15:8
route-target both 8:2
evpn stitching
rd 15.15.15.15:908
route-target both 908:1
encapsulation mpls
multi-homed iesi 00:22:88:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF9
rd 15.15.15.15:9
route-target both 9:2
evpn stitching
rd 15.15.15.15:909
route-target both 909:1
encapsulation mpls
multi-homed iesi 00:22:99:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
nvo vxlan vtep-ip-global 15.15.15.15
!
nvo vxlan id 1001 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF1
!
nvo vxlan id 1002 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF2
!
nvo vxlan id 1003 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF3
!
nvo vxlan id 1004 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF4
!
nvo vxlan id 1005 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF5
!
nvo vxlan id 1006 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF6
!
nvo vxlan id 1007 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF7
!
nvo vxlan id 1008 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF8
!
nvo vxlan id 1009 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF9
!
nvo vxlan id 1010 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF10
!
evpn mpls vtep-ip-global 25.25.25.25
!
evpn mpls id 100001 interconnect-vnid 1001
host-reachability-protocol evpn-bgp L2_VRF1
!
evpn mpls id 100002 interconnect-vnid 1002
host-reachability-protocol evpn-bgp L2_VRF2
!
evpn mpls id 100003 interconnect-vnid 1003
host-reachability-protocol evpn-bgp L2_VRF3
!
evpn mpls id 100004 interconnect-vnid 1004
host-reachability-protocol evpn-bgp L2_VRF4
!
evpn mpls id 100005 control-word interconnect-vnid 1005
host-reachability-protocol evpn-bgp L2_VRF5
!
evpn mpls id 100006 interconnect-vnid 1006
host-reachability-protocol evpn-bgp L2_VRF6
!
evpn mpls id 100007 flow-label interconnect-vnid 1007
host-reachability-protocol evpn-bgp L2_VRF7
!
evpn mpls id 100008 control-word flow-label interconnect-vnid 1008
host-reachability-protocol evpn-bgp L2_VRF8
!
evpn mpls id 100009 interconnect-vnid 1009
host-reachability-protocol evpn-bgp L2_VRF9
!
evpn mpls id 100010 interconnect-vnid 1010
host-reachability-protocol evpn-bgp L2_VRF10
!
router ldp
router-id 15.15.15.15
transport-address ipv4 15.15.15.15
targeted-peer ipv4 13.13.13.13
exit-targeted-peer-mode
targeted-peer ipv4 14.14.14.14
exit-targeted-peer-mode
targeted-peer ipv4 16.16.16.16
exit-targeted-peer-mode
!
interface ce2
load-interval 30
ip address 90.1.1.2/24
!
interface ce4
load-interval 30
ip address 100.1.1.2/24
!
interface ce14/1
load-interval 30
ip address 105.1.1.1/24
label-switching
enable-ldp ipv4
!
interface ce14/2
load-interval 30
ip address 105.1.2.1/24
label-switching
enable-ldp ipv4
!
interface lo
ip address 127.0.0.1/8
ip address 15.15.15.15/32 secondary
ipv6 address ::1/128
!
interface loopback1
ip address 25.25.25.25/32 secondary
!
exit
!
router ospf 100
ospf router-id 15.15.15.15
network 15.15.15.15/32 area 0.0.0.0
network 25.25.25.25/32 area 0.0.0.1
network 90.1.1.0/24 area 0.0.0.0
network 100.1.1.0/24 area 0.0.0.0
network 105.1.1.0/24 area 0.0.0.1
network 105.1.2.0/24 area 0.0.0.1
!
router bgp 65002
bgp router-id 15.15.15.15
bgp bestpath domain-path-id
bgp domain-path-id ipvpn 2523:23
bgp domain-path-id evpn 2524:24
bgp domain-path-id local 2525:25
neighbor 4.4.4.4 remote-as 65003
neighbor 4.4.4.4 ebgp-multihop
neighbor 4.4.4.4 update-source lo
neighbor 5.5.5.5 remote-as 65003
neighbor 5.5.5.5 ebgp-multihop
neighbor 5.5.5.5 update-source lo
neighbor 23.23.23.23 remote-as 65002
neighbor 23.23.23.23 update-source loopback1
neighbor 24.24.24.24 remote-as 65002
neighbor 24.24.24.24 update-source loopback1
neighbor 26.26.26.26 remote-as 65002
neighbor 26.26.26.26 update-source loopback1
!
address-family ipv4 unicast
bgp additional-paths send-receive
exit-address-family
!
address-family vpnv4 unicast
bgp additional-paths send-receive
bgp additional-paths install
multi-path
neighbor 23.23.23.23 activate
neighbor 23.23.23.23 peer-type fabric-external
neighbor 23.23.23.23 allowas-in 1
neighbor 24.24.24.24 activate
neighbor 24.24.24.24 peer-type fabric-external
neighbor 24.24.24.24 allowas-in 1
neighbor 26.26.26.26 activate
neighbor 26.26.26.26 peer-type fabric-external
neighbor 26.26.26.26 allowas-in 1
exit-address-family
!
address-family l2vpn evpn
neighbor 4.4.4.4 activate
neighbor 5.5.5.5 activate
neighbor 23.23.23.23 activate
neighbor 23.23.23.23 peer-type fabric-external
neighbor 23.23.23.23 allowas-in 1
neighbor 24.24.24.24 activate
neighbor 24.24.24.24 peer-type fabric-external
neighbor 24.24.24.24 allowas-in 1
neighbor 26.26.26.26 activate
neighbor 26.26.26.26 peer-type fabric-external
neighbor 26.26.26.26 allowas-in 1
exit-address-family
!
address-family vpnv6 unicast
multi-path
neighbor 23.23.23.23 activate
neighbor 23.23.23.23 peer-type fabric-external
neighbor 23.23.23.23 allowas-in 1
neighbor 24.24.24.24 activate
neighbor 24.24.24.24 peer-type fabric-external
neighbor 24.24.24.24 allowas-in 1
neighbor 26.26.26.26 activate
neighbor 26.26.26.26 peer-type fabric-external
neighbor 26.26.26.26 allowas-in 1
exit-address-family
!
address-family ipv4 vrf L3_VRF1
max-paths ibgp 4
re-originate vpnv4-unicast as l2vpn-evpn
re-originate l2vpn-evpn as vpnv4-unicast
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
address-family ipv6 vrf L3_VRF1
max-paths ibgp 4
re-originate vpnv6-unicast as l2vpn-evpn
re-originate l2vpn-evpn as vpnv6-unicast
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
exit
BLEAF4
!
evpn interconnect-mh gw-vtep-ip vxlan 15.15.15.15 mpls 25.25.25.25
!
hardware-profile filter evpn-arp-nd enable
hardware-profile filter vxlan-mh enable
hardware-profile filter evpn-mpls-mh enable
hardware-profile filter evpn-stitch enable
!
nvo vxlan enable
!
nvo vxlan irb
!
evpn mpls enable
!
evpn vxlan multihoming enable
!
evpn irb-forwarding anycast-gateway-mac 0000.0003.abcd
!
evpn mpls multihoming enable
!
ip vrf L3_VRF1
rd 16.16.16.16:101
route-target both 100:2
l3vni 1000
evpn stitching
rd 16.16.16.16:951
route-target both 951:1
host-route-extend-l2vni 1003-1004
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF1
rd 16.16.16.16:1
route-target both 1:2
evpn stitching
rd 16.16.16.16:901
route-target both 901:1
encapsulation mpls
multi-homed iesi 00:22:11:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF10
evpn-vlan-service vlan-based
rd 16.16.16.16:10
route-target both 10:2
evpn stitching
rd 16.16.16.16:910
route-target both 910:1
encapsulation mpls
multi-homed iesi 00:22:99:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF2
rd 16.16.16.16:2
route-target both 2:2
evpn stitching
rd 16.16.16.16:902
route-target both 902:1
encapsulation mpls
multi-homed iesi 00:22:22:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF3
rd 16.16.16.16:3
route-target both 3:2
evpn stitching
rd 16.16.16.16:903
route-target both 903:1
encapsulation mpls
multi-homed iesi 00:22:33:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF4
rd 16.16.16.16:4
route-target both 4:2
evpn stitching
rd 16.16.16.16:904
route-target both 904:1
encapsulation mpls
multi-homed iesi 00:22:44:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF5
rd 16.16.16.16:5
route-target both 5:2
evpn stitching
rd 16.16.16.16:905
route-target both 905:1
encapsulation mpls
multi-homed iesi 00:22:55:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF6
rd 16.16.16.16:6
route-target both 6:2
evpn stitching
rd 16.16.16.16:906
route-target both 906:1
encapsulation mpls
multi-homed iesi 00:22:66:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF7
rd 16.16.16.16:7
route-target both 7:2
evpn stitching
rd 16.16.16.16:907
route-target both 907:1
encapsulation mpls
multi-homed iesi 00:22:77:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF8
evpn-vlan-service vlan-based
rd 16.16.16.16:8
route-target both 8:2
evpn stitching
rd 16.16.16.16:908
route-target both 908:1
encapsulation mpls
multi-homed iesi 00:22:88:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
mac vrf L2_VRF9
rd 16.16.16.16:9
route-target both 9:2
evpn stitching
rd 16.16.16.16:909
route-target both 909:1
encapsulation mpls
multi-homed iesi 00:22:99:11:11:11:11:11:11 all-active
exit-config-vrf-evpn-mode
!
nvo vxlan vtep-ip-global 16.16.16.16
!
nvo vxlan id 1001 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF1
!
nvo vxlan id 1002 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF2
!
nvo vxlan id 1003 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF3
!
nvo vxlan id 1004 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF4
!
nvo vxlan id 1005 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF5
!
nvo vxlan id 1006 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF6
!
nvo vxlan id 1007 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF7
!
nvo vxlan id 1008 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF8
!
nvo vxlan id 1009 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF9
!
nvo vxlan id 1010 ingress-replication inner-vid-disabled
vxlan host-reachability-protocol evpn-bgp L2_VRF10
!
evpn mpls vtep-ip-global 26.26.26.26
!
evpn mpls id 100001 interconnect-vnid 1001
host-reachability-protocol evpn-bgp L2_VRF1
!
evpn mpls id 100002 interconnect-vnid 1002
host-reachability-protocol evpn-bgp L2_VRF2
!
evpn mpls id 100003 interconnect-vnid 1003
host-reachability-protocol evpn-bgp L2_VRF3
!
evpn mpls id 100004 interconnect-vnid 1004
host-reachability-protocol evpn-bgp L2_VRF4
!
evpn mpls id 100005 control-word interconnect-vnid 1005
host-reachability-protocol evpn-bgp L2_VRF5
!
evpn mpls id 100006 interconnect-vnid 1006
host-reachability-protocol evpn-bgp L2_VRF6
!
evpn mpls id 100007 flow-label interconnect-vnid 1007
host-reachability-protocol evpn-bgp L2_VRF7
!
evpn mpls id 100008 control-word flow-label interconnect-vnid 1008
host-reachability-protocol evpn-bgp L2_VRF8
!
evpn mpls id 100009 interconnect-vnid 1009
host-reachability-protocol evpn-bgp L2_VRF9
!
evpn mpls id 100010 interconnect-vnid 1010
host-reachability-protocol evpn-bgp L2_VRF10
!
router ldp
router-id 16.16.16.16
transport-address ipv4 16.16.16.16
targeted-peer ipv4 13.13.13.13
exit-targeted-peer-mode
targeted-peer ipv4 14.14.14.14
exit-targeted-peer-mode
targeted-peer ipv4 15.15.15.15
exit-targeted-peer-mode
!
interface ce2
load-interval 30
ip address 90.1.2.2/24
!
interface ce3
load-interval 30
ip address 100.1.2.2/24
!
interface lo
ip address 127.0.0.1/8
ip address 16.16.16.16/32 secondary
ipv6 address ::1/128
!
interface loopback1
ip address 26.26.26.26/32 secondary
!
interface xe10
load-interval 30
ip address 106.1.1.1/24
label-switching
enable-ldp ipv4
!
interface xe11
load-interval 30
ip address 106.1.2.1/24
label-switching
enable-ldp ipv4
!
exit
!
router ospf 100
ospf router-id 16.16.16.16
network 16.16.16.16/32 area 0.0.0.0
network 26.26.26.26/32 area 0.0.0.1
network 90.1.2.0/24 area 0.0.0.0
network 100.1.2.0/24 area 0.0.0.0
network 106.1.1.0/24 area 0.0.0.1
network 106.1.2.0/24 area 0.0.0.1
!
router bgp 65002
bgp router-id 16.16.16.16
bgp bestpath domain-path-id
bgp domain-path-id ipvpn 2523:23
bgp domain-path-id evpn 2524:24
bgp domain-path-id local 2526:26
neighbor 4.4.4.4 remote-as 65003
neighbor 4.4.4.4 ebgp-multihop
neighbor 4.4.4.4 update-source lo
neighbor 5.5.5.5 remote-as 65003
neighbor 5.5.5.5 ebgp-multihop
neighbor 5.5.5.5 update-source lo
neighbor 23.23.23.23 remote-as 65002
neighbor 23.23.23.23 update-source loopback1
neighbor 24.24.24.24 remote-as 65002
neighbor 24.24.24.24 update-source loopback1
neighbor 25.25.25.25 remote-as 65002
neighbor 25.25.25.25 update-source loopback1
!
address-family ipv4 unicast
bgp additional-paths send-receive
exit-address-family
!
address-family vpnv4 unicast
bgp additional-paths send-receive
bgp additional-paths install
multi-path
neighbor 23.23.23.23 activate
neighbor 23.23.23.23 peer-type fabric-external
neighbor 23.23.23.23 allowas-in 1
neighbor 24.24.24.24 activate
neighbor 24.24.24.24 peer-type fabric-external
neighbor 24.24.24.24 allowas-in 1
neighbor 25.25.25.25 activate
neighbor 25.25.25.25 peer-type fabric-external
neighbor 25.25.25.25 allowas-in 1
exit-address-family
!
address-family l2vpn evpn
neighbor 4.4.4.4 activate
neighbor 5.5.5.5 activate
neighbor 23.23.23.23 activate
neighbor 23.23.23.23 peer-type fabric-external
neighbor 23.23.23.23 allowas-in 1
neighbor 24.24.24.24 activate
neighbor 24.24.24.24 peer-type fabric-external
neighbor 24.24.24.24 allowas-in 1
neighbor 25.25.25.25 activate
neighbor 25.25.25.25 peer-type fabric-external
neighbor 25.25.25.25 allowas-in 1
exit-address-family
!
address-family vpnv6 unicast
multi-path
neighbor 23.23.23.23 activate
neighbor 23.23.23.23 peer-type fabric-external
neighbor 23.23.23.23 allowas-in 1
neighbor 24.24.24.24 activate
neighbor 24.24.24.24 peer-type fabric-external
neighbor 24.24.24.24 allowas-in 1
neighbor 25.25.25.25 activate
neighbor 25.25.25.25 peer-type fabric-external
neighbor 25.25.25.25 allowas-in 1
exit-address-family
!
address-family ipv4 vrf L3_VRF1
max-paths ibgp 4
re-originate vpnv4-unicast as l2vpn-evpn
re-originate l2vpn-evpn as vpnv4-unicast
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
address-family ipv6 vrf L3_VRF1
max-paths ibgp 4
re-originate vpnv6-unicast as l2vpn-evpn
re-originate l2vpn-evpn as vpnv6-unicast
bgp additional-paths send-receive
bgp additional-paths select all
redistribute connected
bgp bestpath as-path multipath-relax
exit-address-family
!
Exit
Validation
=============================================
R1
=============================================
R1#show ip ospf neighbor
Total number of full neighbors: 4
OSPF process 100 VRF(default):
Neighbor ID Pri State Dead Time Address Interface Instance ID
13.13.13.13 1 Full/Backup 00:00:34 103.1.1.1 xe2 0
14.14.14.14 1 Full/Backup 00:00:36 104.1.1.1 xe16 0
15.15.15.15 1 Full/Backup 00:00:35 105.1.1.1 xe19 0
16.16.16.16 1 Full/Backup 00:00:37 106.1.1.1 xe14 0
R1#show ldp session
Codes: m - MD5 password is not set/unset.
g - GR configuration not set/unset.
t - TCP MSS not set/unset.
Session has to be cleared manually
Code Peer IP Address IF Name My Role State KeepAlive UpTime AutoCreate
13.13.13.13 xe2 Active OPERATIONAL 30 00:16:16 No
16.16.16.16 xe14 Active OPERATIONAL 30 00:18:46 No
14.14.14.14 xe16 Active OPERATIONAL 30 00:14:47 No
15.15.15.15 xe19 Active OPERATIONAL 30 00:17:51 No
R1#
=============================================
R2
=============================================
R2#show ip ospf neighbor
Total number of full neighbors: 4
OSPF process 100 VRF(default):
Neighbor ID Pri State Dead Time Address Interface Instance ID
13.13.13.13 1 Full/Backup 00:00:35 103.1.2.1 ce0 0
14.14.14.14 1 Full/Backup 00:00:35 104.1.2.1 xe16 0
15.15.15.15 1 Full/Backup 00:00:33 105.1.2.1 xe22 0
16.16.16.16 1 Full/Backup 00:00:32 106.1.2.1 xe14 0
R2#show ldp session
Codes: m - MD5 password is not set/unset.
g - GR configuration not set/unset.
t - TCP MSS not set/unset.
Session has to be cleared manually
Code Peer IP Address IF Name My Role State KeepAlive UpTime AutoCreate
13.13.13.13 ce0 Active OPERATIONAL 30 00:17:07 No
16.16.16.16 xe14 Active OPERATIONAL 30 00:19:15 No
14.14.14.14 xe16 Active OPERATIONAL 30 00:15:17 No
15.15.15.15 xe22 Active OPERATIONAL 30 00:18:25 No
R2#
=============================================
SWITCH1
=============================================
SWITCH1#show etherchannel summary
Aggregator po100 100100
Aggregator Type: Layer2
Admin Key: 0100 - Oper Key 0100
Link: ce55 (5056) sync: 1
Link: ce56 (5057) sync: 1
SWITCH1#
=============================================
SWITCH2
=============================================
SWITCH2#show etherchannel summary
Aggregator po200 100200
Aggregator Type: Layer2
Admin Key: 0200 - Oper Key 0200
Link: xe19 (5017) sync: 1
Link: xe51/1 (5059) sync: 1
SWITCH2#
=============================================
VTEP1
=============================================
VTEP1#show ip ospf neighbor
Total number of full neighbors: 2
OSPF process 100 VRF(default):
Neighbor ID Pri State Dead Time Address Interface Instance ID
11.11.11.11 1 Full/DR 00:00:32 10.1.1.2 ce2 0
12.12.12.12 1 Full/DR 00:00:34 10.1.2.2 ce1 0
VTEP1#show bgp l2vpn evpn summary
BGP router identifier 1.1.1.1, local AS number 65001
BGP table version is 43
3 BGP AS-PATH entries
0 BGP community entries
Neighbor V AS MsgRcv MsgSen TblVer InQ OutQ Up/Down State/PfxRcd AD MACIP MCAST ESI PREFIX-ROUTE Desc
2.2.2.2 4 65001 231 211 43 0 0 00:19:51 595 49 503 30 1 12
13.13.13.13 4 65002 165 248 43 0 0 00:18:24 264 19 231 10 0 4
14.14.14.14 4 65002 128 289 43 0 0 00:16:37 191 19 158 10 0 4
Total number of neighbors 3
Total number of Established sessions 3
VTEP1#show nvo vxlan
VXLAN Information
=================
Codes: NW - Network Port
AC - Access Port
(u) - Untagged
VNID VNI-Name VNI-Type Type Intr-VNID Interface ESI VLAN DF-Status Src-Addr Dst-Addr Router-Mac
_______________________________________________________________________________________________________________________________________________________________
1000 ---- L3 NW ---- ---- ---- ---- ---- 1.1.1.1 13.13.13.13 5c07.5851.cb50
1000 ---- L3 NW ---- ---- ---- ---- ---- 1.1.1.1 14.14.14.14 5c07.58d4.9b00
1000 ---- L3 NW ---- ---- ---- ---- ---- 1.1.1.1 2.2.2.2 e001.a6a9.4b01
1001 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 13.13.13.13 --------------
1001 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 14.14.14.14 --------------
1001 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 2.2.2.2 --------------
1001 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1001 NON-DF ---- ----
1002 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 13.13.13.13 --------------
1002 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 14.14.14.14 --------------
1002 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 2.2.2.2 --------------
1002 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1002 DF ---- ----
1003 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 13.13.13.13 --------------
1003 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 14.14.14.14 --------------
1003 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 2.2.2.2 --------------
1003 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1003 NON-DF ---- ----
1004 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 13.13.13.13 --------------
1004 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 14.14.14.14 --------------
1004 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 2.2.2.2 --------------
1004 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1004 DF ---- ----
1005 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 13.13.13.13 --------------
1005 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 14.14.14.14 --------------
1005 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 2.2.2.2 --------------
1005 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1005 NON-DF ---- ----
1006 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 13.13.13.13 --------------
1006 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 14.14.14.14 --------------
1006 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 2.2.2.2 --------------
1006 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1006 DF ---- ----
1007 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 13.13.13.13 --------------
1007 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 14.14.14.14 --------------
1007 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 2.2.2.2 --------------
1007 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1007 NON-DF ---- ----
1008 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 13.13.13.13 --------------
1008 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 14.14.14.14 --------------
1008 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 2.2.2.2 --------------
1008 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1008 DF ---- ----
1009 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 13.13.13.13 --------------
1009 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 14.14.14.14 --------------
1009 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 2.2.2.2 --------------
1009 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1009 NON-DF ---- ----
1010 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 13.13.13.13 --------------
1010 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 14.14.14.14 --------------
1010 ---- L2 NW ---- ---- ---- ---- ---- 1.1.1.1 2.2.2.2 --------------
1010 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1010 DF ---- ----
Total number of entries are 43
VTEP1#show nvo vxlan tunnel
VXLAN Network tunnel Entries
Source Destination Status Up/Down Update
========================================================================
1.1.1.1 13.13.13.13 Installed 00:18:26 00:18:21
1.1.1.1 14.14.14.14 Installed 00:16:38 00:16:38
1.1.1.1 2.2.2.2 Installed 00:19:53 00:19:29
Total number of entries are 3
VTEP1#show nvo vxlan access-if brief
Inner Admin Link
Interface Vlan vlan Ifindex Vnid status status
---------------------------------------------------------------
po100 1001 --- 0x7a120 1001 up up
po100 1002 --- 0x7a121 1002 up up
po100 1003 --- 0x7a122 1003 up up
po100 1004 --- 0x7a123 1004 up up
po100 1005 --- 0x7a124 1005 up up
po100 1006 --- 0x7a125 1006 up up
po100 1007 --- 0x7a126 1007 up up
po100 1008 --- 0x7a127 1008 up up
po100 1009 --- 0x7a128 1009 up up
po100 1010 --- 0x7a129 1010 up up
Total number of entries are 10
VTEP1#show etherchannel summary
Aggregator po100 100100
Aggregator Type: Layer2
Admin Key: 0100 - Oper Key 0100
Link: ce32 (5033) sync: 1
VTEP1#show ip route vrf L3_VRF1
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2,
ia - IS-IS inter area, E - EVPN,
v - vrf leaked, g - imported from global
* - candidate default
IP Route Table for VRF "L3_VRF1"
B 2.2.2.2/32 [0/0] is directly connected, tunvxlan2, installed 00:20:07, last update 00:20:07 ago
B 13.13.13.13/32 [0/0] is directly connected, tunvxlan2, installed 00:18:14, last update 00:18:14 ago
B 14.14.14.14/32 [0/0] is directly connected, tunvxlan2, installed 00:16:53, last update 00:16:53 ago
C 101.101.1.0/24 is directly connected, irb1001, installed 00:22:54, last update 00:22:54 ago
B 102.101.1.0/24 [20/0] via 14.14.14.14 (recursive is directly connected, tunvxlan2), installed 00:18:14, last update 00:16:53 ago
[20/0] via 13.13.13.13 (recursive is directly connected, tunvxlan2)
C 127.0.0.0/8 is directly connected, lo.L3_VRF1, installed 00:22:54, last update 00:22:54 ago
B 201.101.1.0/24 [200/0] via 2.2.2.2 (recursive is directly connected, tunvxlan2), installed 00:20:07, last update 00:20:07 ago
B 202.101.1.0/24 [20/0] via 14.14.14.14 (recursive is directly connected, tunvxlan2), installed 00:18:14, last update 00:16:53 ago
[20/0] via 13.13.13.13 (recursive is directly connected, tunvxlan2)
Gateway of last resort is not set
VTEP1#show ipv6 route vrf L3_VRF1
IPv6 Routing Table
Codes: K - kernel route, C - connected, S - static, D- DHCP, R - RIP,
O - OSPF, IA - OSPF inter area, E1 - OSPF external type 1,
E2 - OSPF external type 2, E - EVPN N1 - OSPF NSSA external type 1,
N2 - OSPF NSSA external type 2, i - IS-IS, B - BGP,
v - vrf leaked, g - imported from global
Timers: Uptime
IP Route Table for VRF "L3_VRF1"
C ::1/128 via ::, lo.L3_VRF1, installed 00:22:59, last update 00:22:59 ago
B ::ffff:202:202/128 [0/0] via ::, tunvxlan2, installed 00:20:12, last update 00:20:12 ago
B ::ffff:d0d:d0d/128 [0/0] via ::, tunvxlan2, installed 00:18:19, last update 00:18:19 ago
B ::ffff:e0e:e0e/128 [0/0] via ::, tunvxlan2, installed 00:16:58, last update 00:16:58 ago
C 101::/64 via ::, irb1001, installed 00:22:59, last update 00:22:59 ago
B 102::/64 [20/0] via ::ffff:e0e:e0e (recursive via ::, tunvxlan2), installed 00:18:19, last update 00:16:58 ago
[20/0] via ::ffff:d0d:d0d (recursive via ::, tunvxlan2)
B 201::/64 [200/0] via ::ffff:202:202 (recursive via ::, tunvxlan2), installed 00:20:12, last update 00:20:12 ago
B 202::/64 [20/0] via ::ffff:e0e:e0e (recursive via ::, tunvxlan2), installed 00:18:19, last update 00:16:58 ago
[20/0] via ::ffff:d0d:d0d (recursive via ::, tunvxlan2)
C fe80::/64 via ::, tunvxlan2, installed 00:22:58, last update 00:22:58 ago
VTEP1#
VTEP1#show bgp l2vpn evpn prefix-route
BGP table version is 43, local router ID is 1.1.1.1
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal,
l - labeled, S Stale w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Description : Ext-Color - Extended community color
RD[2.2.2.2:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*>i0 0 24 101.101.1.0 0.0.0.0 1000 2.2.2.2 2.2.2.2 VXLAN e001:a6a9:4b01
*>i0 0 24 201.101.1.0 0.0.0.0 1000 2.2.2.2 2.2.2.2 VXLAN e001:a6a9:4b01
*>i0 0 64 101:: :: 1000 2.2.2.2 2.2.2.2 VXLAN e001:a6a9:4b01
*>i0 0 64 201:: :: 1000 2.2.2.2 2.2.2.2 VXLAN e001:a6a9:4b01
RD[13.13.13.13:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 102.101.1.0 0.0.0.0 1000 13.13.13.13 13.13.13.13 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 24 102.101.1.0 0.0.0.0 1000 13.13.13.13 2.2.2.2 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
*> 0 0 24 202.101.1.0 0.0.0.0 1000 13.13.13.13 13.13.13.13 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 24 202.101.1.0 0.0.0.0 1000 13.13.13.13 2.2.2.2 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
*> 0 0 64 102:: :: 1000 13.13.13.13 13.13.13.13 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 64 102:: :: 1000 13.13.13.13 2.2.2.2 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
*> 0 0 64 202:: :: 1000 13.13.13.13 13.13.13.13 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 64 202:: :: 1000 13.13.13.13 2.2.2.2 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
RD[14.14.14.14:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 102.101.1.0 0.0.0.0 1000 14.14.14.14 14.14.14.14 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 24 102.101.1.0 0.0.0.0 1000 14.14.14.14 2.2.2.2 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
*> 0 0 24 202.101.1.0 0.0.0.0 1000 14.14.14.14 14.14.14.14 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 24 202.101.1.0 0.0.0.0 1000 14.14.14.14 2.2.2.2 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
*> 0 0 64 102:: :: 1000 14.14.14.14 14.14.14.14 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 64 102:: :: 1000 14.14.14.14 2.2.2.2 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
*> 0 0 64 202:: :: 1000 14.14.14.14 14.14.14.14 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 64 202:: :: 1000 14.14.14.14 2.2.2.2 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
VTEP1#
=============================================
VTEP2
=============================================
VTEP2#show ip ospf neighbor
Total number of full neighbors: 2
OSPF process 100 VRF(default):
Neighbor ID Pri State Dead Time Address Interface Instance ID
11.11.11.11 1 Full/DR 00:00:39 20.1.1.2 xe33 0
12.12.12.12 1 Full/DR 00:00:31 20.1.2.2 ce2 0
VTEP2#show bgp l2vpn evpn summary
BGP router identifier 2.2.2.2, local AS number 65001
BGP table version is 41
3 BGP AS-PATH entries
0 BGP community entries
Neighbor V AS MsgRcv MsgSen TblVer InQ OutQ Up/Down State/PfxRcd AD MACIP MCAST ESI PREFIX-ROUTE Desc
1.1.1.1 4 65001 213 234 41 0 0 00:21:19 525 49 435 30 1 10
13.13.13.13 4 65002 135 230 41 0 0 00:19:52 264 19 231 10 0 4
14.14.14.14 4 65002 130 212 41 0 0 00:18:04 191 19 158 10 0 4
Total number of neighbors 3
Total number of Established sessions 3
VTEP2#show nvo vxlan
VXLAN Information
=================
Codes: NW - Network Port
AC - Access Port
(u) - Untagged
VNID VNI-Name VNI-Type Type Intr-VNID Interface ESI VLAN DF-Status Src-Addr Dst-Addr Router-Mac
_______________________________________________________________________________________________________________________________________________________________
1000 ---- L3 NW ---- ---- ---- ---- ---- 2.2.2.2 1.1.1.1 1444.8f6c.47ec
1000 ---- L3 NW ---- ---- ---- ---- ---- 2.2.2.2 13.13.13.13 5c07.5851.cb50
1000 ---- L3 NW ---- ---- ---- ---- ---- 2.2.2.2 14.14.14.14 5c07.58d4.9b00
1001 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 1.1.1.1 --------------
1001 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 13.13.13.13 --------------
1001 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 14.14.14.14 --------------
1001 ---- -- AC ---- ce29 --- Single Homed Port --- 1001 ---- ---- ----
1001 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1001 DF ---- ----
1002 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 1.1.1.1 --------------
1002 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 13.13.13.13 --------------
1002 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 14.14.14.14 --------------
1002 ---- -- AC ---- ce29 --- Single Homed Port --- 1002 ---- ---- ----
1002 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1002 NON-DF ---- ----
1003 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 1.1.1.1 --------------
1003 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 13.13.13.13 --------------
1003 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 14.14.14.14 --------------
1003 ---- -- AC ---- ce29 --- Single Homed Port --- 1003 ---- ---- ----
1003 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1003 DF ---- ----
1004 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 1.1.1.1 --------------
1004 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 13.13.13.13 --------------
1004 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 14.14.14.14 --------------
1004 ---- -- AC ---- ce29 --- Single Homed Port --- 1004 ---- ---- ----
1004 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1004 NON-DF ---- ----
1005 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 1.1.1.1 --------------
1005 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 13.13.13.13 --------------
1005 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 14.14.14.14 --------------
1005 ---- -- AC ---- ce29 --- Single Homed Port --- 1005 ---- ---- ----
1005 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1005 DF ---- ----
1006 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 1.1.1.1 --------------
1006 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 13.13.13.13 --------------
1006 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 14.14.14.14 --------------
1006 ---- -- AC ---- ce29 --- Single Homed Port --- 1006 ---- ---- ----
1006 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1006 NON-DF ---- ----
1007 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 1.1.1.1 --------------
1007 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 13.13.13.13 --------------
1007 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 14.14.14.14 --------------
1007 ---- -- AC ---- ce29 --- Single Homed Port --- 1007 ---- ---- ----
1007 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1007 DF ---- ----
1008 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 1.1.1.1 --------------
1008 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 13.13.13.13 --------------
1008 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 14.14.14.14 --------------
1008 ---- -- AC ---- ce29 --- Single Homed Port --- 1008 ---- ---- ----
1008 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1008 NON-DF ---- ----
1009 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 1.1.1.1 --------------
1009 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 13.13.13.13 --------------
1009 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 14.14.14.14 --------------
1009 ---- -- AC ---- ce29 --- Single Homed Port --- 1009 ---- ---- ----
1009 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1009 DF ---- ----
1010 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 1.1.1.1 --------------
1010 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 13.13.13.13 --------------
1010 ---- L2 NW ---- ---- ---- ---- ---- 2.2.2.2 14.14.14.14 --------------
1010 ---- -- AC ---- ce29 --- Single Homed Port --- 1010 ---- ---- ----
1010 ---- -- AC ---- po100 00:00:00:99:99:11:11:00:00:00 1010 NON-DF ---- ----
Total number of entries are 53
VTEP2#show nvo vxlan tunnel
VXLAN Network tunnel Entries
Source Destination Status Up/Down Update
========================================================================
2.2.2.2 1.1.1.1 Installed 00:21:17 00:20:54
2.2.2.2 13.13.13.13 Installed 00:19:51 00:19:46
2.2.2.2 14.14.14.14 Installed 00:18:02 00:18:02
Total number of entries are 3
VTEP2#show nvo vxlan access-if brief
Inner Admin Link
Interface Vlan vlan Ifindex Vnid status status
---------------------------------------------------------------
ce29 1001 --- 0x7a120 1001 up up
ce29 1002 --- 0x7a121 1002 up up
ce29 1003 --- 0x7a122 1003 up up
ce29 1004 --- 0x7a123 1004 up up
ce29 1005 --- 0x7a124 1005 up up
ce29 1006 --- 0x7a125 1006 up up
ce29 1007 --- 0x7a126 1007 up up
ce29 1008 --- 0x7a127 1008 up up
ce29 1009 --- 0x7a128 1009 up up
ce29 1010 --- 0x7a129 1010 up up
po100 1001 --- 0x7a12a 1001 up up
po100 1002 --- 0x7a12b 1002 up up
po100 1003 --- 0x7a12c 1003 up up
po100 1004 --- 0x7a12d 1004 up up
po100 1005 --- 0x7a12e 1005 up up
po100 1006 --- 0x7a12f 1006 up up
po100 1007 --- 0x7a130 1007 up up
po100 1008 --- 0x7a131 1008 up up
po100 1009 --- 0x7a132 1009 up up
po100 1010 --- 0x7a133 1010 up up
Total number of entries are 20
VTEP2#show etherchannel summary
Aggregator po100 100100
Aggregator Type: Layer2
Admin Key: 0100 - Oper Key 0100
Link: ce32 (5033) sync: 1
VTEP2#show ip route vrf L3_VRF1
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2,
ia - IS-IS inter area, E - EVPN,
v - vrf leaked, g - imported from global
* - candidate default
IP Route Table for VRF "L3_VRF1"
B 1.1.1.1/32 [0/0] is directly connected, tunvxlan2, installed 00:21:18, last update 00:21:18 ago
B 13.13.13.13/32 [0/0] is directly connected, tunvxlan2, installed 00:19:24, last update 00:19:24 ago
B 14.14.14.14/32 [0/0] is directly connected, tunvxlan2, installed 00:18:03, last update 00:18:03 ago
C 101.101.1.0/24 is directly connected, irb1001, installed 00:23:59, last update 00:23:59 ago
B 102.101.1.0/24 [20/0] via 14.14.14.14 (recursive is directly connected, tunvxlan2), installed 00:19:22, last update 00:18:03 ago
[20/0] via 13.13.13.13 (recursive is directly connected, tunvxlan2)
C 127.0.0.0/8 is directly connected, lo.L3_VRF1, installed 00:24:01, last update 00:24:01 ago
C 201.101.1.0/24 is directly connected, irb1002, installed 00:23:59, last update 00:23:59 ago
B 202.101.1.0/24 [20/0] via 14.14.14.14 (recursive is directly connected, tunvxlan2), installed 00:19:22, last update 00:18:03 ago
[20/0] via 13.13.13.13 (recursive is directly connected, tunvxlan2)
Gateway of last resort is not set
VTEP2#show ipv6 route vrf L3_VRF1
IPv6 Routing Table
Codes: K - kernel route, C - connected, S - static, D- DHCP, R - RIP,
O - OSPF, IA - OSPF inter area, E1 - OSPF external type 1,
E2 - OSPF external type 2, E - EVPN N1 - OSPF NSSA external type 1,
N2 - OSPF NSSA external type 2, i - IS-IS, B - BGP,
v - vrf leaked, g - imported from global
Timers: Uptime
IP Route Table for VRF "L3_VRF1"
C ::1/128 via ::, lo.L3_VRF1, installed 00:24:01, last update 00:24:01 ago
B ::ffff:101:101/128 [0/0] via ::, tunvxlan2, installed 00:21:18, last update 00:21:18 ago
B ::ffff:d0d:d0d/128 [0/0] via ::, tunvxlan2, installed 00:19:24, last update 00:19:24 ago
B ::ffff:e0e:e0e/128 [0/0] via ::, tunvxlan2, installed 00:18:03, last update 00:18:03 ago
C 101::/64 via ::, irb1001, installed 00:23:59, last update 00:23:59 ago
B 102::/64 [20/0] via ::ffff:e0e:e0e (recursive via ::, tunvxlan2), installed 00:19:22, last update 00:18:03 ago
[20/0] via ::ffff:d0d:d0d (recursive via ::, tunvxlan2)
C 201::/64 via ::, irb1002, installed 00:23:59, last update 00:23:59 ago
B 202::/64 [20/0] via ::ffff:e0e:e0e (recursive via ::, tunvxlan2), installed 00:19:22, last update 00:18:03 ago
[20/0] via ::ffff:d0d:d0d (recursive via ::, tunvxlan2)
C fe80::/64 via ::, irb1002, installed 00:23:46, last update 00:23:46 ago
VTEP2#show bgp l2vpn evpn prefix-route
BGP table version is 41, local router ID is 2.2.2.2
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal,
l - labeled, S Stale w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Description : Ext-Color - Extended community color
RD[1.1.1.1:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*>i0 0 24 101.101.1.0 0.0.0.0 1000 1.1.1.1 1.1.1.1 VXLAN 1444:8f6c:47ec
*>i0 0 64 101:: :: 1000 1.1.1.1 1.1.1.1 VXLAN 1444:8f6c:47ec
RD[13.13.13.13:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 102.101.1.0 0.0.0.0 1000 13.13.13.13 13.13.13.13 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 24 102.101.1.0 0.0.0.0 1000 13.13.13.13 1.1.1.1 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
*> 0 0 24 202.101.1.0 0.0.0.0 1000 13.13.13.13 13.13.13.13 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 24 202.101.1.0 0.0.0.0 1000 13.13.13.13 1.1.1.1 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
*> 0 0 64 102:: :: 1000 13.13.13.13 13.13.13.13 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 64 102:: :: 1000 13.13.13.13 1.1.1.1 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
*> 0 0 64 202:: :: 1000 13.13.13.13 13.13.13.13 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 64 202:: :: 1000 13.13.13.13 1.1.1.1 VXLAN 5c07:5851:cb50 2524:24:70(evpn), 2323:23:128(ipvpn)
RD[14.14.14.14:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 102.101.1.0 0.0.0.0 1000 14.14.14.14 14.14.14.14 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 24 102.101.1.0 0.0.0.0 1000 14.14.14.14 1.1.1.1 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
*> 0 0 24 202.101.1.0 0.0.0.0 1000 14.14.14.14 14.14.14.14 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 24 202.101.1.0 0.0.0.0 1000 14.14.14.14 1.1.1.1 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
*> 0 0 64 102:: :: 1000 14.14.14.14 14.14.14.14 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 64 102:: :: 1000 14.14.14.14 1.1.1.1 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
*> 0 0 64 202:: :: 1000 14.14.14.14 14.14.14.14 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
* i0 0 64 202:: :: 1000 14.14.14.14 1.1.1.1 VXLAN 5c07:58d4:9b00 2524:24:70(evpn), 2323:23:128(ipvpn)
VTEP2#
=============================================
VTEP4
=============================================
VTEP4#show ip ospf neighbor
Total number of full neighbors: 2
OSPF process 100 VRF(default):
Neighbor ID Pri State Dead Time Address Interface Instance ID
9.9.9.9 1 Full/DR 00:00:33 40.1.1.2 ce50/1 0
10.10.10.10 1 Full/DR 00:00:37 40.1.2.2 ce54/1 0
VTEP4#show bgp l2vpn evpn summary
BGP router identifier 4.4.4.4, local AS number 65003
BGP table version is 45
3 BGP AS-PATH entries
0 BGP community entries
Neighbor V AS MsgRcv MsgSen TblVer InQ OutQ Up/Down State/PfxRcd AD MACIP MCAST ESI PREFIX-ROUTE Desc
5.5.5.5 4 65003 276 266 45 0 0 00:21:50 668 49 576 30 1 12
15.15.15.15 4 65002 177 302 45 0 0 00:21:39 264 19 231 10 0 4
16.16.16.16 4 65002 200 293 45 0 0 00:21:53 264 19 231 10 0 4
Total number of neighbors 3
Total number of Established sessions 3
VTEP4#show nvo vxlan
VXLAN Information
=================
Codes: NW - Network Port
AC - Access Port
(u) - Untagged
VNID VNI-Name VNI-Type Type Intr-VNID Interface ESI VLAN DF-Status Src-Addr Dst-Addr Router-Mac
_______________________________________________________________________________________________________________________________________________________________
1000 ---- L3 NW ---- ---- ---- ---- ---- 4.4.4.4 15.15.15.15 342c.8e5d.b9cc
1000 ---- L3 NW ---- ---- ---- ---- ---- 4.4.4.4 16.16.16.16 4445.ba13.ba01
1000 ---- L3 NW ---- ---- ---- ---- ---- 4.4.4.4 5.5.5.5 5c17.83ff.2255
1001 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 15.15.15.15 --------------
1001 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 16.16.16.16 --------------
1001 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 5.5.5.5 --------------
1001 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1001 NON-DF ---- ----
1002 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 15.15.15.15 --------------
1002 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 16.16.16.16 --------------
1002 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 5.5.5.5 --------------
1002 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1002 DF ---- ----
1003 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 15.15.15.15 --------------
1003 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 16.16.16.16 --------------
1003 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 5.5.5.5 --------------
1003 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1003 NON-DF ---- ----
1004 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 15.15.15.15 --------------
1004 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 16.16.16.16 --------------
1004 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 5.5.5.5 --------------
1004 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1004 DF ---- ----
1005 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 15.15.15.15 --------------
1005 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 16.16.16.16 --------------
1005 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 5.5.5.5 --------------
1005 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1005 NON-DF ---- ----
1006 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 15.15.15.15 --------------
1006 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 16.16.16.16 --------------
1006 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 5.5.5.5 --------------
1006 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1006 DF ---- ----
1007 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 15.15.15.15 --------------
1007 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 16.16.16.16 --------------
1007 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 5.5.5.5 --------------
1007 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1007 NON-DF ---- ----
1008 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 15.15.15.15 --------------
1008 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 16.16.16.16 --------------
1008 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 5.5.5.5 --------------
1008 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1008 DF ---- ----
1009 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 15.15.15.15 --------------
1009 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 16.16.16.16 --------------
1009 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 5.5.5.5 --------------
1009 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1009 NON-DF ---- ----
1010 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 15.15.15.15 --------------
1010 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 16.16.16.16 --------------
1010 ---- L2 NW ---- ---- ---- ---- ---- 4.4.4.4 5.5.5.5 --------------
1010 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1010 DF ---- ----
Total number of entries are 43
VTEP4#show nvo vxlan tunnel
VXLAN Network tunnel Entries
Source Destination Status Up/Down Update
========================================================================
4.4.4.4 15.15.15.15 Installed 00:21:39 00:21:39
4.4.4.4 16.16.16.16 Installed 00:21:52 00:21:52
4.4.4.4 5.5.5.5 Installed 00:21:50 00:21:50
Total number of entries are 3
VTEP4#show nvo vxlan access-if brief
Inner Admin Link
Interface Vlan vlan Ifindex Vnid status status
---------------------------------------------------------------
po200 1001 --- 0x7a120 1001 up up
po200 1002 --- 0x7a121 1002 up up
po200 1003 --- 0x7a122 1003 up up
po200 1004 --- 0x7a123 1004 up up
po200 1005 --- 0x7a124 1005 up up
po200 1006 --- 0x7a125 1006 up up
po200 1007 --- 0x7a126 1007 up up
po200 1008 --- 0x7a127 1008 up up
po200 1009 --- 0x7a128 1009 up up
po200 1010 --- 0x7a129 1010 up up
Total number of entries are 10
VTEP4#show etherchannel summary
Aggregator po200 100200
Aggregator Type: Layer2
Admin Key: 0200 - Oper Key 0200
Link: xe48 (5054) sync: 1
VTEP4#show ip route vrf L3_VRF1
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2,
ia - IS-IS inter area, E - EVPN,
v - vrf leaked, g - imported from global
* - candidate default
IP Route Table for VRF "L3_VRF1"
B 5.5.5.5/32 [0/0] is directly connected, tunvxlan2, installed 00:21:49, last update 00:21:49 ago
B 15.15.15.15/32 [0/0] is directly connected, tunvxlan2, installed 00:19:34, last update 00:19:34 ago
B 16.16.16.16/32 [0/0] is directly connected, tunvxlan2, installed 00:19:29, last update 00:19:29 ago
B 101.101.1.0/24 [20/0] via 16.16.16.16 (recursive is directly connected, tunvxlan2), installed 00:19:34, last update 00:19:20 ago
[20/0] via 15.15.15.15 (recursive is directly connected, tunvxlan2)
C 102.101.1.0/24 is directly connected, irb1003, installed 00:24:05, last update 00:24:05 ago
C 127.0.0.0/8 is directly connected, lo.L3_VRF1, installed 00:24:08, last update 00:24:08 ago
B 201.101.1.0/24 [20/0] via 16.16.16.16 (recursive is directly connected, tunvxlan2), installed 00:19:34, last update 00:19:20 ago
[20/0] via 15.15.15.15 (recursive is directly connected, tunvxlan2)
B 202.101.1.0/24 [200/0] via 5.5.5.5 (recursive is directly connected, tunvxlan2), installed 00:21:49, last update 00:21:49 ago
Gateway of last resort is not set
VTEP4#show ipv6 route vrf L3_VRF1
IPv6 Routing Table
Codes: K - kernel route, C - connected, S - static, D- DHCP, R - RIP,
O - OSPF, IA - OSPF inter area, E1 - OSPF external type 1,
E2 - OSPF external type 2, E - EVPN N1 - OSPF NSSA external type 1,
N2 - OSPF NSSA external type 2, i - IS-IS, B - BGP,
v - vrf leaked, g - imported from global
Timers: Uptime
IP Route Table for VRF "L3_VRF1"
C ::1/128 via ::, lo.L3_VRF1, installed 00:24:08, last update 00:24:08 ago
B ::ffff:505:505/128 [0/0] via ::, tunvxlan2, installed 00:21:49, last update 00:21:49 ago
B ::ffff:f0f:f0f/128 [0/0] via ::, tunvxlan2, installed 00:19:34, last update 00:19:34 ago
B ::ffff:1010:1010/128 [0/0] via ::, tunvxlan2, installed 00:19:29, last update 00:19:29 ago
B 101::/64 [20/0] via ::ffff:1010:1010 (recursive via ::, tunvxlan2), installed 00:19:34, last update 00:19:20 ago
[20/0] via ::ffff:f0f:f0f (recursive via ::, tunvxlan2)
C 102::/64 via ::, irb1003, installed 00:24:04, last update 00:24:04 ago
B 201::/64 [20/0] via ::ffff:1010:1010 (recursive via ::, tunvxlan2), installed 00:19:34, last update 00:19:20 ago
[20/0] via ::ffff:f0f:f0f (recursive via ::, tunvxlan2)
B 202::/64 [200/0] via ::ffff:505:505 (recursive via ::, tunvxlan2), installed 00:21:49, last update 00:21:49 ago
C fe80::/64 via ::, irb1003, installed 00:24:05, last update 00:24:05 ago
VTEP4#show bgp l2vpn evpn prefix-route
BGP table version is 45, local router ID is 4.4.4.4
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal,
l - labeled, S Stale w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Description : Ext-Color - Extended community color
RD[5.5.5.5:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*>i0 0 24 102.101.1.0 0.0.0.0 1000 5.5.5.5 5.5.5.5 VXLAN 5c17:83ff:2255
*>i0 0 24 202.101.1.0 0.0.0.0 1000 5.5.5.5 5.5.5.5 VXLAN 5c17:83ff:2255
*>i0 0 64 102:: :: 1000 5.5.5.5 5.5.5.5 VXLAN 5c17:83ff:2255
*>i0 0 64 202:: :: 1000 5.5.5.5 5.5.5.5 VXLAN 5c17:83ff:2255
RD[15.15.15.15:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 101.101.1.0 0.0.0.0 1000 15.15.15.15 15.15.15.15 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 24 101.101.1.0 0.0.0.0 1000 15.15.15.15 5.5.5.5 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
*> 0 0 24 201.101.1.0 0.0.0.0 1000 15.15.15.15 15.15.15.15 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 24 201.101.1.0 0.0.0.0 1000 15.15.15.15 5.5.5.5 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
*> 0 0 64 101:: :: 1000 15.15.15.15 15.15.15.15 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 64 101:: :: 1000 15.15.15.15 5.5.5.5 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
*> 0 0 64 201:: :: 1000 15.15.15.15 15.15.15.15 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 64 201:: :: 1000 15.15.15.15 5.5.5.5 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
RD[16.16.16.16:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 101.101.1.0 0.0.0.0 1000 16.16.16.16 16.16.16.16 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 24 101.101.1.0 0.0.0.0 1000 16.16.16.16 5.5.5.5 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
*> 0 0 24 201.101.1.0 0.0.0.0 1000 16.16.16.16 16.16.16.16 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 24 201.101.1.0 0.0.0.0 1000 16.16.16.16 5.5.5.5 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
*> 0 0 64 101:: :: 1000 16.16.16.16 16.16.16.16 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 64 101:: :: 1000 16.16.16.16 5.5.5.5 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
*> 0 0 64 201:: :: 1000 16.16.16.16 16.16.16.16 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 64 201:: :: 1000 16.16.16.16 5.5.5.5 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
VTEP4#
=============================================
VTEP5
=============================================
VTEP5#show ip ospf neighbor
Total number of full neighbors: 2
OSPF process 100 VRF(default):
Neighbor ID Pri State Dead Time Address Interface Instance ID
9.9.9.9 1 Full/DR 00:00:38 50.1.1.2 xe33 0
10.10.10.10 1 Full/DR 00:00:37 50.1.2.2 xe34 0
VTEP5#show bgp l2vpn evpn summary
BGP router identifier 5.5.5.5, local AS number 65003
BGP table version is 42
3 BGP AS-PATH entries
0 BGP community entries
Neighbor V AS MsgRcv MsgSen TblVer InQ OutQ Up/Down State/PfxRcd AD MACIP MCAST ESI PREFIX-ROUTE Desc
4.4.4.4 4 65003 265 276 42 0 0 00:21:52 600 49 510 30 1 10
15.15.15.15 4 65002 164 300 42 0 0 00:21:42 264 19 231 10 0 4
16.16.16.16 4 65002 176 303 42 0 0 00:21:52 264 19 231 10 0 4
Total number of neighbors 3
Total number of Established sessions 3
VTEP5#show nvo vxlan
VXLAN Information
=================
Codes: NW - Network Port
AC - Access Port
(u) - Untagged
VNID VNI-Name VNI-Type Type Intr-VNID Interface ESI VLAN DF-Status Src-Addr Dst-Addr Router-Mac
_______________________________________________________________________________________________________________________________________________________________
1000 ---- L3 NW ---- ---- ---- ---- ---- 5.5.5.5 15.15.15.15 342c.8e5d.b9cc
1000 ---- L3 NW ---- ---- ---- ---- ---- 5.5.5.5 16.16.16.16 4445.ba13.ba01
1000 ---- L3 NW ---- ---- ---- ---- ---- 5.5.5.5 4.4.4.4 7c8d.9caa.5231
1001 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 15.15.15.15 --------------
1001 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 16.16.16.16 --------------
1001 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 4.4.4.4 --------------
1001 ---- -- AC ---- cd3/1 --- Single Homed Port --- 1001 ---- ---- ----
1001 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1001 DF ---- ----
1002 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 15.15.15.15 --------------
1002 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 16.16.16.16 --------------
1002 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 4.4.4.4 --------------
1002 ---- -- AC ---- cd3/1 --- Single Homed Port --- 1002 ---- ---- ----
1002 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1002 NON-DF ---- ----
1003 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 15.15.15.15 --------------
1003 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 16.16.16.16 --------------
1003 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 4.4.4.4 --------------
1003 ---- -- AC ---- cd3/1 --- Single Homed Port --- 1003 ---- ---- ----
1003 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1003 DF ---- ----
1004 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 15.15.15.15 --------------
1004 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 16.16.16.16 --------------
1004 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 4.4.4.4 --------------
1004 ---- -- AC ---- cd3/1 --- Single Homed Port --- 1004 ---- ---- ----
1004 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1004 NON-DF ---- ----
1005 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 15.15.15.15 --------------
1005 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 16.16.16.16 --------------
1005 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 4.4.4.4 --------------
1005 ---- -- AC ---- cd3/1 --- Single Homed Port --- 1005 ---- ---- ----
1005 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1005 DF ---- ----
1006 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 15.15.15.15 --------------
1006 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 16.16.16.16 --------------
1006 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 4.4.4.4 --------------
1006 ---- -- AC ---- cd3/1 --- Single Homed Port --- 1006 ---- ---- ----
1006 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1006 NON-DF ---- ----
1007 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 15.15.15.15 --------------
1007 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 16.16.16.16 --------------
1007 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 4.4.4.4 --------------
1007 ---- -- AC ---- cd3/1 --- Single Homed Port --- 1007 ---- ---- ----
1007 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1007 DF ---- ----
1008 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 15.15.15.15 --------------
1008 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 16.16.16.16 --------------
1008 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 4.4.4.4 --------------
1008 ---- -- AC ---- cd3/1 --- Single Homed Port --- 1008 ---- ---- ----
1008 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1008 NON-DF ---- ----
1009 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 15.15.15.15 --------------
1009 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 16.16.16.16 --------------
1009 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 4.4.4.4 --------------
1009 ---- -- AC ---- cd3/1 --- Single Homed Port --- 1009 ---- ---- ----
1009 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1009 DF ---- ----
1010 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 15.15.15.15 --------------
1010 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 16.16.16.16 --------------
1010 ---- L2 NW ---- ---- ---- ---- ---- 5.5.5.5 4.4.4.4 --------------
1010 ---- -- AC ---- cd3/1 --- Single Homed Port --- 1010 ---- ---- ----
1010 ---- -- AC ---- po200 00:00:00:99:99:22:22:00:00:00 1010 NON-DF ---- ----
Total number of entries are 53
VTEP5#show nvo vxlan tunnel
VXLAN Network tunnel Entries
Source Destination Status Up/Down Update
========================================================================
5.5.5.5 15.15.15.15 Installed 00:21:41 00:21:41
5.5.5.5 16.16.16.16 Installed 00:21:51 00:21:51
5.5.5.5 4.4.4.4 Installed 00:21:51 00:21:51
Total number of entries are 3
VTEP5#show nvo vxlan access-if brief
Inner Admin Link
Interface Vlan vlan Ifindex Vnid status status
---------------------------------------------------------------
cd3/1 1001 --- 0x7a120 1001 up up
cd3/1 1002 --- 0x7a121 1002 up up
cd3/1 1003 --- 0x7a122 1003 up up
cd3/1 1004 --- 0x7a123 1004 up up
cd3/1 1005 --- 0x7a124 1005 up up
cd3/1 1006 --- 0x7a125 1006 up up
cd3/1 1007 --- 0x7a126 1007 up up
cd3/1 1008 --- 0x7a127 1008 up up
cd3/1 1009 --- 0x7a128 1009 up up
cd3/1 1010 --- 0x7a129 1010 up up
po200 1001 --- 0x7a12a 1001 up up
po200 1002 --- 0x7a12b 1002 up up
po200 1003 --- 0x7a12c 1003 up up
po200 1004 --- 0x7a12d 1004 up up
po200 1005 --- 0x7a12e 1005 up up
po200 1006 --- 0x7a12f 1006 up up
po200 1007 --- 0x7a130 1007 up up
po200 1008 --- 0x7a131 1008 up up
po200 1009 --- 0x7a132 1009 up up
po200 1010 --- 0x7a133 1010 up up
Total number of entries are 20
VTEP5#show etherchannel summary
Aggregator po200 100200
Aggregator Type: Layer2
Admin Key: 0200 - Oper Key 0200
Link: cd21/1 (5043) sync: 1
VTEP5#show ip route vrf L3_VRF1
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2,
ia - IS-IS inter area, E - EVPN,
v - vrf leaked, g - imported from global
* - candidate default
IP Route Table for VRF "L3_VRF1"
B 4.4.4.4/32 [0/0] is directly connected, tunvxlan2, installed 00:21:51, last update 00:21:51 ago
B 15.15.15.15/32 [0/0] is directly connected, tunvxlan2, installed 00:19:34, last update 00:19:34 ago
B 16.16.16.16/32 [0/0] is directly connected, tunvxlan2, installed 00:19:33, last update 00:19:33 ago
B 101.101.1.0/24 [20/0] via 16.16.16.16 (recursive is directly connected, tunvxlan2), installed 00:19:33, last update 00:19:24 ago
[20/0] via 15.15.15.15 (recursive is directly connected, tunvxlan2)
C 102.101.1.0/24 is directly connected, irb1003, installed 00:24:03, last update 00:24:03 ago
C 127.0.0.0/8 is directly connected, lo.L3_VRF1, installed 00:24:07, last update 00:24:07 ago
B 201.101.1.0/24 [20/0] via 16.16.16.16 (recursive is directly connected, tunvxlan2), installed 00:19:33, last update 00:19:24 ago
[20/0] via 15.15.15.15 (recursive is directly connected, tunvxlan2)
C 202.101.1.0/24 is directly connected, irb1004, installed 00:24:03, last update 00:24:03 ago
Gateway of last resort is not set
VTEP5#show ipv6 route vrf L3_VRF1
IPv6 Routing Table
Codes: K - kernel route, C - connected, S - static, D- DHCP, R - RIP,
O - OSPF, IA - OSPF inter area, E1 - OSPF external type 1,
E2 - OSPF external type 2, E - EVPN N1 - OSPF NSSA external type 1,
N2 - OSPF NSSA external type 2, i - IS-IS, B - BGP,
v - vrf leaked, g - imported from global
Timers: Uptime
IP Route Table for VRF "L3_VRF1"
C ::1/128 via ::, lo.L3_VRF1, installed 00:24:08, last update 00:24:08 ago
B ::ffff:404:404/128 [0/0] via ::, tunvxlan2, installed 00:21:52, last update 00:21:52 ago
B ::ffff:f0f:f0f/128 [0/0] via ::, tunvxlan2, installed 00:19:35, last update 00:19:35 ago
B ::ffff:1010:1010/128 [0/0] via ::, tunvxlan2, installed 00:19:34, last update 00:19:34 ago
B 101::/64 [20/0] via ::ffff:1010:1010 (recursive via ::, tunvxlan2), installed 00:19:34, last update 00:19:25 ago
[20/0] via ::ffff:f0f:f0f (recursive via ::, tunvxlan2)
C 102::/64 via ::, irb1003, installed 00:24:04, last update 00:24:04 ago
B 201::/64 [20/0] via ::ffff:1010:1010 (recursive via ::, tunvxlan2), installed 00:19:34, last update 00:19:25 ago
[20/0] via ::ffff:f0f:f0f (recursive via ::, tunvxlan2)
C 202::/64 via ::, irb1004, installed 00:24:04, last update 00:24:04 ago
C fe80::/64 via ::, irb1004, installed 00:24:04, last update 00:24:04 ago
VTEP5#show bgp l2vpn evpn prefix-route
BGP table version is 42, local router ID is 5.5.5.5
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal,
l - labeled, S Stale w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Description : Ext-Color - Extended community color
RD[4.4.4.4:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*>i0 0 24 102.101.1.0 0.0.0.0 1000 4.4.4.4 4.4.4.4 VXLAN 7c8d:9caa:5231
*>i0 0 64 102:: :: 1000 4.4.4.4 4.4.4.4 VXLAN 7c8d:9caa:5231
RD[15.15.15.15:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 101.101.1.0 0.0.0.0 1000 15.15.15.15 15.15.15.15 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 24 101.101.1.0 0.0.0.0 1000 15.15.15.15 4.4.4.4 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
*> 0 0 24 201.101.1.0 0.0.0.0 1000 15.15.15.15 15.15.15.15 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 24 201.101.1.0 0.0.0.0 1000 15.15.15.15 4.4.4.4 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
*> 0 0 64 101:: :: 1000 15.15.15.15 15.15.15.15 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 64 101:: :: 1000 15.15.15.15 4.4.4.4 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
*> 0 0 64 201:: :: 1000 15.15.15.15 15.15.15.15 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 64 201:: :: 1000 15.15.15.15 4.4.4.4 VXLAN 342c:8e5d:b9cc 2324:24:70(evpn), 2523:23:128(ipvpn)
RD[16.16.16.16:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 101.101.1.0 0.0.0.0 1000 16.16.16.16 16.16.16.16 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 24 101.101.1.0 0.0.0.0 1000 16.16.16.16 4.4.4.4 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
*> 0 0 24 201.101.1.0 0.0.0.0 1000 16.16.16.16 16.16.16.16 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 24 201.101.1.0 0.0.0.0 1000 16.16.16.16 4.4.4.4 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
*> 0 0 64 101:: :: 1000 16.16.16.16 16.16.16.16 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 64 101:: :: 1000 16.16.16.16 4.4.4.4 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
*> 0 0 64 201:: :: 1000 16.16.16.16 16.16.16.16 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
* i0 0 64 201:: :: 1000 16.16.16.16 4.4.4.4 VXLAN 4445:ba13:ba01 2324:24:70(evpn), 2523:23:128(ipvpn)
VTEP5#
=============================================
BLEAF1
=============================================
BLEAF1#show ip ospf neighbor
Total number of full neighbors: 4
OSPF process 100 VRF(default):
Neighbor ID Pri State Dead Time Address Interface Instance ID
11.11.11.11 1 Full/Backup 00:00:35 101.1.1.1 ce22 0
12.12.12.12 1 Full/Backup 00:00:29 102.1.1.1 ce21 0
17.17.17.17 1 Full/DR 00:00:32 103.1.1.2 xe2 0
18.18.18.18 1 Full/DR 00:00:31 103.1.2.2 ce12 0
BLEAF1#show bgp l2vpn evpn summary
BGP router identifier 13.13.13.13, local AS number 65002
BGP table version is 42
3 BGP AS-PATH entries
0 BGP community entries
Neighbor V AS MsgRcv MsgSen TblVer InQ OutQ Up/Down State/PfxRcd AD MACIP MCAST ESI PREFIX-ROUTE Desc
1.1.1.1 4 65001 252 170 42 0 0 00:20:39 208 22 160 20 0 6
2.2.2.2 4 65001 231 137 42 0 0 00:20:39 208 22 160 20 0 6
24.24.24.24 4 65002 121 184 42 0 0 00:18:54 38 19 0 10 9 0
25.25.25.25 4 65002 128 194 42 0 0 00:20:39 187 19 158 10 0 0
26.26.26.26 4 65002 128 168 42 0 0 00:20:39 187 19 158 10 0 0
Total number of neighbors 5
Total number of Established sessions 5
BLEAF1#show nvo vxlan
VXLAN Information
=================
Codes: NW - Network Port
AC - Access Port
(u) - Untagged
VNID VNI-Name VNI-Type Type Intr-VNID Interface ESI VLAN DF-Status Src-Addr Dst-Addr Router-Mac
_______________________________________________________________________________________________________________________________________________________________
1000 ---- L3 NW ---- ---- ---- ---- ---- 13.13.13.13 2.2.2.2 e001.a6a9.4b01
1000 ---- L3 NW ---- ---- ---- ---- ---- 13.13.13.13 1.1.1.1 1444.8f6c.47ec
1001 ---- L2 NW 100001 ---- ---- ---- ---- 13.13.13.13 2.2.2.2 --------------
1001 ---- L2 NW 100001 ---- ---- ---- ---- 13.13.13.13 1.1.1.1 --------------
1001 ---- -- AC 100001 ce4/4.1001 --- Single Homed Port --- ---- ---- ---- ----
1001 ---- -- DC 100001 iESI 00:00:11:11:11:11:11:11:11:11 1001 N/A(DC) ---- ----
1002 ---- L2 NW 100002 ---- ---- ---- ---- 13.13.13.13 2.2.2.2 --------------
1002 ---- L2 NW 100002 ---- ---- ---- ---- 13.13.13.13 1.1.1.1 --------------
1002 ---- -- AC 100002 ce4/4.1002 --- Single Homed Port --- ---- ---- ---- ----
1002 ---- -- DC 100002 iESI 00:00:11:22:11:11:11:11:11:11 1002 N/A(DC) ---- ----
1003 ---- L2 NW 100003 ---- ---- ---- ---- 13.13.13.13 2.2.2.2 --------------
1003 ---- L2 NW 100003 ---- ---- ---- ---- 13.13.13.13 1.1.1.1 --------------
1003 ---- -- AC 100003 ce4/4.1003 --- Single Homed Port --- ---- ---- ---- ----
1003 ---- -- DC 100003 iESI 00:00:11:33:11:11:11:11:11:11 1003 N/A(DC) ---- ----
1004 ---- L2 NW 100004 ---- ---- ---- ---- 13.13.13.13 2.2.2.2 --------------
1004 ---- L2 NW 100004 ---- ---- ---- ---- 13.13.13.13 1.1.1.1 --------------
1004 ---- -- AC 100004 ce4/4.1004 --- Single Homed Port --- ---- ---- ---- ----
1004 ---- -- DC 100004 iESI 00:00:11:44:11:11:11:11:11:11 1004 N/A(DC) ---- ----
1005 ---- L2 NW 100005 ---- ---- ---- ---- 13.13.13.13 2.2.2.2 --------------
1005 ---- L2 NW 100005 ---- ---- ---- ---- 13.13.13.13 1.1.1.1 --------------
1005 ---- -- AC 100005 ce4/4.1005 --- Single Homed Port --- ---- ---- ---- ----
1005 ---- -- DC 100005 iESI 00:00:11:55:11:11:11:11:11:11 1005 N/A(DC) ---- ----
1006 ---- L2 NW 100006 ---- ---- ---- ---- 13.13.13.13 2.2.2.2 --------------
1006 ---- L2 NW 100006 ---- ---- ---- ---- 13.13.13.13 1.1.1.1 --------------
1006 ---- -- AC 100006 ce4/4.1006 --- Single Homed Port --- ---- ---- ---- ----
1006 ---- -- DC 100006 iESI 00:00:11:66:11:11:11:11:11:11 1006 N/A(DC) ---- ----
1007 ---- L2 NW 100007 ---- ---- ---- ---- 13.13.13.13 2.2.2.2 --------------
1007 ---- L2 NW 100007 ---- ---- ---- ---- 13.13.13.13 1.1.1.1 --------------
1007 ---- -- AC 100007 ce4/4.1007 --- Single Homed Port --- ---- ---- ---- ----
1007 ---- -- DC 100007 iESI 00:00:11:77:11:11:11:11:11:11 1007 N/A(DC) ---- ----
1008 ---- L2 NW 100008 ---- ---- ---- ---- 13.13.13.13 2.2.2.2 --------------
1008 ---- L2 NW 100008 ---- ---- ---- ---- 13.13.13.13 1.1.1.1 --------------
1008 ---- -- AC 100008 ce4/4.1008 --- Single Homed Port --- ---- ---- ---- ----
1008 ---- -- DC 100008 iESI 00:00:11:88:11:11:11:11:11:11 1008 N/A(DC) ---- ----
1009 ---- L2 NW 100009 ---- ---- ---- ---- 13.13.13.13 2.2.2.2 --------------
1009 ---- L2 NW 100009 ---- ---- ---- ---- 13.13.13.13 1.1.1.1 --------------
1009 ---- -- AC 100009 ce4/4.1009 --- Single Homed Port --- ---- ---- ---- ----
1009 ---- -- DC 100009 iESI 00:00:11:99:11:11:11:11:11:11 1009 N/A(DC) ---- ----
1010 ---- L2 NW 100010 ---- ---- ---- ---- 13.13.13.13 2.2.2.2 --------------
1010 ---- L2 NW 100010 ---- ---- ---- ---- 13.13.13.13 1.1.1.1 --------------
1010 ---- -- AC 100010 ce4/4.1010 --- Single Homed Port --- ---- ---- ---- ----
1010 ---- -- DC 100010 iESI 00:00:11:99:11:11:11:11:11:11 1010 N/A(DC) ---- ----
Total number of entries are 42
Note: Refer sub-interface config for VLAN information.
BLEAF1#show nvo vxlan tunnel
VXLAN Network tunnel Entries
Source Destination Status Up/Down Update
========================================================================
13.13.13.13 2.2.2.2 Installed 00:20:41 00:20:41
13.13.13.13 1.1.1.1 Installed 00:20:41 00:20:41
Total number of entries are 2
BLEAF1#show nvo vxlan access-if brief
Inner Admin Link
Interface Vlan vlan Ifindex Vnid status status
---------------------------------------------------------------
ce4/4.1001 --- --- 0x139203e9 1001 up up
ce4/4.1002 --- --- 0x139203ea 1002 up up
ce4/4.1003 --- --- 0x139203eb 1003 up up
ce4/4.1004 --- --- 0x139203ec 1004 up up
ce4/4.1005 --- --- 0x139203ed 1005 up up
ce4/4.1006 --- --- 0x139203ee 1006 up up
ce4/4.1007 --- --- 0x139203ef 1007 up up
ce4/4.1008 --- --- 0x139203f0 1008 up up
ce4/4.1009 --- --- 0x139203f1 1009 up up
ce4/4.1010 --- --- 0x139203f2 1010 up up
Total number of entries are 10
Note: Refer sub-interface config for VLAN information.
BLEAF1#show etherchannel summary
BLEAF1#show ip route vrf L3_VRF1
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2,
ia - IS-IS inter area, E - EVPN,
v - vrf leaked, g - imported from global
* - candidate default
IP Route Table for VRF "L3_VRF1"
B 1.1.1.1/32 [0/0] is directly connected, tunvxlan2, installed 00:20:46, last update 00:20:46 ago
B 2.2.2.2/32 [0/0] is directly connected, tunvxlan2, installed 00:20:46, last update 00:20:46 ago
B 101.101.1.0/24 [20/0] via 1.1.1.1 (recursive is directly connected, tunvxlan2), installed 00:20:46, last update 00:20:46 ago
C 127.0.0.0/8 is directly connected, lo.L3_VRF1, installed 00:21:52, last update 00:21:52 ago
B 201.101.1.0/24 [20/0] via 2.2.2.2 (recursive is directly connected, tunvxlan2), installed 00:20:46, last update 00:20:46 ago
Gateway of last resort is not set
BLEAF1#show ipv6 route vrf L3_VRF1
IPv6 Routing Table
Codes: K - kernel route, C - connected, S - static, D- DHCP, R - RIP,
O - OSPF, IA - OSPF inter area, E1 - OSPF external type 1,
E2 - OSPF external type 2, E - EVPN N1 - OSPF NSSA external type 1,
N2 - OSPF NSSA external type 2, i - IS-IS, B - BGP,
P - SRV6-POLICY,
v - vrf leaked, g - imported from global
Timers: Uptime
IP Route Table for VRF "L3_VRF1"
C ::1/128 via ::, lo.L3_VRF1, installed 00:21:54, last update 00:21:54 ago
B ::ffff:101:101/128 [0/0] via ::, tunvxlan2, installed 00:20:48, last update 00:20:48 ago
B ::ffff:202:202/128 [0/0] via ::, tunvxlan2, installed 00:20:48, last update 00:20:48 ago
B 101::/64 [20/0] via ::ffff:101:101 (recursive via ::, tunvxlan2), installed 00:20:48, last update 00:20:48 ago
B 201::/64 [20/0] via ::ffff:202:202 (recursive via ::, tunvxlan2), installed 00:20:48, last update 00:20:48 ago
C fe80::/64 via ::, tunvxlan2, installed 00:21:54, last update 00:21:54 ago
BLEAF1#show ip route vrf L3_VRF1 database
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2,
ia - IS-IS inter area, E - EVPN,
v - vrf leaked, g - imported from global
> - selected route, * - FIB route, p - stale info
IP Route Table for VRF "L3_VRF1"
B *> 1.1.1.1/32 [0/0] is directly connected, tunvxlan2, installed 00:20:56, last update 00:20:56 ago
B *> 2.2.2.2/32 [0/0] is directly connected, tunvxlan2, installed 00:20:56, last update 00:20:56 ago
B *> 101.101.1.0/24 [20/0] via 1.1.1.1 (recursive is directly connected, tunvxlan2), installed 00:20:56, last update 00:20:56 ago
B > 102.101.1.0/24 [200/0] via 26.26.26.26, installed 00:20:55, last update 00:20:54 ago
> [200/0] via 25.25.25.25
C *> 127.0.0.0/8 is directly connected, lo.L3_VRF1, installed 00:22:02, last update 00:22:02 ago
B *> 201.101.1.0/24 [20/0] via 2.2.2.2 (recursive is directly connected, tunvxlan2), installed 00:20:56, last update 00:20:56 ago
B > 202.101.1.0/24 [200/0] via 26.26.26.26, installed 00:20:55, last update 00:20:54 ago
> [200/0] via 25.25.25.25
Total number of IPv4 routes 9
Gateway of last resort is not set
BLEAF1#show ipv6 route vrf L3_VRF1 database
IPv6 Routing Table
Codes: K - kernel route, C - connected, S - static, D- DHCP, R - RIP,
O - OSPF, IA - OSPF inter area, E1 - OSPF external type 1,
E2 - OSPF external type 2, E - EVPN N1 - OSPF NSSA external type 1,
N2 - OSPF NSSA external type 2, i - IS-IS, B - BGP,
P - SRV6-POLICY,
v - vrf leaked, g - imported from global
> - selected route, * - FIB route,p - stale info
Timers: Uptime
IP Route Table for VRF "L3_VRF1"
C *> ::1/128 via ::, lo.L3_VRF1, installed 00:22:07, last update 00:22:07 ago
B *> ::ffff:101:101/128 [0/0] via ::, tunvxlan2, installed 00:21:01, last update 00:21:01 ago
B *> ::ffff:202:202/128 [0/0] via ::, tunvxlan2, installed 00:21:01, last update 00:21:01 ago
B *> 101::/64 [20/0] via ::ffff:101:101 (recursive via ::, tunvxlan2), installed 00:21:01, last update 00:21:01 ago
B > 102::/64 [200/0] via ::ffff:26.26.26.26, installed 00:21:00, last update 00:21:00 ago
> [200/0] via ::ffff:25.25.25.25
B *> 201::/64 [20/0] via ::ffff:202:202 (recursive via ::, tunvxlan2), installed 00:21:01, last update 00:21:01 ago
B > 202::/64 [200/0] via ::ffff:26.26.26.26, installed 00:21:00, last update 00:21:00 ago
> [200/0] via ::ffff:25.25.25.25
C *> fe80::/64 via ::, tunvxlan2, installed 00:22:07, last update 00:22:07 ago
Total number of IPv6 routes 10
BLEAF1#show ip bgp vpnv4 all
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal, l - labeled
S Stale, x-EVPN, w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path Ext-Color
Route Distinguisher: 13.13.13.13:101 (Default for VRF L3_VRF1)
*>x l 101.101.1.0/24 1.1.1.1 0 100 0 65001 ? -
* x 2.2.2.2 0 100 0 65001 ? -
*>iw 102.101.1.0/24 25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
* iw 26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
*>x l 201.101.1.0/24 2.2.2.2 0 100 0 65001 ? -
*>iw 202.101.1.0/24 25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
* iw 26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 7
Route Distinguisher: 15.15.15.15:951
*>iw 102.101.1.0/24 25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
*>iw 202.101.1.0/24 25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
Route Distinguisher: 16.16.16.16:951
*>iw 102.101.1.0/24 26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
*>iw 202.101.1.0/24 26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
BLEAF1#show ip bgp vpnv6 all
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal, l - labeled
S Stale, x-EVPN, w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path Ext-Color
Route Distinguisher: 13.13.13.13:101 (Default for VRF L3_VRF1)
*>x l 101::/64 ::ffff:1.1.1.1 0 100 0 65001 ? -
* x ::ffff:2.2.2.2 0 100 0 65001 ? -
*>iw 102::/64 ::ffff:25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
*aiw ::ffff:26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
*>x l 201::/64 ::ffff:2.2.2.2 0 100 0 65001 ? -
*>iw 202::/64 ::ffff:25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
*aiw ::ffff:26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 7
Route Distinguisher: 15.15.15.15:951
*>iw 102::/64 ::ffff:25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
*>iw 202::/64 ::ffff:25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
Route Distinguisher: 16.16.16.16:951
*>iw 102::/64 ::ffff:26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
*>iw 202::/64 ::ffff:26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
BLEAF1#show evpn mpls
EVPN-MPLS Information
=================
Codes: NW - Network Port
AC - Access Port
CW - Control Word
(u) - Untagged
VPN-ID EVI-Name CW EVI-Type Type Intr-VNID Interface ESI VLAN DF-Status Src-Addr Dst-Addr
___________________________________________________________________________________________________________________________________________
100001 ---- --- L2 NW 1001 ---- ---- ---- ---- 23.23.23.23 26.26.26.26
100001 ---- --- L2 NW 1001 ---- ---- ---- ---- 23.23.23.23 24.24.24.24
100001 ---- --- L2 NW 1001 ---- ---- ---- ---- 23.23.23.23 25.25.25.25
100001 ---- No -- WAN 1001 iESI 00:00:11:11:11:11:11:11:11:11 100001 NDF ---- ----
100002 ---- --- L2 NW 1002 ---- ---- ---- ---- 23.23.23.23 26.26.26.26
100002 ---- --- L2 NW 1002 ---- ---- ---- ---- 23.23.23.23 24.24.24.24
100002 ---- --- L2 NW 1002 ---- ---- ---- ---- 23.23.23.23 25.25.25.25
100002 ---- No -- WAN 1002 iESI 00:00:11:22:11:11:11:11:11:11 100002 DF ---- ----
100003 ---- --- L2 NW 1003 ---- ---- ---- ---- 23.23.23.23 26.26.26.26
100003 ---- --- L2 NW 1003 ---- ---- ---- ---- 23.23.23.23 24.24.24.24
100003 ---- --- L2 NW 1003 ---- ---- ---- ---- 23.23.23.23 25.25.25.25
100003 ---- No -- WAN 1003 iESI 00:00:11:33:11:11:11:11:11:11 100003 NDF ---- ----
100004 ---- --- L2 NW 1004 ---- ---- ---- ---- 23.23.23.23 26.26.26.26
100004 ---- --- L2 NW 1004 ---- ---- ---- ---- 23.23.23.23 24.24.24.24
100004 ---- --- L2 NW 1004 ---- ---- ---- ---- 23.23.23.23 25.25.25.25
100004 ---- No -- WAN 1004 iESI 00:00:11:44:11:11:11:11:11:11 100004 DF ---- ----
100005 ---- --- L2 NW 1005 ---- ---- ---- ---- 23.23.23.23 26.26.26.26
100005 ---- --- L2 NW 1005 ---- ---- ---- ---- 23.23.23.23 24.24.24.24
100005 ---- --- L2 NW 1005 ---- ---- ---- ---- 23.23.23.23 25.25.25.25
100005 ---- Yes -- WAN 1005 iESI 00:00:11:55:11:11:11:11:11:11 100005 NDF ---- ----
100006 ---- --- L2 NW 1006 ---- ---- ---- ---- 23.23.23.23 26.26.26.26
100006 ---- --- L2 NW 1006 ---- ---- ---- ---- 23.23.23.23 24.24.24.24
100006 ---- --- L2 NW 1006 ---- ---- ---- ---- 23.23.23.23 25.25.25.25
100006 ---- No -- WAN 1006 iESI 00:00:11:66:11:11:11:11:11:11 100006 DF ---- ----
100007 ---- --- L2 NW 1007 ---- ---- ---- ---- 23.23.23.23 26.26.26.26
100007 ---- --- L2 NW 1007 ---- ---- ---- ---- 23.23.23.23 24.24.24.24
100007 ---- --- L2 NW 1007 ---- ---- ---- ---- 23.23.23.23 25.25.25.25
100007 ---- No -- WAN 1007 iESI 00:00:11:77:11:11:11:11:11:11 100007 NDF ---- ----
100008 ---- --- L2 NW 1008 ---- ---- ---- ---- 23.23.23.23 26.26.26.26
100008 ---- --- L2 NW 1008 ---- ---- ---- ---- 23.23.23.23 24.24.24.24
100008 ---- --- L2 NW 1008 ---- ---- ---- ---- 23.23.23.23 25.25.25.25
100008 ---- Yes -- WAN 1008 iESI 00:00:11:88:11:11:11:11:11:11 100008 DF ---- ----
100009 ---- --- L2 NW 1009 ---- ---- ---- ---- 23.23.23.23 26.26.26.26
100009 ---- --- L2 NW 1009 ---- ---- ---- ---- 23.23.23.23 24.24.24.24
100009 ---- --- L2 NW 1009 ---- ---- ---- ---- 23.23.23.23 25.25.25.25
100009 ---- No -- WAN 1009 iESI 00:00:11:99:11:11:11:11:11:11 100009 NDF ---- ----
100010 ---- --- L2 NW 1010 ---- ---- ---- ---- 23.23.23.23 26.26.26.26
100010 ---- --- L2 NW 1010 ---- ---- ---- ---- 23.23.23.23 24.24.24.24
100010 ---- --- L2 NW 1010 ---- ---- ---- ---- 23.23.23.23 25.25.25.25
100010 ---- No -- WAN 1010 iESI 00:00:11:99:11:11:11:11:11:11 100010 DF ---- ----
Total number of entries are 40
Note: Refer sub-interface config for VLAN information.
BLEAF1#show evpn mpls tunnel
EVPN-MPLS Network tunnel Entries
Source Destination Status Up/Down Update evpn-id Local-Leaf Remote-Leaf Ext-Color FAT CW
========================================================================================================================================
23.23.23.23 26.26.26.26 Installed 00:21:17 00:20:58 100010 --- --- --- --- No
23.23.23.23 26.26.26.26 Installed 00:21:17 00:20:58 100009 --- --- --- --- No
23.23.23.23 26.26.26.26 Installed 00:21:17 00:20:58 100008 --- --- --- set Yes
23.23.23.23 26.26.26.26 Installed 00:21:17 00:20:58 100007 --- --- --- set No
23.23.23.23 26.26.26.26 Installed 00:21:17 00:20:58 100006 --- --- --- --- No
23.23.23.23 26.26.26.26 Installed 00:21:17 00:20:58 100005 --- --- --- --- Yes
23.23.23.23 26.26.26.26 Installed 00:21:17 00:20:58 100004 --- --- --- --- No
23.23.23.23 26.26.26.26 Installed 00:21:17 00:20:58 100003 --- --- --- --- No
23.23.23.23 26.26.26.26 Installed 00:21:17 00:20:58 100002 --- --- --- --- No
23.23.23.23 26.26.26.26 Installed 00:21:17 00:20:58 100001 --- --- --- --- No
23.23.23.23 24.24.24.24 Installed 00:19:33 00:19:33 100010 --- --- --- --- No
23.23.23.23 24.24.24.24 Installed 00:19:33 00:19:33 100009 --- --- --- --- No
23.23.23.23 24.24.24.24 Installed 00:19:33 00:19:33 100008 --- --- --- set Yes
23.23.23.23 24.24.24.24 Installed 00:19:33 00:19:33 100007 --- --- --- set No
23.23.23.23 24.24.24.24 Installed 00:19:33 00:19:33 100006 --- --- --- --- No
23.23.23.23 24.24.24.24 Installed 00:19:33 00:19:33 100005 --- --- --- --- Yes
23.23.23.23 24.24.24.24 Installed 00:19:33 00:19:33 100004 --- --- --- --- No
23.23.23.23 24.24.24.24 Installed 00:19:33 00:19:33 100003 --- --- --- --- No
23.23.23.23 24.24.24.24 Installed 00:19:33 00:19:33 100002 --- --- --- --- No
23.23.23.23 24.24.24.24 Installed 00:19:33 00:19:33 100001 --- --- --- --- No
23.23.23.23 25.25.25.25 Installed 00:21:16 00:20:58 100010 --- --- --- --- No
23.23.23.23 25.25.25.25 Installed 00:21:16 00:20:58 100009 --- --- --- --- No
23.23.23.23 25.25.25.25 Installed 00:21:16 00:20:58 100008 --- --- --- set Yes
23.23.23.23 25.25.25.25 Installed 00:21:16 00:20:58 100007 --- --- --- set No
23.23.23.23 25.25.25.25 Installed 00:21:16 00:20:58 100006 --- --- --- --- No
23.23.23.23 25.25.25.25 Installed 00:21:16 00:20:58 100005 --- --- --- --- Yes
23.23.23.23 25.25.25.25 Installed 00:21:16 00:20:58 100004 --- --- --- --- No
23.23.23.23 25.25.25.25 Installed 00:21:16 00:20:58 100003 --- --- --- --- No
23.23.23.23 25.25.25.25 Installed 00:21:16 00:20:58 100002 --- --- --- --- No
23.23.23.23 25.25.25.25 Installed 00:21:16 00:20:58 100001 --- --- --- --- No
Total number of entries are 30
BLEAF1#show evpn mpls access-if brief
Inner Admin Link
Interface Vlan vlan Ifindex Vnid status status
---------------------------------------------------------------
Total number of entries are 0
Note: Refer sub-interface config for VLAN information.
BLEAF1#show ldp session
Codes: m - MD5 password is not set/unset.
g - GR configuration not set/unset.
t - TCP MSS not set/unset.
Session has to be cleared manually
Code Peer IP Address IF Name My Role State KeepAlive UpTime AutoCreate
14.14.14.14 ce21 Passive OPERATIONAL 30 00:19:37 No
18.18.18.18 ce12 Passive OPERATIONAL 30 00:21:27 No
17.17.17.17 xe2 Passive OPERATIONAL 30 00:21:08 No
BLEAF1#show mpls forwarding-table
Codes: > - installed FTN, * - selected FTN, p - stale FTN, ! - using backup
B - BGP FTN, K - CLI FTN, (t) - tunnel, P - SR Policy FTN, (b) - bypass,
L - LDP FTN, R - RSVP-TE FTN, S - SNMP FTN, I - IGP-Shortcut,
U - unknown FTN, O - SR-OSPF FTN, i - SR-ISIS FTN, k - SR-CLI FTN
(m) - FTN mapped over multipath transport, (e) - FTN is ECMP
FTN-ECMP LDP: Disabled, SR: Disabled
Code FEC FTN-ID Nhlfe-ID Tunnel-ID Pri Out-Label Out-Intf ELC Nexthop Algo-Num UpTime
L> 17.17.17.17/32 9 20 - - - - - - N/A 00:21:16
19 - Yes 3 xe2 No 103.1.1.2 - -
L> 18.18.18.18/32 2 4 - - - - - - N/A 00:21:37
3 - Yes 3 ce12 No 103.1.2.2 - -
L> 24.24.24.24/32 20 38 - - - - - - N/A 00:19:53
36 - Yes 24356 ce12 No 103.1.2.2 - -
37 - Yes 24356 xe2 No 103.1.1.2 - -
L> 25.25.25.25/32 3 6 - - - - - - N/A 00:21:37
5 - Yes 24337 ce12 No 103.1.2.2 - -
22 - Yes 24337 xe2 No 103.1.1.2 - -
L> 26.26.26.26/32 4 8 - - - - - - N/A 00:21:37
7 - Yes 24322 ce12 No 103.1.2.2 - -
23 - Yes 24322 xe2 No 103.1.1.2 - -
L> 104.1.1.0/24 19 34 - - - - - - N/A 00:20:39
33 - Yes 24355 xe2 No 103.1.1.2 - -
L> 104.1.2.0/24 18 31 - - - - - - N/A 00:20:39
30 - Yes 24355 ce12 No 103.1.2.2 - -
L> 105.1.1.0/24 10 20 - - - - - - N/A 00:21:16
19 - Yes 3 xe2 No 103.1.1.2 - -
L> 105.1.2.0/24 6 4 - - - - - - N/A 00:21:37
3 - Yes 3 ce12 No 103.1.2.2 - -
L> 106.1.1.0/24 11 20 - - - - - - N/A 00:21:16
19 - Yes 3 xe2 No 103.1.1.2 - -
L> 106.1.2.0/24 8 4 - - - - - - N/A 00:21:37
3 - Yes 3 ce12 No 103.1.2.2 - -
BLEAF1#
BLEAF1#show bgp l2vpn evpn prefix-route
BGP table version is 42, local router ID is 13.13.13.13
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal,
l - labeled, S Stale w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Description : Ext-Color - Extended community color
RD[1.1.1.1:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 101.101.1.0 0.0.0.0 1000 1.1.1.1 2.2.2.2 VXLAN 1444:8f6c:47ec
* 0 0 24 101.101.1.0 0.0.0.0 1000 1.1.1.1 1.1.1.1 VXLAN 1444:8f6c:47ec
*> 0 0 64 101:: :: 1000 1.1.1.1 2.2.2.2 VXLAN 1444:8f6c:47ec
* 0 0 64 101:: :: 1000 1.1.1.1 1.1.1.1 VXLAN 1444:8f6c:47ec
RD[2.2.2.2:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 101.101.1.0 0.0.0.0 1000 2.2.2.2 2.2.2.2 VXLAN e001:a6a9:4b01
* 0 0 24 101.101.1.0 0.0.0.0 1000 2.2.2.2 1.1.1.1 VXLAN e001:a6a9:4b01
*> 0 0 24 201.101.1.0 0.0.0.0 1000 2.2.2.2 2.2.2.2 VXLAN e001:a6a9:4b01
* 0 0 24 201.101.1.0 0.0.0.0 1000 2.2.2.2 1.1.1.1 VXLAN e001:a6a9:4b01
*> 0 0 64 101:: :: 1000 2.2.2.2 2.2.2.2 VXLAN e001:a6a9:4b01
* 0 0 64 101:: :: 1000 2.2.2.2 1.1.1.1 VXLAN e001:a6a9:4b01
*> 0 0 64 201:: :: 1000 2.2.2.2 2.2.2.2 VXLAN e001:a6a9:4b01
* 0 0 64 201:: :: 1000 2.2.2.2 1.1.1.1 VXLAN e001:a6a9:4b01
BLEAF1#
BLEAF1#show evpn multi-homing domain-tracking-status
iESI Domain Tracking Status
===========================
iESI-configured VRFs : 10
Configured peer-GW VTEPs (BGP-pushed) : 14.14.14.14(DC,no tunnel),24.24.24.24(WAN,tunnel exists)
Resolved-transit tunnels (peer GW excluded):
DC : 2 => DC ACTIVE
WAN : 20 => WAN ACTIVE
Per-VRF iESI object state:
VRF Domain ESI Isolated Withdrawn Tenants Peer GW(s)
--------------------------------------------------------------------------------------------------------
L2_VRF1 DC 00:00:11:11:11:11:11:11:11:11 no no 1 -
L2_VRF1 WAN 00:00:11:11:11:11:11:11:11:11 no no 1 24.24.24.24
L2_VRF10 DC 00:00:11:99:11:11:11:11:11:11 no no 2 -
L2_VRF10 WAN 00:00:11:99:11:11:11:11:11:11 no no 2 24.24.24.24
L2_VRF2 DC 00:00:11:22:11:11:11:11:11:11 no no 1 -
L2_VRF2 WAN 00:00:11:22:11:11:11:11:11:11 no no 1 24.24.24.24
L2_VRF3 DC 00:00:11:33:11:11:11:11:11:11 no no 1 -
L2_VRF3 WAN 00:00:11:33:11:11:11:11:11:11 no no 1 24.24.24.24
L2_VRF4 DC 00:00:11:44:11:11:11:11:11:11 no no 1 -
L2_VRF4 WAN 00:00:11:44:11:11:11:11:11:11 no no 1 24.24.24.24
L2_VRF5 DC 00:00:11:55:11:11:11:11:11:11 no no 1 -
L2_VRF5 WAN 00:00:11:55:11:11:11:11:11:11 no no 1 24.24.24.24
L2_VRF6 DC 00:00:11:66:11:11:11:11:11:11 no no 1 -
L2_VRF6 WAN 00:00:11:66:11:11:11:11:11:11 no no 1 24.24.24.24
L2_VRF7 DC 00:00:11:77:11:11:11:11:11:11 no no 1 -
L2_VRF7 WAN 00:00:11:77:11:11:11:11:11:11 no no 1 24.24.24.24
L2_VRF8 DC 00:00:11:88:11:11:11:11:11:11 no no 1 -
L2_VRF8 WAN 00:00:11:88:11:11:11:11:11:11 no no 1 24.24.24.24
L2_VRF9 DC 00:00:11:99:11:11:11:11:11:11 no no 2 -
L2_VRF9 WAN 00:00:11:99:11:11:11:11:11:11 no no 2 24.24.24.24
BLEAF1#
=============================================
BLEAF2
=============================================
BLEAF2#show ip ospf neighbor
Total number of full neighbors: 4
OSPF process 100 VRF(default):
Neighbor ID Pri State Dead Time Address Interface Instance ID
11.11.11.11 1 Full/Backup 00:00:38 101.1.2.1 ce1 0
12.12.12.12 1 Full/Backup 00:00:36 102.1.2.1 ce4 0
17.17.17.17 1 Full/DR 00:00:31 104.1.1.2 xe48 0
18.18.18.18 1 Full/DR 00:00:37 104.1.2.2 xe47 0
BLEAF2#show bgp l2vpn evpn summary
BGP router identifier 14.14.14.14, local AS number 65002
BGP table version is 35
3 BGP AS-PATH entries
0 BGP community entries
Neighbor V AS MsgRcv MsgSen TblVer InQ OutQ Up/Down State/PfxRcd AD MACIP MCAST ESI PREFIX-ROUTE Desc
1.1.1.1 4 65001 297 137 35 0 0 00:20:13 208 22 160 20 0 6
2.2.2.2 4 65001 217 136 35 0 0 00:20:12 208 22 160 20 0 6
23.23.23.23 4 65002 188 125 35 0 0 00:20:15 111 19 73 10 9 0
25.25.25.25 4 65002 148 125 35 0 0 00:20:14 187 19 158 10 0 0
26.26.26.26 4 65002 149 125 35 0 0 00:20:14 187 19 158 10 0 0
Total number of neighbors 5
Total number of Established sessions 5
BLEAF2#show nvo vxlan
VXLAN Information
=================
Codes: NW - Network Port
AC - Access Port
(u) - Untagged
VNID VNI-Name VNI-Type Type Intr-VNID Interface ESI VLAN DF-Status Src-Addr Dst-Addr Router-Mac
_______________________________________________________________________________________________________________________________________________________________
1000 ---- L3 NW ---- ---- ---- ---- ---- 14.14.14.14 2.2.2.2 e001.a6a9.4b01
1000 ---- L3 NW ---- ---- ---- ---- ---- 14.14.14.14 1.1.1.1 1444.8f6c.47ec
1001 ---- L2 NW 100001 ---- ---- ---- ---- 14.14.14.14 2.2.2.2 --------------
1001 ---- L2 NW 100001 ---- ---- ---- ---- 14.14.14.14 1.1.1.1 --------------
1001 ---- -- DC 100001 iESI 00:00:11:11:11:11:11:11:11:11 1001 N/A(DC) ---- ----
1002 ---- L2 NW 100002 ---- ---- ---- ---- 14.14.14.14 2.2.2.2 --------------
1002 ---- L2 NW 100002 ---- ---- ---- ---- 14.14.14.14 1.1.1.1 --------------
1002 ---- -- DC 100002 iESI 00:00:11:22:11:11:11:11:11:11 1002 N/A(DC) ---- ----
1003 ---- L2 NW 100003 ---- ---- ---- ---- 14.14.14.14 2.2.2.2 --------------
1003 ---- L2 NW 100003 ---- ---- ---- ---- 14.14.14.14 1.1.1.1 --------------
1003 ---- -- DC 100003 iESI 00:00:11:33:11:11:11:11:11:11 1003 N/A(DC) ---- ----
1004 ---- L2 NW 100004 ---- ---- ---- ---- 14.14.14.14 2.2.2.2 --------------
1004 ---- L2 NW 100004 ---- ---- ---- ---- 14.14.14.14 1.1.1.1 --------------
1004 ---- -- DC 100004 iESI 00:00:11:44:11:11:11:11:11:11 1004 N/A(DC) ---- ----
1005 ---- L2 NW 100005 ---- ---- ---- ---- 14.14.14.14 2.2.2.2 --------------
1005 ---- L2 NW 100005 ---- ---- ---- ---- 14.14.14.14 1.1.1.1 --------------
1005 ---- -- DC 100005 iESI 00:00:11:55:11:11:11:11:11:11 1005 N/A(DC) ---- ----
1006 ---- L2 NW 100006 ---- ---- ---- ---- 14.14.14.14 2.2.2.2 --------------
1006 ---- L2 NW 100006 ---- ---- ---- ---- 14.14.14.14 1.1.1.1 --------------
1006 ---- -- DC 100006 iESI 00:00:11:66:11:11:11:11:11:11 1006 N/A(DC) ---- ----
1007 ---- L2 NW 100007 ---- ---- ---- ---- 14.14.14.14 2.2.2.2 --------------
1007 ---- L2 NW 100007 ---- ---- ---- ---- 14.14.14.14 1.1.1.1 --------------
1007 ---- -- DC 100007 iESI 00:00:11:77:11:11:11:11:11:11 1007 N/A(DC) ---- ----
1008 ---- L2 NW 100008 ---- ---- ---- ---- 14.14.14.14 2.2.2.2 --------------
1008 ---- L2 NW 100008 ---- ---- ---- ---- 14.14.14.14 1.1.1.1 --------------
1008 ---- -- DC 100008 iESI 00:00:11:88:11:11:11:11:11:11 1008 N/A(DC) ---- ----
1009 ---- L2 NW 100009 ---- ---- ---- ---- 14.14.14.14 2.2.2.2 --------------
1009 ---- L2 NW 100009 ---- ---- ---- ---- 14.14.14.14 1.1.1.1 --------------
1009 ---- -- DC 100009 iESI 00:00:11:99:11:11:11:11:11:11 1009 N/A(DC) ---- ----
1010 ---- L2 NW 100010 ---- ---- ---- ---- 14.14.14.14 2.2.2.2 --------------
1010 ---- L2 NW 100010 ---- ---- ---- ---- 14.14.14.14 1.1.1.1 --------------
1010 ---- -- DC 100010 iESI 00:00:11:99:11:11:11:11:11:11 1010 N/A(DC) ---- ----
Total number of entries are 32
Note: Refer sub-interface config for VLAN information.
BLEAF2#show nvo vxlan tunnel
VXLAN Network tunnel Entries
Source Destination Status Up/Down Update
========================================================================
14.14.14.14 2.2.2.2 Installed 00:20:12 00:20:12
14.14.14.14 1.1.1.1 Installed 00:20:12 00:20:12
Total number of entries are 2
BLEAF2#show nvo vxlan access-if brief
Inner Admin Link
Interface Vlan vlan Ifindex Vnid status status
---------------------------------------------------------------
Total number of entries are 0
Note: Refer sub-interface config for VLAN information.
BLEAF2#show etherchannel summary
BLEAF2#show ip route vrf L3_VRF1
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2,
ia - IS-IS inter area, E - EVPN,
v - vrf leaked, g - imported from global
* - candidate default
IP Route Table for VRF "L3_VRF1"
B 1.1.1.1/32 [0/0] is directly connected, tunvxlan2, installed 00:20:11, last update 00:20:11 ago
B 2.2.2.2/32 [0/0] is directly connected, tunvxlan2, installed 00:20:11, last update 00:20:11 ago
B 101.101.1.0/24 [20/0] via 1.1.1.1 (recursive is directly connected, tunvxlan2), installed 00:20:11, last update 00:20:11 ago
C 127.0.0.0/8 is directly connected, lo.L3_VRF1, installed 00:21:23, last update 00:21:23 ago
B 201.101.1.0/24 [20/0] via 2.2.2.2 (recursive is directly connected, tunvxlan2), installed 00:20:11, last update 00:20:11 ago
Gateway of last resort is not set
BLEAF2#show ipv6 route vrf L3_VRF1
IPv6 Routing Table
Codes: K - kernel route, C - connected, S - static, D- DHCP, R - RIP,
O - OSPF, IA - OSPF inter area, E1 - OSPF external type 1,
E2 - OSPF external type 2, E - EVPN N1 - OSPF NSSA external type 1,
N2 - OSPF NSSA external type 2, i - IS-IS, B - BGP,
P - SRV6-POLICY,
v - vrf leaked, g - imported from global
Timers: Uptime
IP Route Table for VRF "L3_VRF1"
C ::1/128 via ::, lo.L3_VRF1, installed 00:21:24, last update 00:21:24 ago
B ::ffff:101:101/128 [0/0] via ::, tunvxlan2, installed 00:20:12, last update 00:20:12 ago
B ::ffff:202:202/128 [0/0] via ::, tunvxlan2, installed 00:20:12, last update 00:20:12 ago
B 101::/64 [20/0] via ::ffff:101:101 (recursive via ::, tunvxlan2), installed 00:20:12, last update 00:20:12 ago
B 201::/64 [20/0] via ::ffff:202:202 (recursive via ::, tunvxlan2), installed 00:20:12, last update 00:20:12 ago
C fe80::/64 via ::, tunvxlan2, installed 00:21:24, last update 00:21:24 ago
BLEAF2#show ip route vrf L3_VRF1 database
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2,
ia - IS-IS inter area, E - EVPN,
v - vrf leaked, g - imported from global
> - selected route, * - FIB route, p - stale info
IP Route Table for VRF "L3_VRF1"
B *> 1.1.1.1/32 [0/0] is directly connected, tunvxlan2, installed 00:20:12, last update 00:20:12 ago
B *> 2.2.2.2/32 [0/0] is directly connected, tunvxlan2, installed 00:20:12, last update 00:20:12 ago
B *> 101.101.1.0/24 [20/0] via 1.1.1.1 (recursive is directly connected, tunvxlan2), installed 00:20:12, last update 00:20:12 ago
B > 102.101.1.0/24 [200/0] via 26.26.26.26, installed 00:20:14, last update 00:20:14 ago
> [200/0] via 25.25.25.25
C *> 127.0.0.0/8 is directly connected, lo.L3_VRF1, installed 00:21:24, last update 00:21:24 ago
B *> 201.101.1.0/24 [20/0] via 2.2.2.2 (recursive is directly connected, tunvxlan2), installed 00:20:12, last update 00:20:12 ago
B > 202.101.1.0/24 [200/0] via 26.26.26.26, installed 00:20:14, last update 00:20:14 ago
> [200/0] via 25.25.25.25
Total number of IPv4 routes 9
Gateway of last resort is not set
BLEAF2#show ipv6 route vrf L3_VRF1 database
IPv6 Routing Table
Codes: K - kernel route, C - connected, S - static, D- DHCP, R - RIP,
O - OSPF, IA - OSPF inter area, E1 - OSPF external type 1,
E2 - OSPF external type 2, E - EVPN N1 - OSPF NSSA external type 1,
N2 - OSPF NSSA external type 2, i - IS-IS, B - BGP,
P - SRV6-POLICY,
v - vrf leaked, g - imported from global
> - selected route, * - FIB route,p - stale info
Timers: Uptime
IP Route Table for VRF "L3_VRF1"
C *> ::1/128 via ::, lo.L3_VRF1, installed 00:21:24, last update 00:21:24 ago
B *> ::ffff:101:101/128 [0/0] via ::, tunvxlan2, installed 00:20:12, last update 00:20:12 ago
B *> ::ffff:202:202/128 [0/0] via ::, tunvxlan2, installed 00:20:12, last update 00:20:12 ago
B *> 101::/64 [20/0] via ::ffff:101:101 (recursive via ::, tunvxlan2), installed 00:20:12, last update 00:20:12 ago
B > 102::/64 [200/0] via ::ffff:26.26.26.26, installed 00:20:14, last update 00:20:14 ago
> [200/0] via ::ffff:25.25.25.25
B *> 201::/64 [20/0] via ::ffff:202:202 (recursive via ::, tunvxlan2), installed 00:20:12, last update 00:20:12 ago
B > 202::/64 [200/0] via ::ffff:26.26.26.26, installed 00:20:14, last update 00:20:14 ago
> [200/0] via ::ffff:25.25.25.25
C *> fe80::/64 via ::, tunvxlan2, installed 00:21:24, last update 00:21:24 ago
Total number of IPv6 routes 10
BLEAF2#show ip bgp vpnv4 all
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal, l - labeled
S Stale, x-EVPN, w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path Ext-Color
Route Distinguisher: 14.14.14.14:101 (Default for VRF L3_VRF1)
*>x l 101.101.1.0/24 1.1.1.1 0 100 0 65001 ? -
* x 2.2.2.2 0 100 0 65001 ? -
*>iw 102.101.1.0/24 25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
* iw 26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
*>x l 201.101.1.0/24 2.2.2.2 0 100 0 65001 ? -
*>iw 202.101.1.0/24 25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
* iw 26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 7
Route Distinguisher: 15.15.15.15:951
*>iw 102.101.1.0/24 25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
*>iw 202.101.1.0/24 25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
Route Distinguisher: 16.16.16.16:951
*>iw 102.101.1.0/24 26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
*>iw 202.101.1.0/24 26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
BLEAF2#show ip bgp vpnv6 all
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal, l - labeled
S Stale, x-EVPN, w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path Ext-Color
Route Distinguisher: 14.14.14.14:101 (Default for VRF L3_VRF1)
*>x l 101::/64 ::ffff:1.1.1.1 0 100 0 65001 ? -
* x ::ffff:2.2.2.2 0 100 0 65001 ? -
*>iw 102::/64 ::ffff:25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
*aiw ::ffff:26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
*>x l 201::/64 ::ffff:2.2.2.2 0 100 0 65001 ? -
*>iw 202::/64 ::ffff:25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
*aiw ::ffff:26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 7
Route Distinguisher: 15.15.15.15:951
*>iw 102::/64 ::ffff:25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
*>iw 202::/64 ::ffff:25.25.25.25 0 100 0 65003 ? 2524:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
Route Distinguisher: 16.16.16.16:951
*>iw 102::/64 ::ffff:26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
*>iw 202::/64 ::ffff:26.26.26.26 0 100 0 65003 ? 2524:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
BLEAF2#show evpn mpls
EVPN-MPLS Information
=================
Codes: NW - Network Port
AC - Access Port
CW - Control Word
(u) - Untagged
VPN-ID EVI-Name CW EVI-Type Type Intr-VNID Interface ESI VLAN DF-Status Src-Addr Dst-Addr
___________________________________________________________________________________________________________________________________________
100001 ---- --- L2 NW 1001 ---- ---- ---- ---- 24.24.24.24 25.25.25.25
100001 ---- --- L2 NW 1001 ---- ---- ---- ---- 24.24.24.24 23.23.23.23
100001 ---- --- L2 NW 1001 ---- ---- ---- ---- 24.24.24.24 26.26.26.26
100001 ---- No -- WAN 1001 iESI 00:00:11:11:11:11:11:11:11:11 100001 DF ---- ----
100002 ---- --- L2 NW 1002 ---- ---- ---- ---- 24.24.24.24 25.25.25.25
100002 ---- --- L2 NW 1002 ---- ---- ---- ---- 24.24.24.24 23.23.23.23
100002 ---- --- L2 NW 1002 ---- ---- ---- ---- 24.24.24.24 26.26.26.26
100002 ---- No -- WAN 1002 iESI 00:00:11:22:11:11:11:11:11:11 100002 NDF ---- ----
100003 ---- --- L2 NW 1003 ---- ---- ---- ---- 24.24.24.24 25.25.25.25
100003 ---- --- L2 NW 1003 ---- ---- ---- ---- 24.24.24.24 23.23.23.23
100003 ---- --- L2 NW 1003 ---- ---- ---- ---- 24.24.24.24 26.26.26.26
100003 ---- No -- WAN 1003 iESI 00:00:11:33:11:11:11:11:11:11 100003 DF ---- ----
100004 ---- --- L2 NW 1004 ---- ---- ---- ---- 24.24.24.24 25.25.25.25
100004 ---- --- L2 NW 1004 ---- ---- ---- ---- 24.24.24.24 23.23.23.23
100004 ---- --- L2 NW 1004 ---- ---- ---- ---- 24.24.24.24 26.26.26.26
100004 ---- No -- WAN 1004 iESI 00:00:11:44:11:11:11:11:11:11 100004 NDF ---- ----
100005 ---- --- L2 NW 1005 ---- ---- ---- ---- 24.24.24.24 25.25.25.25
100005 ---- --- L2 NW 1005 ---- ---- ---- ---- 24.24.24.24 23.23.23.23
100005 ---- --- L2 NW 1005 ---- ---- ---- ---- 24.24.24.24 26.26.26.26
100005 ---- Yes -- WAN 1005 iESI 00:00:11:55:11:11:11:11:11:11 100005 DF ---- ----
100006 ---- --- L2 NW 1006 ---- ---- ---- ---- 24.24.24.24 25.25.25.25
100006 ---- --- L2 NW 1006 ---- ---- ---- ---- 24.24.24.24 23.23.23.23
100006 ---- --- L2 NW 1006 ---- ---- ---- ---- 24.24.24.24 26.26.26.26
100006 ---- No -- WAN 1006 iESI 00:00:11:66:11:11:11:11:11:11 100006 NDF ---- ----
100007 ---- --- L2 NW 1007 ---- ---- ---- ---- 24.24.24.24 25.25.25.25
100007 ---- --- L2 NW 1007 ---- ---- ---- ---- 24.24.24.24 23.23.23.23
100007 ---- --- L2 NW 1007 ---- ---- ---- ---- 24.24.24.24 26.26.26.26
100007 ---- No -- WAN 1007 iESI 00:00:11:77:11:11:11:11:11:11 100007 DF ---- ----
100008 ---- --- L2 NW 1008 ---- ---- ---- ---- 24.24.24.24 25.25.25.25
100008 ---- --- L2 NW 1008 ---- ---- ---- ---- 24.24.24.24 23.23.23.23
100008 ---- --- L2 NW 1008 ---- ---- ---- ---- 24.24.24.24 26.26.26.26
100008 ---- Yes -- WAN 1008 iESI 00:00:11:88:11:11:11:11:11:11 100008 NDF ---- ----
100009 ---- --- L2 NW 1009 ---- ---- ---- ---- 24.24.24.24 25.25.25.25
100009 ---- --- L2 NW 1009 ---- ---- ---- ---- 24.24.24.24 23.23.23.23
100009 ---- --- L2 NW 1009 ---- ---- ---- ---- 24.24.24.24 26.26.26.26
100009 ---- No -- WAN 1009 iESI 00:00:11:99:11:11:11:11:11:11 100009 DF ---- ----
100010 ---- --- L2 NW 1010 ---- ---- ---- ---- 24.24.24.24 25.25.25.25
100010 ---- --- L2 NW 1010 ---- ---- ---- ---- 24.24.24.24 23.23.23.23
100010 ---- --- L2 NW 1010 ---- ---- ---- ---- 24.24.24.24 26.26.26.26
100010 ---- No -- WAN 1010 iESI 00:00:11:99:11:11:11:11:11:11 100010 NDF ---- ----
Total number of entries are 40
Note: Refer sub-interface config for VLAN information.
BLEAF2#show evpn mpls tunnel
EVPN-MPLS Network tunnel Entries
Source Destination Status Up/Down Update evpn-id Local-Leaf Remote-Leaf Ext-Color FAT CW
========================================================================================================================================
24.24.24.24 25.25.25.25 Installed 00:20:13 00:20:12 100010 --- --- --- --- No
24.24.24.24 25.25.25.25 Installed 00:20:13 00:20:12 100009 --- --- --- --- No
24.24.24.24 25.25.25.25 Installed 00:20:13 00:20:12 100008 --- --- --- set Yes
24.24.24.24 25.25.25.25 Installed 00:20:13 00:20:12 100007 --- --- --- set No
24.24.24.24 25.25.25.25 Installed 00:20:13 00:20:12 100006 --- --- --- --- No
24.24.24.24 25.25.25.25 Installed 00:20:13 00:20:12 100005 --- --- --- --- Yes
24.24.24.24 25.25.25.25 Installed 00:20:13 00:20:12 100004 --- --- --- --- No
24.24.24.24 25.25.25.25 Installed 00:20:13 00:20:12 100003 --- --- --- --- No
24.24.24.24 25.25.25.25 Installed 00:20:13 00:20:12 100002 --- --- --- --- No
24.24.24.24 25.25.25.25 Installed 00:20:13 00:20:12 100001 --- --- --- --- No
24.24.24.24 23.23.23.23 Installed 00:20:13 00:20:12 100010 --- --- --- --- No
24.24.24.24 23.23.23.23 Installed 00:20:13 00:20:12 100009 --- --- --- --- No
24.24.24.24 23.23.23.23 Installed 00:20:13 00:20:12 100008 --- --- --- set Yes
24.24.24.24 23.23.23.23 Installed 00:20:13 00:20:12 100007 --- --- --- set No
24.24.24.24 23.23.23.23 Installed 00:20:13 00:20:12 100006 --- --- --- --- No
24.24.24.24 23.23.23.23 Installed 00:20:13 00:20:12 100005 --- --- --- --- Yes
24.24.24.24 23.23.23.23 Installed 00:20:13 00:20:12 100004 --- --- --- --- No
24.24.24.24 23.23.23.23 Installed 00:20:13 00:20:12 100003 --- --- --- --- No
24.24.24.24 23.23.23.23 Installed 00:20:13 00:20:12 100002 --- --- --- --- No
24.24.24.24 23.23.23.23 Installed 00:20:13 00:20:12 100001 --- --- --- --- No
24.24.24.24 26.26.26.26 Installed 00:20:13 00:20:12 100010 --- --- --- --- No
24.24.24.24 26.26.26.26 Installed 00:20:13 00:20:12 100009 --- --- --- --- No
24.24.24.24 26.26.26.26 Installed 00:20:13 00:20:12 100008 --- --- --- set Yes
24.24.24.24 26.26.26.26 Installed 00:20:13 00:20:12 100007 --- --- --- set No
24.24.24.24 26.26.26.26 Installed 00:20:13 00:20:12 100006 --- --- --- --- No
24.24.24.24 26.26.26.26 Installed 00:20:13 00:20:12 100005 --- --- --- --- Yes
24.24.24.24 26.26.26.26 Installed 00:20:13 00:20:12 100004 --- --- --- --- No
24.24.24.24 26.26.26.26 Installed 00:20:13 00:20:12 100003 --- --- --- --- No
24.24.24.24 26.26.26.26 Installed 00:20:13 00:20:12 100002 --- --- --- --- No
24.24.24.24 26.26.26.26 Installed 00:20:13 00:20:12 100001 --- --- --- --- No
Total number of entries are 30
BLEAF2#show evpn mpls access-if brief
Inner Admin Link
Interface Vlan vlan Ifindex Vnid status status
---------------------------------------------------------------
Total number of entries are 0
Note: Refer sub-interface config for VLAN information.
BLEAF2#show ldp session
Codes: m - MD5 password is not set/unset.
g - GR configuration not set/unset.
t - TCP MSS not set/unset.
Session has to be cleared manually
Code Peer IP Address IF Name My Role State KeepAlive UpTime AutoCreate
13.13.13.13 ce4 Active OPERATIONAL 30 00:20:13 No
18.18.18.18 xe47 Passive OPERATIONAL 30 00:20:13 No
17.17.17.17 xe48 Passive OPERATIONAL 30 00:20:13 No
BLEAF2#show mpls forwarding-table
Codes: > - installed FTN, * - selected FTN, p - stale FTN, ! - using backup
B - BGP FTN, K - CLI FTN, (t) - tunnel, P - SR Policy FTN, (b) - bypass,
L - LDP FTN, R - RSVP-TE FTN, S - SNMP FTN, I - IGP-Shortcut,
U - unknown FTN, O - SR-OSPF FTN, i - SR-ISIS FTN, k - SR-CLI FTN
(m) - FTN mapped over multipath transport, (e) - FTN is ECMP
FTN-ECMP LDP: Disabled, SR: Disabled
Code FEC FTN-ID Nhlfe-ID Tunnel-ID Pri Out-Label Out-Intf ELC Nexthop Algo-Num UpTime
L> 17.17.17.17/32 8 15 - - - - - - N/A 00:21:06
14 - Yes 3 xe48 No 104.1.1.2 - -
L> 18.18.18.18/32 1 5 - - - - - - N/A 00:21:07
4 - Yes 3 xe47 No 104.1.2.2 - -
L> 23.23.23.23/32 2 18 - - - - - - N/A 00:21:07
17 - Yes 24340 xe48 No 104.1.1.2 - -
7 - Yes 24340 xe47 No 104.1.2.2 - -
L> 25.25.25.25/32 3 20 - - - - - - N/A 00:21:07
19 - Yes 24337 xe48 No 104.1.1.2 - -
9 - Yes 24337 xe47 No 104.1.2.2 - -
L> 26.26.26.26/32 4 22 - - - - - - N/A 00:21:07
21 - Yes 24322 xe48 No 104.1.1.2 - -
12 - Yes 24322 xe47 No 104.1.2.2 - -
L> 103.1.1.0/24 9 15 - - - - - - N/A 00:21:06
14 - Yes 3 xe48 No 104.1.1.2 - -
L> 103.1.2.0/24 5 5 - - - - - - N/A 00:21:07
4 - Yes 3 xe47 No 104.1.2.2 - -
L> 105.1.1.0/24 10 15 - - - - - - N/A 00:21:06
14 - Yes 3 xe48 No 104.1.1.2 - -
L> 105.1.2.0/24 6 5 - - - - - - N/A 00:21:07
4 - Yes 3 xe47 No 104.1.2.2 - -
L> 106.1.1.0/24 11 15 - - - - - - N/A 00:21:06
14 - Yes 3 xe48 No 104.1.1.2 - -
L> 106.1.2.0/24 7 5 - - - - - - N/A 00:21:07
4 - Yes 3 xe47 No 104.1.2.2 - -
BLEAF2#show bgp l2vpn evpn prefix-route
BGP table version is 35, local router ID is 14.14.14.14
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal,
l - labeled, S Stale w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Description : Ext-Color - Extended community color
RD[1.1.1.1:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 101.101.1.0 0.0.0.0 1000 1.1.1.1 1.1.1.1 VXLAN 1444:8f6c:47ec
* 0 0 24 101.101.1.0 0.0.0.0 1000 1.1.1.1 2.2.2.2 VXLAN 1444:8f6c:47ec
*> 0 0 64 101:: :: 1000 1.1.1.1 1.1.1.1 VXLAN 1444:8f6c:47ec
* 0 0 64 101:: :: 1000 1.1.1.1 2.2.2.2 VXLAN 1444:8f6c:47ec
RD[2.2.2.2:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 101.101.1.0 0.0.0.0 1000 2.2.2.2 1.1.1.1 VXLAN e001:a6a9:4b01
* 0 0 24 101.101.1.0 0.0.0.0 1000 2.2.2.2 2.2.2.2 VXLAN e001:a6a9:4b01
*> 0 0 24 201.101.1.0 0.0.0.0 1000 2.2.2.2 1.1.1.1 VXLAN e001:a6a9:4b01
* 0 0 24 201.101.1.0 0.0.0.0 1000 2.2.2.2 2.2.2.2 VXLAN e001:a6a9:4b01
*> 0 0 64 101:: :: 1000 2.2.2.2 1.1.1.1 VXLAN e001:a6a9:4b01
* 0 0 64 101:: :: 1000 2.2.2.2 2.2.2.2 VXLAN e001:a6a9:4b01
*> 0 0 64 201:: :: 1000 2.2.2.2 1.1.1.1 VXLAN e001:a6a9:4b01
* 0 0 64 201:: :: 1000 2.2.2.2 2.2.2.2 VXLAN e001:a6a9:4b01
BLEAF2#
BLEAF2#show evpn multi-homing domain-tracking-status
iESI Domain Tracking Status
===========================
iESI-configured VRFs : 10
Configured peer-GW VTEPs (BGP-pushed) : 13.13.13.13(DC,no tunnel),23.23.23.23(WAN,tunnel exists)
Resolved-transit tunnels (peer GW excluded):
DC : 2 => DC ACTIVE
WAN : 20 => WAN ACTIVE
Per-VRF iESI object state:
VRF Domain ESI Isolated Withdrawn Tenants Peer GW(s)
--------------------------------------------------------------------------------------------------------
L2_VRF1 DC 00:00:11:11:11:11:11:11:11:11 no no 1 -
L2_VRF1 WAN 00:00:11:11:11:11:11:11:11:11 no no 1 23.23.23.23
L2_VRF10 DC 00:00:11:99:11:11:11:11:11:11 no no 2 -
L2_VRF10 WAN 00:00:11:99:11:11:11:11:11:11 no no 2 23.23.23.23
L2_VRF2 DC 00:00:11:22:11:11:11:11:11:11 no no 1 -
L2_VRF2 WAN 00:00:11:22:11:11:11:11:11:11 no no 1 23.23.23.23
L2_VRF3 DC 00:00:11:33:11:11:11:11:11:11 no no 1 -
L2_VRF3 WAN 00:00:11:33:11:11:11:11:11:11 no no 1 23.23.23.23
L2_VRF4 DC 00:00:11:44:11:11:11:11:11:11 no no 1 -
L2_VRF4 WAN 00:00:11:44:11:11:11:11:11:11 no no 1 23.23.23.23
L2_VRF5 DC 00:00:11:55:11:11:11:11:11:11 no no 1 -
L2_VRF5 WAN 00:00:11:55:11:11:11:11:11:11 no no 1 23.23.23.23
L2_VRF6 DC 00:00:11:66:11:11:11:11:11:11 no no 1 -
L2_VRF6 WAN 00:00:11:66:11:11:11:11:11:11 no no 1 23.23.23.23
L2_VRF7 DC 00:00:11:77:11:11:11:11:11:11 no no 1 -
L2_VRF7 WAN 00:00:11:77:11:11:11:11:11:11 no no 1 23.23.23.23
L2_VRF8 DC 00:00:11:88:11:11:11:11:11:11 no no 1 -
L2_VRF8 WAN 00:00:11:88:11:11:11:11:11:11 no no 1 23.23.23.23
L2_VRF9 DC 00:00:11:99:11:11:11:11:11:11 no no 2 -
L2_VRF9 WAN 00:00:11:99:11:11:11:11:11:11 no no 2 23.23.23.23
BLEAF2#
=============================================
BLEAF3
=============================================
BLEAF3#show ip ospf neighbor
Total number of full neighbors: 4
OSPF process 100 VRF(default):
Neighbor ID Pri State Dead Time Address Interface Instance ID
9.9.9.9 1 Full/Backup 00:00:37 90.1.1.1 ce2 0
10.10.10.10 1 Full/Backup 00:00:33 100.1.1.1 ce4 0
17.17.17.17 1 Full/DR 00:00:36 105.1.1.2 ce14/1 0
18.18.18.18 1 Full/DR 00:00:29 105.1.2.2 ce14/2 0
BLEAF3#show bgp l2vpn evpn summary
BGP router identifier 15.15.15.15, local AS number 65002
BGP table version is 38
3 BGP AS-PATH entries
0 BGP community entries
Neighbor V AS MsgRcv MsgSen TblVer InQ OutQ Up/Down State/PfxRcd AD MACIP MCAST ESI PREFIX-ROUTE Desc
4.4.4.4 4 65003 307 182 38 0 0 00:23:49 210 22 162 20 0 6
5.5.5.5 4 65003 306 168 38 0 0 00:23:50 210 22 162 20 0 6
23.23.23.23 4 65002 198 132 38 0 0 00:22:03 260 19 231 10 0 0
24.24.24.24 4 65002 125 149 38 0 0 00:20:17 187 19 158 10 0 0
26.26.26.26 4 65002 165 134 38 0 0 00:23:47 38 19 0 10 9 0
Total number of neighbors 5
Total number of Established sessions 5
BLEAF3#show nvo vxlan
VXLAN Information
=================
Codes: NW - Network Port
AC - Access Port
(u) - Untagged
VNID VNI-Name VNI-Type Type Intr-VNID Interface ESI VLAN DF-Status Src-Addr Dst-Addr Router-Mac
_______________________________________________________________________________________________________________________________________________________________
1000 ---- L3 NW ---- ---- ---- ---- ---- 15.15.15.15 4.4.4.4 7c8d.9caa.5231
1000 ---- L3 NW ---- ---- ---- ---- ---- 15.15.15.15 5.5.5.5 5c17.83ff.2255
1001 ---- L2 NW 100001 ---- ---- ---- ---- 15.15.15.15 4.4.4.4 --------------
1001 ---- L2 NW 100001 ---- ---- ---- ---- 15.15.15.15 5.5.5.5 --------------
1001 ---- -- DC 100001 iESI 00:00:22:11:11:11:11:11:11:11 1001 N/A(DC) ---- ----
1002 ---- L2 NW 100002 ---- ---- ---- ---- 15.15.15.15 4.4.4.4 --------------
1002 ---- L2 NW 100002 ---- ---- ---- ---- 15.15.15.15 5.5.5.5 --------------
1002 ---- -- DC 100002 iESI 00:00:22:22:11:11:11:11:11:11 1002 N/A(DC) ---- ----
1003 ---- L2 NW 100003 ---- ---- ---- ---- 15.15.15.15 4.4.4.4 --------------
1003 ---- L2 NW 100003 ---- ---- ---- ---- 15.15.15.15 5.5.5.5 --------------
1003 ---- -- DC 100003 iESI 00:00:22:33:11:11:11:11:11:11 1003 N/A(DC) ---- ----
1004 ---- L2 NW 100004 ---- ---- ---- ---- 15.15.15.15 4.4.4.4 --------------
1004 ---- L2 NW 100004 ---- ---- ---- ---- 15.15.15.15 5.5.5.5 --------------
1004 ---- -- DC 100004 iESI 00:00:22:44:11:11:11:11:11:11 1004 N/A(DC) ---- ----
1005 ---- L2 NW 100005 ---- ---- ---- ---- 15.15.15.15 4.4.4.4 --------------
1005 ---- L2 NW 100005 ---- ---- ---- ---- 15.15.15.15 5.5.5.5 --------------
1005 ---- -- DC 100005 iESI 00:00:22:55:11:11:11:11:11:11 1005 N/A(DC) ---- ----
1006 ---- L2 NW 100006 ---- ---- ---- ---- 15.15.15.15 4.4.4.4 --------------
1006 ---- L2 NW 100006 ---- ---- ---- ---- 15.15.15.15 5.5.5.5 --------------
1006 ---- -- DC 100006 iESI 00:00:22:66:11:11:11:11:11:11 1006 N/A(DC) ---- ----
1007 ---- L2 NW 100007 ---- ---- ---- ---- 15.15.15.15 4.4.4.4 --------------
1007 ---- L2 NW 100007 ---- ---- ---- ---- 15.15.15.15 5.5.5.5 --------------
1007 ---- -- DC 100007 iESI 00:00:22:77:11:11:11:11:11:11 1007 N/A(DC) ---- ----
1008 ---- L2 NW 100008 ---- ---- ---- ---- 15.15.15.15 4.4.4.4 --------------
1008 ---- L2 NW 100008 ---- ---- ---- ---- 15.15.15.15 5.5.5.5 --------------
1008 ---- -- DC 100008 iESI 00:00:22:88:11:11:11:11:11:11 1008 N/A(DC) ---- ----
1009 ---- L2 NW 100009 ---- ---- ---- ---- 15.15.15.15 4.4.4.4 --------------
1009 ---- L2 NW 100009 ---- ---- ---- ---- 15.15.15.15 5.5.5.5 --------------
1009 ---- -- DC 100009 iESI 00:00:22:99:11:11:11:11:11:11 1009 N/A(DC) ---- ----
1010 ---- L2 NW 100010 ---- ---- ---- ---- 15.15.15.15 4.4.4.4 --------------
1010 ---- L2 NW 100010 ---- ---- ---- ---- 15.15.15.15 5.5.5.5 --------------
1010 ---- -- DC 100010 iESI 00:00:22:99:11:11:11:11:11:11 1010 N/A(DC) ---- ----
Total number of entries are 32
Note: Refer sub-interface config for VLAN information.
BLEAF3#show nvo vxlan tunnel
VXLAN Network tunnel Entries
Source Destination Status Up/Down Update
========================================================================
15.15.15.15 4.4.4.4 Installed 00:23:48 00:23:48
15.15.15.15 5.5.5.5 Installed 00:23:48 00:23:48
Total number of entries are 2
BLEAF3#show nvo vxlan access-if brief
Inner Admin Link
Interface Vlan vlan Ifindex Vnid status status
---------------------------------------------------------------
Total number of entries are 0
Note: Refer sub-interface config for VLAN information.
BLEAF3#show etherchannel summary
BLEAF3#show ip route vrf L3_VRF1
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2,
ia - IS-IS inter area, E - EVPN,
v - vrf leaked, g - imported from global
* - candidate default
IP Route Table for VRF "L3_VRF1"
B 4.4.4.4/32 [0/0] is directly connected, tunvxlan2, installed 00:23:48, last update 00:23:48 ago
B 5.5.5.5/32 [0/0] is directly connected, tunvxlan2, installed 00:23:48, last update 00:23:48 ago
B 102.101.1.0/24 [20/0] via 4.4.4.4 (recursive is directly connected, tunvxlan2), installed 00:23:48, last update 00:23:48 ago
C 127.0.0.0/8 is directly connected, lo.L3_VRF1, installed 00:24:49, last update 00:24:49 ago
B 202.101.1.0/24 [20/0] via 5.5.5.5 (recursive is directly connected, tunvxlan2), installed 00:23:48, last update 00:23:48 ago
Gateway of last resort is not set
BLEAF3#show ipv6 route vrf L3_VRF1
IPv6 Routing Table
Codes: K - kernel route, C - connected, S - static, D- DHCP, R - RIP,
O - OSPF, IA - OSPF inter area, E1 - OSPF external type 1,
E2 - OSPF external type 2, E - EVPN N1 - OSPF NSSA external type 1,
N2 - OSPF NSSA external type 2, i - IS-IS, B - BGP,
P - SRV6-POLICY,
v - vrf leaked, g - imported from global
Timers: Uptime
IP Route Table for VRF "L3_VRF1"
C ::1/128 via ::, lo.L3_VRF1, installed 00:24:50, last update 00:24:50 ago
B ::ffff:404:404/128 [0/0] via ::, tunvxlan2, installed 00:23:49, last update 00:23:49 ago
B ::ffff:505:505/128 [0/0] via ::, tunvxlan2, installed 00:23:49, last update 00:23:49 ago
B 102::/64 [20/0] via ::ffff:404:404 (recursive via ::, tunvxlan2), installed 00:23:49, last update 00:23:49 ago
B 202::/64 [20/0] via ::ffff:505:505 (recursive via ::, tunvxlan2), installed 00:23:49, last update 00:23:49 ago
C fe80::/64 via ::, tunvxlan2, installed 00:24:50, last update 00:24:50 ago
BLEAF3#show ip route vrf L3_VRF1 database
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2,
ia - IS-IS inter area, E - EVPN,
v - vrf leaked, g - imported from global
> - selected route, * - FIB route, p - stale info
IP Route Table for VRF "L3_VRF1"
B *> 4.4.4.4/32 [0/0] is directly connected, tunvxlan2, installed 00:23:49, last update 00:23:49 ago
B *> 5.5.5.5/32 [0/0] is directly connected, tunvxlan2, installed 00:23:49, last update 00:23:49 ago
B > 101.101.1.0/24 [200/0] via 24.24.24.24, installed 00:21:47, last update 00:20:12 ago
> [200/0] via 23.23.23.23
B *> 102.101.1.0/24 [20/0] via 4.4.4.4 (recursive is directly connected, tunvxlan2), installed 00:23:49, last update 00:23:49 ago
C *> 127.0.0.0/8 is directly connected, lo.L3_VRF1, installed 00:24:50, last update 00:24:50 ago
B > 201.101.1.0/24 [200/0] via 24.24.24.24, installed 00:21:47, last update 00:20:12 ago
> [200/0] via 23.23.23.23
B *> 202.101.1.0/24 [20/0] via 5.5.5.5 (recursive is directly connected, tunvxlan2), installed 00:23:49, last update 00:23:49 ago
Total number of IPv4 routes 9
Gateway of last resort is not set
BLEAF3#show ipv6 route vrf L3_VRF1 database
IPv6 Routing Table
Codes: K - kernel route, C - connected, S - static, D- DHCP, R - RIP,
O - OSPF, IA - OSPF inter area, E1 - OSPF external type 1,
E2 - OSPF external type 2, E - EVPN N1 - OSPF NSSA external type 1,
N2 - OSPF NSSA external type 2, i - IS-IS, B - BGP,
P - SRV6-POLICY,
v - vrf leaked, g - imported from global
> - selected route, * - FIB route,p - stale info
Timers: Uptime
IP Route Table for VRF "L3_VRF1"
C *> ::1/128 via ::, lo.L3_VRF1, installed 00:24:50, last update 00:24:50 ago
B *> ::ffff:404:404/128 [0/0] via ::, tunvxlan2, installed 00:23:49, last update 00:23:49 ago
B *> ::ffff:505:505/128 [0/0] via ::, tunvxlan2, installed 00:23:49, last update 00:23:49 ago
B > 101::/64 [200/0] via ::ffff:24.24.24.24, installed 00:21:47, last update 00:20:12 ago
> [200/0] via ::ffff:23.23.23.23
B *> 102::/64 [20/0] via ::ffff:404:404 (recursive via ::, tunvxlan2), installed 00:23:49, last update 00:23:49 ago
B > 201::/64 [200/0] via ::ffff:24.24.24.24, installed 00:21:47, last update 00:20:12 ago
> [200/0] via ::ffff:23.23.23.23
B *> 202::/64 [20/0] via ::ffff:505:505 (recursive via ::, tunvxlan2), installed 00:23:49, last update 00:23:49 ago
C *> fe80::/64 via ::, tunvxlan2, installed 00:24:50, last update 00:24:50 ago
Total number of IPv6 routes 10
BLEAF3#show ip bgp vpnv4 all
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal, l - labeled
S Stale, x-EVPN, w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path Ext-Color
Route Distinguisher: 13.13.13.13:951
*>iw 101.101.1.0/24 23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
*>iw 201.101.1.0/24 23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
Route Distinguisher: 14.14.14.14:951
*>iw 101.101.1.0/24 24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
*>iw 201.101.1.0/24 24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
Route Distinguisher: 15.15.15.15:101 (Default for VRF L3_VRF1)
*>iw 101.101.1.0/24 23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
* iw 24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
*>x l 102.101.1.0/24 4.4.4.4 0 100 0 65003 ? -
* x 5.5.5.5 0 100 0 65003 ? -
*>iw 201.101.1.0/24 23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
* iw 24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
*>x l 202.101.1.0/24 5.5.5.5 0 100 0 65003 ? -
VRF Origin Route count = 0
Accepted routes count = 7
BLEAF3#show ip bgp vpnv6 all
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal, l - labeled
S Stale, x-EVPN, w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path Ext-Color
Route Distinguisher: 13.13.13.13:951
*>iw 101::/64 ::ffff:23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
*>iw 201::/64 ::ffff:23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
Route Distinguisher: 14.14.14.14:951
*>iw 101::/64 ::ffff:24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
*>iw 201::/64 ::ffff:24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
Route Distinguisher: 15.15.15.15:101 (Default for VRF L3_VRF1)
*>iw 101::/64 ::ffff:23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
*aiw ::ffff:24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
*>x l 102::/64 ::ffff:4.4.4.4 0 100 0 65003 ? -
* x ::ffff:5.5.5.5 0 100 0 65003 ? -
*>iw 201::/64 ::ffff:23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
*aiw ::ffff:24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
*>x l 202::/64 ::ffff:5.5.5.5 0 100 0 65003 ? -
VRF Origin Route count = 0
Accepted routes count = 7
BLEAF3#show evpn mpls
EVPN-MPLS Information
=================
Codes: NW - Network Port
AC - Access Port
CW - Control Word
(u) - Untagged
VPN-ID EVI-Name CW EVI-Type Type Intr-VNID Interface ESI VLAN DF-Status Src-Addr Dst-Addr
___________________________________________________________________________________________________________________________________________
100001 ---- --- L2 NW 1001 ---- ---- ---- ---- 25.25.25.25 24.24.24.24
100001 ---- --- L2 NW 1001 ---- ---- ---- ---- 25.25.25.25 26.26.26.26
100001 ---- --- L2 NW 1001 ---- ---- ---- ---- 25.25.25.25 23.23.23.23
100001 ---- No -- WAN 1001 iESI 00:00:22:11:11:11:11:11:11:11 100001 NDF ---- ----
100002 ---- --- L2 NW 1002 ---- ---- ---- ---- 25.25.25.25 24.24.24.24
100002 ---- --- L2 NW 1002 ---- ---- ---- ---- 25.25.25.25 26.26.26.26
100002 ---- --- L2 NW 1002 ---- ---- ---- ---- 25.25.25.25 23.23.23.23
100002 ---- No -- WAN 1002 iESI 00:00:22:22:11:11:11:11:11:11 100002 DF ---- ----
100003 ---- --- L2 NW 1003 ---- ---- ---- ---- 25.25.25.25 24.24.24.24
100003 ---- --- L2 NW 1003 ---- ---- ---- ---- 25.25.25.25 26.26.26.26
100003 ---- --- L2 NW 1003 ---- ---- ---- ---- 25.25.25.25 23.23.23.23
100003 ---- No -- WAN 1003 iESI 00:00:22:33:11:11:11:11:11:11 100003 NDF ---- ----
100004 ---- --- L2 NW 1004 ---- ---- ---- ---- 25.25.25.25 24.24.24.24
100004 ---- --- L2 NW 1004 ---- ---- ---- ---- 25.25.25.25 26.26.26.26
100004 ---- --- L2 NW 1004 ---- ---- ---- ---- 25.25.25.25 23.23.23.23
100004 ---- No -- WAN 1004 iESI 00:00:22:44:11:11:11:11:11:11 100004 DF ---- ----
100005 ---- --- L2 NW 1005 ---- ---- ---- ---- 25.25.25.25 24.24.24.24
100005 ---- --- L2 NW 1005 ---- ---- ---- ---- 25.25.25.25 26.26.26.26
100005 ---- --- L2 NW 1005 ---- ---- ---- ---- 25.25.25.25 23.23.23.23
100005 ---- Yes -- WAN 1005 iESI 00:00:22:55:11:11:11:11:11:11 100005 NDF ---- ----
100006 ---- --- L2 NW 1006 ---- ---- ---- ---- 25.25.25.25 24.24.24.24
100006 ---- --- L2 NW 1006 ---- ---- ---- ---- 25.25.25.25 26.26.26.26
100006 ---- --- L2 NW 1006 ---- ---- ---- ---- 25.25.25.25 23.23.23.23
100006 ---- No -- WAN 1006 iESI 00:00:22:66:11:11:11:11:11:11 100006 DF ---- ----
100007 ---- --- L2 NW 1007 ---- ---- ---- ---- 25.25.25.25 24.24.24.24
100007 ---- --- L2 NW 1007 ---- ---- ---- ---- 25.25.25.25 26.26.26.26
100007 ---- --- L2 NW 1007 ---- ---- ---- ---- 25.25.25.25 23.23.23.23
100007 ---- No -- WAN 1007 iESI 00:00:22:77:11:11:11:11:11:11 100007 NDF ---- ----
100008 ---- --- L2 NW 1008 ---- ---- ---- ---- 25.25.25.25 24.24.24.24
100008 ---- --- L2 NW 1008 ---- ---- ---- ---- 25.25.25.25 26.26.26.26
100008 ---- --- L2 NW 1008 ---- ---- ---- ---- 25.25.25.25 23.23.23.23
100008 ---- Yes -- WAN 1008 iESI 00:00:22:88:11:11:11:11:11:11 100008 DF ---- ----
100009 ---- --- L2 NW 1009 ---- ---- ---- ---- 25.25.25.25 24.24.24.24
100009 ---- --- L2 NW 1009 ---- ---- ---- ---- 25.25.25.25 26.26.26.26
100009 ---- --- L2 NW 1009 ---- ---- ---- ---- 25.25.25.25 23.23.23.23
100009 ---- No -- WAN 1009 iESI 00:00:22:99:11:11:11:11:11:11 100009 NDF ---- ----
100010 ---- --- L2 NW 1010 ---- ---- ---- ---- 25.25.25.25 24.24.24.24
100010 ---- --- L2 NW 1010 ---- ---- ---- ---- 25.25.25.25 26.26.26.26
100010 ---- --- L2 NW 1010 ---- ---- ---- ---- 25.25.25.25 23.23.23.23
100010 ---- No -- WAN 1010 iESI 00:00:22:99:11:11:11:11:11:11 100010 DF ---- ----
Total number of entries are 40
Note: Refer sub-interface config for VLAN information.
BLEAF3#show evpn mpls tunnel
EVPN-MPLS Network tunnel Entries
Source Destination Status Up/Down Update evpn-id Local-Leaf Remote-Leaf Ext-Color FAT CW
========================================================================================================================================
25.25.25.25 24.24.24.24 Installed 00:20:17 00:20:17 100010 --- --- --- --- No
25.25.25.25 24.24.24.24 Installed 00:20:17 00:20:17 100009 --- --- --- --- No
25.25.25.25 24.24.24.24 Installed 00:20:17 00:20:17 100008 --- --- --- set Yes
25.25.25.25 24.24.24.24 Installed 00:20:17 00:20:17 100007 --- --- --- set No
25.25.25.25 24.24.24.24 Installed 00:20:17 00:20:17 100006 --- --- --- --- No
25.25.25.25 24.24.24.24 Installed 00:20:17 00:20:17 100005 --- --- --- --- Yes
25.25.25.25 24.24.24.24 Installed 00:20:17 00:20:17 100004 --- --- --- --- No
25.25.25.25 24.24.24.24 Installed 00:20:17 00:20:17 100003 --- --- --- --- No
25.25.25.25 24.24.24.24 Installed 00:20:17 00:20:17 100002 --- --- --- --- No
25.25.25.25 24.24.24.24 Installed 00:20:17 00:20:17 100001 --- --- --- --- No
25.25.25.25 26.26.26.26 Installed 00:23:23 00:23:22 100010 --- --- --- --- No
25.25.25.25 26.26.26.26 Installed 00:23:23 00:23:22 100009 --- --- --- --- No
25.25.25.25 26.26.26.26 Installed 00:23:23 00:23:22 100008 --- --- --- set Yes
25.25.25.25 26.26.26.26 Installed 00:23:23 00:23:22 100007 --- --- --- set No
25.25.25.25 26.26.26.26 Installed 00:23:23 00:23:22 100006 --- --- --- --- No
25.25.25.25 26.26.26.26 Installed 00:23:23 00:23:22 100005 --- --- --- --- Yes
25.25.25.25 26.26.26.26 Installed 00:23:23 00:23:22 100004 --- --- --- --- No
25.25.25.25 26.26.26.26 Installed 00:23:23 00:23:22 100003 --- --- --- --- No
25.25.25.25 26.26.26.26 Installed 00:23:23 00:23:22 100002 --- --- --- --- No
25.25.25.25 26.26.26.26 Installed 00:23:23 00:23:22 100001 --- --- --- --- No
25.25.25.25 23.23.23.23 Installed 00:21:58 00:21:58 100010 --- --- --- --- No
25.25.25.25 23.23.23.23 Installed 00:21:58 00:21:58 100009 --- --- --- --- No
25.25.25.25 23.23.23.23 Installed 00:21:58 00:21:58 100008 --- --- --- set Yes
25.25.25.25 23.23.23.23 Installed 00:21:58 00:21:58 100007 --- --- --- set No
25.25.25.25 23.23.23.23 Installed 00:21:58 00:21:58 100006 --- --- --- --- No
25.25.25.25 23.23.23.23 Installed 00:21:58 00:21:58 100005 --- --- --- --- Yes
25.25.25.25 23.23.23.23 Installed 00:21:58 00:21:58 100004 --- --- --- --- No
25.25.25.25 23.23.23.23 Installed 00:21:58 00:21:58 100003 --- --- --- --- No
25.25.25.25 23.23.23.23 Installed 00:21:58 00:21:58 100002 --- --- --- --- No
25.25.25.25 23.23.23.23 Installed 00:21:58 00:21:58 100001 --- --- --- --- No
Total number of entries are 30
BLEAF3#show evpn mpls access-if brief
Inner Admin Link
Interface Vlan vlan Ifindex Vnid status status
---------------------------------------------------------------
Total number of entries are 0
Note: Refer sub-interface config for VLAN information.
BLEAF3#show ldp session
Codes: m - MD5 password is not set/unset.
g - GR configuration not set/unset.
t - TCP MSS not set/unset.
Session has to be cleared manually
Code Peer IP Address IF Name My Role State KeepAlive UpTime AutoCreate
16.16.16.16 ce4 Passive OPERATIONAL 30 00:23:30 No
17.17.17.17 ce14/1 Passive OPERATIONAL 30 00:23:23 No
18.18.18.18 ce14/2 Passive OPERATIONAL 30 00:23:26 No
BLEAF3#show mpls forwarding-table
Codes: > - installed FTN, * - selected FTN, p - stale FTN, ! - using backup
B - BGP FTN, K - CLI FTN, (t) - tunnel, P - SR Policy FTN, (b) - bypass,
L - LDP FTN, R - RSVP-TE FTN, S - SNMP FTN, I - IGP-Shortcut,
U - unknown FTN, O - SR-OSPF FTN, i - SR-ISIS FTN, k - SR-CLI FTN
(m) - FTN mapped over multipath transport, (e) - FTN is ECMP
FTN-ECMP LDP: Disabled, SR: Disabled
Code FEC FTN-ID Nhlfe-ID Tunnel-ID Pri Out-Label Out-Intf ELC Nexthop Algo-Num UpTime
L> 17.17.17.17/32 4 9 - - - - - - N/A 00:23:22
8 - Yes 3 ce14/1 No 105.1.1.2 - -
L> 18.18.18.18/32 1 3 - - - - - - N/A 00:23:23
2 - Yes 3 ce14/2 No 105.1.2.2 - -
L> 23.23.23.23/32 8 15 - - - - - - N/A 00:21:58
13 - Yes 24340 ce14/1 No 105.1.1.2 - -
14 - Yes 24340 ce14/2 No 105.1.2.2 - -
L> 24.24.24.24/32 13 28 - - - - - - N/A 00:20:18
26 - Yes 24356 ce14/2 No 105.1.2.2 - -
27 - Yes 24356 ce14/1 No 105.1.1.2 - -
L> 26.26.26.26/32 2 6 - - - - - - N/A 00:23:23
5 - Yes 24322 ce14/2 No 105.1.2.2 - -
11 - Yes 24322 ce14/1 No 105.1.1.2 - -
L> 103.1.1.0/24 6 9 - - - - - - N/A 00:22:48
8 - Yes 3 ce14/1 No 105.1.1.2 - -
L> 103.1.2.0/24 7 3 - - - - - - N/A 00:22:48
2 - Yes 3 ce14/2 No 105.1.2.2 - -
L> 104.1.1.0/24 11 21 - - - - - - N/A 00:21:06
20 - Yes 24355 ce14/1 No 105.1.1.2 - -
L> 104.1.2.0/24 12 24 - - - - - - N/A 00:21:06
23 - Yes 24355 ce14/2 No 105.1.2.2 - -
L> 106.1.1.0/24 5 9 - - - - - - N/A 00:23:22
8 - Yes 3 ce14/1 No 105.1.1.2 - -
L> 106.1.2.0/24 3 3 - - - - - - N/A 00:23:23
2 - Yes 3 ce14/2 No 105.1.2.2 - -
BLEAF3#show bgp l2vpn evpn prefix-route
BGP table version is 38, local router ID is 15.15.15.15
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal,
l - labeled, S Stale w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Description : Ext-Color - Extended community color
RD[4.4.4.4:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 102.101.1.0 0.0.0.0 1000 4.4.4.4 5.5.5.5 VXLAN 7c8d:9caa:5231
* 0 0 24 102.101.1.0 0.0.0.0 1000 4.4.4.4 4.4.4.4 VXLAN 7c8d:9caa:5231
*> 0 0 64 102:: :: 1000 4.4.4.4 5.5.5.5 VXLAN 7c8d:9caa:5231
* 0 0 64 102:: :: 1000 4.4.4.4 4.4.4.4 VXLAN 7c8d:9caa:5231
RD[5.5.5.5:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 102.101.1.0 0.0.0.0 1000 5.5.5.5 5.5.5.5 VXLAN 5c17:83ff:2255
* 0 0 24 102.101.1.0 0.0.0.0 1000 5.5.5.5 4.4.4.4 VXLAN 5c17:83ff:2255
*> 0 0 24 202.101.1.0 0.0.0.0 1000 5.5.5.5 5.5.5.5 VXLAN 5c17:83ff:2255
* 0 0 24 202.101.1.0 0.0.0.0 1000 5.5.5.5 4.4.4.4 VXLAN 5c17:83ff:2255
*> 0 0 64 102:: :: 1000 5.5.5.5 5.5.5.5 VXLAN 5c17:83ff:2255
* 0 0 64 102:: :: 1000 5.5.5.5 4.4.4.4 VXLAN 5c17:83ff:2255
*> 0 0 64 202:: :: 1000 5.5.5.5 5.5.5.5 VXLAN 5c17:83ff:2255
* 0 0 64 202:: :: 1000 5.5.5.5 4.4.4.4 VXLAN 5c17:83ff:2255
BLEAF3#
BLEAF3#show evpn multi-homing domain-tracking-status
iESI Domain Tracking Status
===========================
iESI-configured VRFs : 10
Configured peer-GW VTEPs (BGP-pushed) : 16.16.16.16(DC,no tunnel),26.26.26.26(WAN,tunnel exists)
Resolved-transit tunnels (peer GW excluded):
DC : 2 => DC ACTIVE
WAN : 20 => WAN ACTIVE
Per-VRF iESI object state:
VRF Domain ESI Isolated Withdrawn Tenants Peer GW(s)
--------------------------------------------------------------------------------------------------------
L2_VRF1 DC 00:00:22:11:11:11:11:11:11:11 no no 1 -
L2_VRF1 WAN 00:00:22:11:11:11:11:11:11:11 no no 1 26.26.26.26
L2_VRF10 DC 00:00:22:99:11:11:11:11:11:11 no no 2 -
L2_VRF10 WAN 00:00:22:99:11:11:11:11:11:11 no no 2 26.26.26.26
L2_VRF2 DC 00:00:22:22:11:11:11:11:11:11 no no 1 -
L2_VRF2 WAN 00:00:22:22:11:11:11:11:11:11 no no 1 26.26.26.26
L2_VRF3 DC 00:00:22:33:11:11:11:11:11:11 no no 1 -
L2_VRF3 WAN 00:00:22:33:11:11:11:11:11:11 no no 1 26.26.26.26
L2_VRF4 DC 00:00:22:44:11:11:11:11:11:11 no no 1 -
L2_VRF4 WAN 00:00:22:44:11:11:11:11:11:11 no no 1 26.26.26.26
L2_VRF5 DC 00:00:22:55:11:11:11:11:11:11 no no 1 -
L2_VRF5 WAN 00:00:22:55:11:11:11:11:11:11 no no 1 26.26.26.26
L2_VRF6 DC 00:00:22:66:11:11:11:11:11:11 no no 1 -
L2_VRF6 WAN 00:00:22:66:11:11:11:11:11:11 no no 1 26.26.26.26
L2_VRF7 DC 00:00:22:77:11:11:11:11:11:11 no no 1 -
L2_VRF7 WAN 00:00:22:77:11:11:11:11:11:11 no no 1 26.26.26.26
L2_VRF8 DC 00:00:22:88:11:11:11:11:11:11 no no 1 -
L2_VRF8 WAN 00:00:22:88:11:11:11:11:11:11 no no 1 26.26.26.26
L2_VRF9 DC 00:00:22:99:11:11:11:11:11:11 no no 2 -
L2_VRF9 WAN 00:00:22:99:11:11:11:11:11:11 no no 2 26.26.26.26
BLEAF3#
=============================================
BLEAF4
=============================================
BLEAF4#show ip ospf neighbor
Total number of full neighbors: 4
OSPF process 100 VRF(default):
Neighbor ID Pri State Dead Time Address Interface Instance ID
9.9.9.9 1 Full/Backup 00:00:36 90.1.2.1 ce2 0
10.10.10.10 1 Full/Backup 00:00:33 100.1.2.1 ce3 0
17.17.17.17 1 Full/DR 00:00:38 106.1.1.2 xe10 0
18.18.18.18 1 Full/DR 00:00:38 106.1.2.2 xe11 0
BLEAF4#show bgp l2vpn evpn summary
BGP router identifier 16.16.16.16, local AS number 65002
BGP table version is 39
3 BGP AS-PATH entries
0 BGP community entries
Neighbor V AS MsgRcv MsgSen TblVer InQ OutQ Up/Down State/PfxRcd AD MACIP MCAST ESI PREFIX-ROUTE Desc
4.4.4.4 4 65003 298 205 39 0 0 00:24:04 210 22 162 20 0 6
5.5.5.5 4 65003 308 182 39 0 0 00:24:02 210 22 162 20 0 6
23.23.23.23 4 65002 172 132 39 0 0 00:22:05 260 19 231 10 0 0
24.24.24.24 4 65002 124 149 39 0 0 00:20:19 187 19 158 10 0 0
25.25.25.25 4 65002 134 165 39 0 0 00:23:49 38 19 0 10 9 0
Total number of neighbors 5
Total number of Established sessions 5
BLEAF4#show nvo vxlan
VXLAN Information
=================
Codes: NW - Network Port
AC - Access Port
(u) - Untagged
VNID VNI-Name VNI-Type Type Intr-VNID Interface ESI VLAN DF-Status Src-Addr Dst-Addr Router-Mac
_______________________________________________________________________________________________________________________________________________________________
1000 ---- L3 NW ---- ---- ---- ---- ---- 16.16.16.16 5.5.5.5 5c17.83ff.2255
1000 ---- L3 NW ---- ---- ---- ---- ---- 16.16.16.16 4.4.4.4 7c8d.9caa.5231
1001 ---- L2 NW 100001 ---- ---- ---- ---- 16.16.16.16 5.5.5.5 --------------
1001 ---- L2 NW 100001 ---- ---- ---- ---- 16.16.16.16 4.4.4.4 --------------
1001 ---- -- DC 100001 iESI 00:00:22:11:11:11:11:11:11:11 1001 N/A(DC) ---- ----
1002 ---- L2 NW 100002 ---- ---- ---- ---- 16.16.16.16 5.5.5.5 --------------
1002 ---- L2 NW 100002 ---- ---- ---- ---- 16.16.16.16 4.4.4.4 --------------
1002 ---- -- DC 100002 iESI 00:00:22:22:11:11:11:11:11:11 1002 N/A(DC) ---- ----
1003 ---- L2 NW 100003 ---- ---- ---- ---- 16.16.16.16 5.5.5.5 --------------
1003 ---- L2 NW 100003 ---- ---- ---- ---- 16.16.16.16 4.4.4.4 --------------
1003 ---- -- DC 100003 iESI 00:00:22:33:11:11:11:11:11:11 1003 N/A(DC) ---- ----
1004 ---- L2 NW 100004 ---- ---- ---- ---- 16.16.16.16 5.5.5.5 --------------
1004 ---- L2 NW 100004 ---- ---- ---- ---- 16.16.16.16 4.4.4.4 --------------
1004 ---- -- DC 100004 iESI 00:00:22:44:11:11:11:11:11:11 1004 N/A(DC) ---- ----
1005 ---- L2 NW 100005 ---- ---- ---- ---- 16.16.16.16 5.5.5.5 --------------
1005 ---- L2 NW 100005 ---- ---- ---- ---- 16.16.16.16 4.4.4.4 --------------
1005 ---- -- DC 100005 iESI 00:00:22:55:11:11:11:11:11:11 1005 N/A(DC) ---- ----
1006 ---- L2 NW 100006 ---- ---- ---- ---- 16.16.16.16 5.5.5.5 --------------
1006 ---- L2 NW 100006 ---- ---- ---- ---- 16.16.16.16 4.4.4.4 --------------
1006 ---- -- DC 100006 iESI 00:00:22:66:11:11:11:11:11:11 1006 N/A(DC) ---- ----
1007 ---- L2 NW 100007 ---- ---- ---- ---- 16.16.16.16 5.5.5.5 --------------
1007 ---- L2 NW 100007 ---- ---- ---- ---- 16.16.16.16 4.4.4.4 --------------
1007 ---- -- DC 100007 iESI 00:00:22:77:11:11:11:11:11:11 1007 N/A(DC) ---- ----
1008 ---- L2 NW 100008 ---- ---- ---- ---- 16.16.16.16 5.5.5.5 --------------
1008 ---- L2 NW 100008 ---- ---- ---- ---- 16.16.16.16 4.4.4.4 --------------
1008 ---- -- DC 100008 iESI 00:00:22:88:11:11:11:11:11:11 1008 N/A(DC) ---- ----
1009 ---- L2 NW 100009 ---- ---- ---- ---- 16.16.16.16 5.5.5.5 --------------
1009 ---- L2 NW 100009 ---- ---- ---- ---- 16.16.16.16 4.4.4.4 --------------
1009 ---- -- DC 100009 iESI 00:00:22:99:11:11:11:11:11:11 1009 N/A(DC) ---- ----
1010 ---- L2 NW 100010 ---- ---- ---- ---- 16.16.16.16 5.5.5.5 --------------
1010 ---- L2 NW 100010 ---- ---- ---- ---- 16.16.16.16 4.4.4.4 --------------
1010 ---- -- DC 100010 iESI 00:00:22:99:11:11:11:11:11:11 1010 N/A(DC) ---- ----
Total number of entries are 32
Note: Refer sub-interface config for VLAN information.
BLEAF4#show nvo vxlan tunnel
VXLAN Network tunnel Entries
Source Destination Status Up/Down Update
========================================================================
16.16.16.16 5.5.5.5 Installed 00:24:00 00:24:00
16.16.16.16 4.4.4.4 Installed 00:24:03 00:24:03
Total number of entries are 2
BLEAF4#show nvo vxlan access-if brief
Inner Admin Link
Interface Vlan vlan Ifindex Vnid status status
---------------------------------------------------------------
Total number of entries are 0
Note: Refer sub-interface config for VLAN information.
BLEAF4#show etherchannel summary
BLEAF4#show ip route vrf L3_VRF1
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2,
ia - IS-IS inter area, E - EVPN,
v - vrf leaked, g - imported from global
* - candidate default
IP Route Table for VRF "L3_VRF1"
B 4.4.4.4/32 [0/0] is directly connected, tunvxlan2, installed 00:24:02, last update 00:24:02 ago
B 5.5.5.5/32 [0/0] is directly connected, tunvxlan2, installed 00:24:00, last update 00:24:00 ago
B 102.101.1.0/24 [20/0] via 4.4.4.4 (recursive is directly connected, tunvxlan2), installed 00:24:02, last update 00:24:02 ago
C 127.0.0.0/8 is directly connected, lo.L3_VRF1, installed 00:26:02, last update 00:26:02 ago
B 202.101.1.0/24 [20/0] via 5.5.5.5 (recursive is directly connected, tunvxlan2), installed 00:24:00, last update 00:24:00 ago
Gateway of last resort is not set
BLEAF4#show ipv6 route vrf L3_VRF1
IPv6 Routing Table
Codes: K - kernel route, C - connected, S - static, D- DHCP, R - RIP,
O - OSPF, IA - OSPF inter area, E1 - OSPF external type 1,
E2 - OSPF external type 2, E - EVPN N1 - OSPF NSSA external type 1,
N2 - OSPF NSSA external type 2, i - IS-IS, B - BGP,
P - SRV6-POLICY,
v - vrf leaked, g - imported from global
Timers: Uptime
IP Route Table for VRF "L3_VRF1"
C ::1/128 via ::, lo.L3_VRF1, installed 00:26:02, last update 00:26:02 ago
B ::ffff:404:404/128 [0/0] via ::, tunvxlan2, installed 00:24:02, last update 00:24:02 ago
B ::ffff:505:505/128 [0/0] via ::, tunvxlan2, installed 00:24:00, last update 00:24:00 ago
B 102::/64 [20/0] via ::ffff:404:404 (recursive via ::, tunvxlan2), installed 00:24:02, last update 00:24:02 ago
B 202::/64 [20/0] via ::ffff:505:505 (recursive via ::, tunvxlan2), installed 00:24:00, last update 00:24:00 ago
C fe80::/64 via ::, tunvxlan2, installed 00:26:02, last update 00:26:02 ago
BLEAF4#show ip route vrf L3_VRF1 database
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2,
ia - IS-IS inter area, E - EVPN,
v - vrf leaked, g - imported from global
> - selected route, * - FIB route, p - stale info
IP Route Table for VRF "L3_VRF1"
B *> 4.4.4.4/32 [0/0] is directly connected, tunvxlan2, installed 00:24:02, last update 00:24:02 ago
B *> 5.5.5.5/32 [0/0] is directly connected, tunvxlan2, installed 00:24:00, last update 00:24:00 ago
B > 101.101.1.0/24 [200/0] via 24.24.24.24, installed 00:21:59, last update 00:20:13 ago
> [200/0] via 23.23.23.23
B *> 102.101.1.0/24 [20/0] via 4.4.4.4 (recursive is directly connected, tunvxlan2), installed 00:24:02, last update 00:24:02 ago
C *> 127.0.0.0/8 is directly connected, lo.L3_VRF1, installed 00:26:02, last update 00:26:02 ago
B > 201.101.1.0/24 [200/0] via 24.24.24.24, installed 00:21:59, last update 00:20:13 ago
> [200/0] via 23.23.23.23
B *> 202.101.1.0/24 [20/0] via 5.5.5.5 (recursive is directly connected, tunvxlan2), installed 00:24:00, last update 00:24:00 ago
Total number of IPv4 routes 9
Gateway of last resort is not set
BLEAF4#show ipv6 route vrf L3_VRF1 database
IPv6 Routing Table
Codes: K - kernel route, C - connected, S - static, D- DHCP, R - RIP,
O - OSPF, IA - OSPF inter area, E1 - OSPF external type 1,
E2 - OSPF external type 2, E - EVPN N1 - OSPF NSSA external type 1,
N2 - OSPF NSSA external type 2, i - IS-IS, B - BGP,
P - SRV6-POLICY,
v - vrf leaked, g - imported from global
> - selected route, * - FIB route,p - stale info
Timers: Uptime
IP Route Table for VRF "L3_VRF1"
C *> ::1/128 via ::, lo.L3_VRF1, installed 00:26:02, last update 00:26:02 ago
B *> ::ffff:404:404/128 [0/0] via ::, tunvxlan2, installed 00:24:02, last update 00:24:02 ago
B *> ::ffff:505:505/128 [0/0] via ::, tunvxlan2, installed 00:24:00, last update 00:24:00 ago
B > 101::/64 [200/0] via ::ffff:24.24.24.24, installed 00:21:59, last update 00:20:13 ago
> [200/0] via ::ffff:23.23.23.23
B *> 102::/64 [20/0] via ::ffff:404:404 (recursive via ::, tunvxlan2), installed 00:24:02, last update 00:24:02 ago
B > 201::/64 [200/0] via ::ffff:24.24.24.24, installed 00:21:59, last update 00:20:13 ago
> [200/0] via ::ffff:23.23.23.23
B *> 202::/64 [20/0] via ::ffff:505:505 (recursive via ::, tunvxlan2), installed 00:24:00, last update 00:24:00 ago
C *> fe80::/64 via ::, tunvxlan2, installed 00:26:02, last update 00:26:02 ago
Total number of IPv6 routes 10
BLEAF4#show ip bgp vpnv4 all
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal, l - labeled
S Stale, x-EVPN, w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path Ext-Color
Route Distinguisher: 13.13.13.13:951
*>iw 101.101.1.0/24 23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
*>iw 201.101.1.0/24 23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
Route Distinguisher: 14.14.14.14:951
*>iw 101.101.1.0/24 24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
*>iw 201.101.1.0/24 24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
Route Distinguisher: 16.16.16.16:101 (Default for VRF L3_VRF1)
*>iw 101.101.1.0/24 23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
* iw 24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
*>x l 102.101.1.0/24 4.4.4.4 0 100 0 65003 ? -
* x 5.5.5.5 0 100 0 65003 ? -
*>iw 201.101.1.0/24 23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
* iw 24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
*>x l 202.101.1.0/24 5.5.5.5 0 100 0 65003 ? -
VRF Origin Route count = 0
Accepted routes count = 7
BLEAF4#show ip bgp vpnv6 all
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal, l - labeled
S Stale, x-EVPN, w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path Ext-Color
Route Distinguisher: 13.13.13.13:951
*>iw 101::/64 ::ffff:23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
*>iw 201::/64 ::ffff:23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
Route Distinguisher: 14.14.14.14:951
*>iw 101::/64 ::ffff:24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
*>iw 201::/64 ::ffff:24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
VRF Origin Route count = 0
Accepted routes count = 2
Route Distinguisher: 16.16.16.16:101 (Default for VRF L3_VRF1)
*>iw 101::/64 ::ffff:23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
*aiw ::ffff:24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
*>x l 102::/64 ::ffff:4.4.4.4 0 100 0 65003 ? -
* x ::ffff:5.5.5.5 0 100 0 65003 ? -
*>iw 201::/64 ::ffff:23.23.23.23 0 100 0 65001 ? 2324:24:70(evpn) -
*aiw ::ffff:24.24.24.24 0 100 0 65001 ? 2324:24:70(evpn) -
*>x l 202::/64 ::ffff:5.5.5.5 0 100 0 65003 ? -
VRF Origin Route count = 0
Accepted routes count = 7
BLEAF4#show evpn mpls
EVPN-MPLS Information
=================
Codes: NW - Network Port
AC - Access Port
CW - Control Word
(u) - Untagged
VPN-ID EVI-Name CW EVI-Type Type Intr-VNID Interface ESI VLAN DF-Status Src-Addr Dst-Addr
___________________________________________________________________________________________________________________________________________
100001 ---- --- L2 NW 1001 ---- ---- ---- ---- 26.26.26.26 23.23.23.23
100001 ---- --- L2 NW 1001 ---- ---- ---- ---- 26.26.26.26 25.25.25.25
100001 ---- --- L2 NW 1001 ---- ---- ---- ---- 26.26.26.26 24.24.24.24
100001 ---- No -- WAN 1001 iESI 00:00:22:11:11:11:11:11:11:11 100001 DF ---- ----
100002 ---- --- L2 NW 1002 ---- ---- ---- ---- 26.26.26.26 23.23.23.23
100002 ---- --- L2 NW 1002 ---- ---- ---- ---- 26.26.26.26 25.25.25.25
100002 ---- --- L2 NW 1002 ---- ---- ---- ---- 26.26.26.26 24.24.24.24
100002 ---- No -- WAN 1002 iESI 00:00:22:22:11:11:11:11:11:11 100002 NDF ---- ----
100003 ---- --- L2 NW 1003 ---- ---- ---- ---- 26.26.26.26 23.23.23.23
100003 ---- --- L2 NW 1003 ---- ---- ---- ---- 26.26.26.26 25.25.25.25
100003 ---- --- L2 NW 1003 ---- ---- ---- ---- 26.26.26.26 24.24.24.24
100003 ---- No -- WAN 1003 iESI 00:00:22:33:11:11:11:11:11:11 100003 DF ---- ----
100004 ---- --- L2 NW 1004 ---- ---- ---- ---- 26.26.26.26 23.23.23.23
100004 ---- --- L2 NW 1004 ---- ---- ---- ---- 26.26.26.26 25.25.25.25
100004 ---- --- L2 NW 1004 ---- ---- ---- ---- 26.26.26.26 24.24.24.24
100004 ---- No -- WAN 1004 iESI 00:00:22:44:11:11:11:11:11:11 100004 NDF ---- ----
100005 ---- --- L2 NW 1005 ---- ---- ---- ---- 26.26.26.26 23.23.23.23
100005 ---- --- L2 NW 1005 ---- ---- ---- ---- 26.26.26.26 25.25.25.25
100005 ---- --- L2 NW 1005 ---- ---- ---- ---- 26.26.26.26 24.24.24.24
100005 ---- Yes -- WAN 1005 iESI 00:00:22:55:11:11:11:11:11:11 100005 DF ---- ----
100006 ---- --- L2 NW 1006 ---- ---- ---- ---- 26.26.26.26 23.23.23.23
100006 ---- --- L2 NW 1006 ---- ---- ---- ---- 26.26.26.26 25.25.25.25
100006 ---- --- L2 NW 1006 ---- ---- ---- ---- 26.26.26.26 24.24.24.24
100006 ---- No -- WAN 1006 iESI 00:00:22:66:11:11:11:11:11:11 100006 NDF ---- ----
100007 ---- --- L2 NW 1007 ---- ---- ---- ---- 26.26.26.26 23.23.23.23
100007 ---- --- L2 NW 1007 ---- ---- ---- ---- 26.26.26.26 25.25.25.25
100007 ---- --- L2 NW 1007 ---- ---- ---- ---- 26.26.26.26 24.24.24.24
100007 ---- No -- WAN 1007 iESI 00:00:22:77:11:11:11:11:11:11 100007 DF ---- ----
100008 ---- --- L2 NW 1008 ---- ---- ---- ---- 26.26.26.26 23.23.23.23
100008 ---- --- L2 NW 1008 ---- ---- ---- ---- 26.26.26.26 25.25.25.25
100008 ---- --- L2 NW 1008 ---- ---- ---- ---- 26.26.26.26 24.24.24.24
100008 ---- Yes -- WAN 1008 iESI 00:00:22:88:11:11:11:11:11:11 100008 NDF ---- ----
100009 ---- --- L2 NW 1009 ---- ---- ---- ---- 26.26.26.26 23.23.23.23
100009 ---- --- L2 NW 1009 ---- ---- ---- ---- 26.26.26.26 25.25.25.25
100009 ---- --- L2 NW 1009 ---- ---- ---- ---- 26.26.26.26 24.24.24.24
100009 ---- No -- WAN 1009 iESI 00:00:22:99:11:11:11:11:11:11 100009 DF ---- ----
100010 ---- --- L2 NW 1010 ---- ---- ---- ---- 26.26.26.26 23.23.23.23
100010 ---- --- L2 NW 1010 ---- ---- ---- ---- 26.26.26.26 25.25.25.25
100010 ---- --- L2 NW 1010 ---- ---- ---- ---- 26.26.26.26 24.24.24.24
100010 ---- No -- WAN 1010 iESI 00:00:22:99:11:11:11:11:11:11 100010 NDF ---- ----
Total number of entries are 40
Note: Refer sub-interface config for VLAN information.
BLEAF4#show evpn mpls tunnel
EVPN-MPLS Network tunnel Entries
Source Destination Status Up/Down Update evpn-id Local-Leaf Remote-Leaf Ext-Color FAT CW
========================================================================================================================================
26.26.26.26 23.23.23.23 Installed 00:22:04 00:22:04 100010 --- --- --- --- No
26.26.26.26 23.23.23.23 Installed 00:22:04 00:22:04 100009 --- --- --- --- No
26.26.26.26 23.23.23.23 Installed 00:22:04 00:22:04 100008 --- --- --- set Yes
26.26.26.26 23.23.23.23 Installed 00:22:04 00:22:04 100007 --- --- --- set No
26.26.26.26 23.23.23.23 Installed 00:22:04 00:22:04 100006 --- --- --- --- No
26.26.26.26 23.23.23.23 Installed 00:22:04 00:22:04 100005 --- --- --- --- Yes
26.26.26.26 23.23.23.23 Installed 00:22:04 00:22:04 100004 --- --- --- --- No
26.26.26.26 23.23.23.23 Installed 00:22:04 00:22:04 100003 --- --- --- --- No
26.26.26.26 23.23.23.23 Installed 00:22:04 00:22:04 100002 --- --- --- --- No
26.26.26.26 23.23.23.23 Installed 00:22:04 00:22:04 100001 --- --- --- --- No
26.26.26.26 25.25.25.25 Installed 00:23:49 00:23:49 100010 --- --- --- --- No
26.26.26.26 25.25.25.25 Installed 00:23:49 00:23:49 100009 --- --- --- --- No
26.26.26.26 25.25.25.25 Installed 00:23:49 00:23:49 100008 --- --- --- set Yes
26.26.26.26 25.25.25.25 Installed 00:23:49 00:23:49 100007 --- --- --- set No
26.26.26.26 25.25.25.25 Installed 00:23:49 00:23:49 100006 --- --- --- --- No
26.26.26.26 25.25.25.25 Installed 00:23:49 00:23:49 100005 --- --- --- --- Yes
26.26.26.26 25.25.25.25 Installed 00:23:49 00:23:49 100004 --- --- --- --- No
26.26.26.26 25.25.25.25 Installed 00:23:49 00:23:49 100003 --- --- --- --- No
26.26.26.26 25.25.25.25 Installed 00:23:49 00:23:49 100002 --- --- --- --- No
26.26.26.26 25.25.25.25 Installed 00:23:49 00:23:49 100001 --- --- --- --- No
26.26.26.26 24.24.24.24 Installed 00:20:19 00:20:19 100010 --- --- --- --- No
26.26.26.26 24.24.24.24 Installed 00:20:19 00:20:19 100009 --- --- --- --- No
26.26.26.26 24.24.24.24 Installed 00:20:19 00:20:19 100008 --- --- --- set Yes
26.26.26.26 24.24.24.24 Installed 00:20:19 00:20:19 100007 --- --- --- set No
26.26.26.26 24.24.24.24 Installed 00:20:19 00:20:19 100006 --- --- --- --- No
26.26.26.26 24.24.24.24 Installed 00:20:19 00:20:19 100005 --- --- --- --- Yes
26.26.26.26 24.24.24.24 Installed 00:20:19 00:20:19 100004 --- --- --- --- No
26.26.26.26 24.24.24.24 Installed 00:20:19 00:20:19 100003 --- --- --- --- No
26.26.26.26 24.24.24.24 Installed 00:20:19 00:20:19 100002 --- --- --- --- No
26.26.26.26 24.24.24.24 Installed 00:20:19 00:20:19 100001 --- --- --- --- No
Total number of entries are 30
BLEAF4#show evpn mpls access-if brief
Inner Admin Link
Interface Vlan vlan Ifindex Vnid status status
---------------------------------------------------------------
Total number of entries are 0
Note: Refer sub-interface config for VLAN information.
BLEAF4#show ldp session
Codes: m - MD5 password is not set/unset.
g - GR configuration not set/unset.
t - TCP MSS not set/unset.
Session has to be cleared manually
Code Peer IP Address IF Name My Role State KeepAlive UpTime AutoCreate
15.15.15.15 ce3 Active OPERATIONAL 30 00:23:34 No
17.17.17.17 xe10 Passive OPERATIONAL 30 00:24:19 No
18.18.18.18 xe11 Passive OPERATIONAL 30 00:24:19 No
BLEAF4#show mpls forwarding-table
Codes: > - installed FTN, * - selected FTN, p - stale FTN, ! - using backup
B - BGP FTN, K - CLI FTN, (t) - tunnel, P - SR Policy FTN, (b) - bypass,
L - LDP FTN, R - RSVP-TE FTN, S - SNMP FTN, I - IGP-Shortcut,
U - unknown FTN, O - SR-OSPF FTN, i - SR-ISIS FTN, k - SR-CLI FTN
(m) - FTN mapped over multipath transport, (e) - FTN is ECMP
FTN-ECMP LDP: Disabled, SR: Disabled
Code FEC FTN-ID Nhlfe-ID Tunnel-ID Pri Out-Label Out-Intf ELC Nexthop Algo-Num UpTime
L> 17.17.17.17/32 1 2 - - - - - - N/A 00:24:19
1 - Yes 3 xe10 No 106.1.1.2 - -
L> 18.18.18.18/32 3 5 - - - - - - N/A 00:24:15
4 - Yes 3 xe11 No 106.1.2.2 - -
L> 23.23.23.23/32 8 13 - - - - - - N/A 00:22:11
12 - Yes 24340 xe11 No 106.1.2.2 - -
15 - Yes 24340 xe10 No 106.1.1.2 - -
L> 24.24.24.24/32 17 34 - - - - - - N/A 00:20:23
33 - Yes 24356 xe11 No 106.1.2.2 - -
30 - Yes 24356 xe10 No 106.1.1.2 - -
L> 25.25.25.25/32 5 9 - - - - - - N/A 00:23:54
7 - Yes 24337 xe11 No 106.1.2.2 - -
8 - Yes 24337 xe10 No 106.1.1.2 - -
L> 103.1.1.0/24 6 2 - - - - - - N/A 00:22:56
1 - Yes 3 xe10 No 106.1.1.2 - -
L> 103.1.2.0/24 7 5 - - - - - - N/A 00:22:56
4 - Yes 3 xe11 No 106.1.2.2 - -
L> 104.1.1.0/24 16 28 - - - - - - N/A 00:21:09
27 - Yes 24355 xe10 No 106.1.1.2 - -
L> 104.1.2.0/24 15 25 - - - - - - N/A 00:21:09
24 - Yes 24355 xe11 No 106.1.2.2 - -
L> 105.1.1.0/24 2 2 - - - - - - N/A 00:24:19
1 - Yes 3 xe10 No 106.1.1.2 - -
L> 105.1.2.0/24 4 5 - - - - - - N/A 00:24:15
4 - Yes 3 xe11 No 106.1.2.2 - -
BLEAF4#
BLEAF4#show bgp l2vpn evpn prefix-route
BGP table version is 39, local router ID is 16.16.16.16
Status codes: s suppressed, d damped, h history, a add-path, b back-up, * valid, > best, i - internal,
l - labeled, S Stale w-WAN-routes
Origin codes: i - IGP, e - EGP, ? - incomplete
Description : Ext-Color - Extended community color
RD[4.4.4.4:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 102.101.1.0 0.0.0.0 1000 4.4.4.4 4.4.4.4 VXLAN 7c8d:9caa:5231
* 0 0 24 102.101.1.0 0.0.0.0 1000 4.4.4.4 5.5.5.5 VXLAN 7c8d:9caa:5231
*> 0 0 64 102:: :: 1000 4.4.4.4 4.4.4.4 VXLAN 7c8d:9caa:5231
* 0 0 64 102:: :: 1000 4.4.4.4 5.5.5.5 VXLAN 7c8d:9caa:5231
RD[5.5.5.5:101]
ESI Eth-Tag Prefix-Length IP-Address GW-IPAddress L3VNID/LABEL Nexthop Peer Encap Router-Mac D-path
*> 0 0 24 102.101.1.0 0.0.0.0 1000 5.5.5.5 5.5.5.5 VXLAN 5c17:83ff:2255
* 0 0 24 102.101.1.0 0.0.0.0 1000 5.5.5.5 4.4.4.4 VXLAN 5c17:83ff:2255
*> 0 0 24 202.101.1.0 0.0.0.0 1000 5.5.5.5 5.5.5.5 VXLAN 5c17:83ff:2255
* 0 0 24 202.101.1.0 0.0.0.0 1000 5.5.5.5 4.4.4.4 VXLAN 5c17:83ff:2255
*> 0 0 64 102:: :: 1000 5.5.5.5 5.5.5.5 VXLAN 5c17:83ff:2255
* 0 0 64 102:: :: 1000 5.5.5.5 4.4.4.4 VXLAN 5c17:83ff:2255
*> 0 0 64 202:: :: 1000 5.5.5.5 5.5.5.5 VXLAN 5c17:83ff:2255
* 0 0 64 202:: :: 1000 5.5.5.5 4.4.4.4 VXLAN 5c17:83ff:2255
BLEAF4#
BLEAF4#show evpn multi-homing domain-tracking-status
iESI Domain Tracking Status
===========================
iESI-configured VRFs : 10
Configured peer-GW VTEPs (BGP-pushed) : 15.15.15.15(DC,no tunnel),25.25.25.25(WAN,tunnel exists)
Resolved-transit tunnels (peer GW excluded):
DC : 2 => DC ACTIVE
WAN : 20 => WAN ACTIVE
Per-VRF iESI object state:
VRF Domain ESI Isolated Withdrawn Tenants Peer GW(s)
--------------------------------------------------------------------------------------------------------
L2_VRF1 DC 00:00:22:11:11:11:11:11:11:11 no no 1 -
L2_VRF1 WAN 00:00:22:11:11:11:11:11:11:11 no no 1 25.25.25.25
L2_VRF10 DC 00:00:22:99:11:11:11:11:11:11 no no 2 -
L2_VRF10 WAN 00:00:22:99:11:11:11:11:11:11 no no 2 25.25.25.25
L2_VRF2 DC 00:00:22:22:11:11:11:11:11:11 no no 1 -
L2_VRF2 WAN 00:00:22:22:11:11:11:11:11:11 no no 1 25.25.25.25
L2_VRF3 DC 00:00:22:33:11:11:11:11:11:11 no no 1 -
L2_VRF3 WAN 00:00:22:33:11:11:11:11:11:11 no no 1 25.25.25.25
L2_VRF4 DC 00:00:22:44:11:11:11:11:11:11 no no 1 -
L2_VRF4 WAN 00:00:22:44:11:11:11:11:11:11 no no 1 25.25.25.25
L2_VRF5 DC 00:00:22:55:11:11:11:11:11:11 no no 1 -
L2_VRF5 WAN 00:00:22:55:11:11:11:11:11:11 no no 1 25.25.25.25
L2_VRF6 DC 00:00:22:66:11:11:11:11:11:11 no no 1 -
L2_VRF6 WAN 00:00:22:66:11:11:11:11:11:11 no no 1 25.25.25.25
L2_VRF7 DC 00:00:22:77:11:11:11:11:11:11 no no 1 -
L2_VRF7 WAN 00:00:22:77:11:11:11:11:11:11 no no 1 25.25.25.25
L2_VRF8 DC 00:00:22:88:11:11:11:11:11:11 no no 1 -
L2_VRF8 WAN 00:00:22:88:11:11:11:11:11:11 no no 1 25.25.25.25
L2_VRF9 DC 00:00:22:99:11:11:11:11:11:11 no no 2 -
L2_VRF9 WAN 00:00:22:99:11:11:11:11:11:11 no no 2 25.25.25.25
BLEAF4#
=============================================
SPINE1
=============================================
SPINE1#show ip ospf neighbor
Total number of full neighbors: 4
OSPF process 100 VRF(default):
Neighbor ID Pri State Dead Time Address Interface Instance ID
1.1.1.1 1 Full/Backup 00:00:33 10.1.1.1 ce2/1 0
2.2.2.2 1 Full/Backup 00:00:34 20.1.1.1 ce1/2 0
13.13.13.13 1 Full/DR 00:00:31 101.1.1.2 ce3/1 0
14.14.14.14 1 Full/DR 00:00:36 101.1.2.2 ce21/1 0
SPINE1#
=============================================
SPINE2
=============================================
SPINE2#show ip ospf neighbor
Total number of full neighbors: 4
OSPF process 100 VRF(default):
Neighbor ID Pri State Dead Time Address Interface Instance ID
1.1.1.1 1 Full/Backup 00:00:28 10.1.2.1 ce1/1 0
2.2.2.2 1 Full/Backup 00:00:38 20.1.2.1 ce2/1 0
13.13.13.13 1 Full/DR 00:00:29 102.1.1.2 ce3/1 0
14.14.14.14 1 Full/DR 00:00:32 102.1.2.2 ce4/1 0
SPINE2#
=============================================
SPINE4
=============================================
SPINE4#show ip ospf neighbor
Total number of full neighbors: 4
OSPF process 100 VRF(default):
Neighbor ID Pri State Dead Time Address Interface Instance ID
4.4.4.4 1 Full/Backup 00:00:32 40.1.1.1 xe31/1 0
5.5.5.5 1 Full/Backup 00:00:32 50.1.1.1 xe1/1 0
15.15.15.15 1 Full/DR 00:00:37 90.1.1.2 ce27 0
16.16.16.16 1 Full/DR 00:00:34 90.1.2.2 ce25 0
SPINE4#
=============================================
SPINE5
=============================================
SPINE5#show ip ospf neighbor
Total number of full neighbors: 4
OSPF process 100 VRF(default):
Neighbor ID Pri State Dead Time Address Interface Instance ID
4.4.4.4 1 Full/Backup 00:00:37 40.1.2.1 xe31/1 0
5.5.5.5 1 Full/Backup 00:00:37 50.1.2.1 xe1/1 0
15.15.15.15 1 Full/DR 00:00:39 100.1.1.2 ce27 0
16.16.16.16 1 Full/DR 00:00:29 100.1.2.2 ce25 0
SPINE5#
Interconnecting EVPN VXLAN to MPLS Commands
The following commands are introduced as part of the EVPN VXLAN to MPLS Interconnecting.
arp-nd-cache disable
Use this command to disable the proxy for ARP and ND packets received over tunnel interfaces within an EVPN stitching MAC-VRF on the BGW.
Note: Disabling arp-nd-cache on the BGW does not flush the existing ARP and ND cache.
Use the no parameter of this command to re-enable the ARP and ND cache.
Command Syntax
arp-nd-cache disable
no arp-nd-cache disable
Parameters
None.
Default
Enabled
Command Mode
MAC VRF Stitching Mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for disabling the ARP and ND caching caching under EVPN stitching mode.
OcNOS# configure terminal
OcNOS(config)# mac vrf MAC_VRF1
OcNOS(config-vrf)# evpn stitching
OcNOS(config-vrf-evpn)# arp-nd-cache disable
bgp bestpath domain-path-id
Use this command to include the BGP Domain Path (D-PATH) attribute in the BGP best-path selection algorithm. When enabled, BGP evaluates the length of the D-PATH attribute during route selection and prefers the path with the shortest D-PATH length when all preceding path selection criteria (such as Weight, Local Preference, AIGP, AS-Path, and Origin) are equal.
Note: Updating the domain-path attribute dynamically requires a manual BGP session reset to apply changes. After modifying the configuration, execute the following command to re-advertise your routes with the updated domain-path attribute: clear ip bgp all *.
Use the no parameter of this command to exclude the D-PATH attribute from the BGP best-path calculation.
Command Syntax
bgp bestpath domain-path-id
no bgp bestpath domain-path-id
Parameters
None
Default
Disabled
Command Mode
Router Mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for enabling D-PATH in BGP best-path selection.
OcNOS# configure terminal
OcNOS(config)# router bgp 65000
OcNOS(config-router)# bgp bestpath domain-path-id
OcNOS(config-router)# commit
OcNOS(config-router)# exit
bgp domain-path-id
Use this command to configure d-path attribute.
Note:
• Global Domain ID support across all three Subsequent Address Family Identifiers (SAFIs) (EVPN, IPv4/IPv6 IPVPN, and Local).
• Updating the domain-path attribute dynamically requires a manual BGP session reset to apply changes. After modifying the configuration, execute the following command to re-advertise your routes with the updated domain-path attribute: clear ip bgp all *.
Use the no parameter of this command to remove the domain path identifier.
Command Syntax
bgp domain-path-id (all|evpn|local)
no bgp domain-path-id
Parameters
all
Applies the Domain Path (D-PATH) identifier attribute across all stitched route types/domains (formatted as <Global:Local>, e.g., 65000:100).
evpn
Applies the Domain Path (D-PATH) identifier attribute specifically to EVPN routes.
local
Restricts the Domain Path (D-PATH) identifier generation and matching to the local domain.
Default
None
Command Mode
Router Mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for configuring a domain path identifier for IPVPN routes.
OcNOS(config)#router bgp
OcNOS(config-router)#bgp domain-path-id all 2325:25
OcNOS(config-router)#bgp domain-path-id ipvpn 2323:23
OcNOS(config-router)#bgp domain-path-id evpn 2324:24
OcNOS(config-router)#bgp domain-path-id local 2325:25
domain-path-id
Use this command to configure the BGP Domain Path (D-PATH) attribute identifier for IPVPN routes under an IP-VRF interconnecting block.
Note:
• Per-tenant (IP-VRF) Domain ID supports under the evpn stitching block to enable inter-VRF route leaking.
• Updating the domain-path attribute dynamically requires a manual BGP session reset to apply changes. After modifying the configuration, execute the following command to re-advertise your routes with the updated domain-path attribute: clear ip bgp all *.
Use the no parameter of this command to remove the domain path identifier.
Command Syntax
domain-path-id (ipvpn <AS_or_IP-address_Router-ID_or_Domain-ID:VRF-ID_or_Gateway-ID> | all | local | evpn |)
no domain-path-id
Parameters
AS_or_IP-address_Router-ID_or_Domain-ID:VRF-ID_or_Gateway-ID
Specifies the 6-byte domain path identifier formatted as Global:Local (e.g., 65000:100)
AS: A 2-byte or 4-byte: ASN (e.g., 65001 or 4200000001) representing the BGP Autonomous System of the domain.
Domain-ID: A unique integer assigned to identify a specific routing domain within an enterprise or service provider network.
VRF-ID: An integer index representing the Virtual Routing and Forwarding (VRF) instance on the gateway router.
Gateway-ID: A unique numerical ID representing the border gateway node performing the route re-advertisement/stitching.
Default
None
Command Mode
VRF Stitching Mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for configuring a domain path identifier for IPVPN routes.
OcNOS# configure terminal
OcNOS(config)# ip vrf
OcNOS(config-vrf)# evpn stitching
OcNOS(config-vrf-evpn)# domain-path-id ipvpn 65000:100
OcNOS(config-vrf-evpn)# domain-path-id evpn 2324:24
OcNOS(config-vrf-evpn)# domain-path-id local 2325:25
OcNOS(config-vrf-evpn)# domain-path-id all 2325:25
encapsulation
Use this command to specify the WAN domain encapsulation type for an EVPN interconnecting instance.
Use the no parameter of this command to reset the encapsulation type to default and also remove the iESI.
Command Syntax
encapsulation (vxlan | mpls)
no encapsulation
Parameters
vxlan
Specifies Virtual Extensible LAN (VXLAN) encapsulation for the WAN domain.
mpls
Specifies Multiprotocol Label Switching (MPLS) encapsulation for the WAN domain.
Default
vxlan
Command Mode
VRF Stitching Mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for setting WAN domain encapsulation to MPLS.
OcNOS# configure terminal
OcNOS(config)# mac vrf MAC_VRF1
OcNOS(config-vrf)# evpn stitching
OcNOS(config-vrf-evpn)# encapsulation mpls
evpn interconnect-mh gw-vtep-ip
Use this command to configure gateway VTEP IP addresses for EVPN interconnect multihoming across VXLAN and MPLS domains.
Note:
• The evpn interconnect-mh gw-vtep-ip command is mandatory for EVPN Interconnect Multihoming. Executing no evpn interconnect-mh gw-vtep-ip displays a warning prompt. Removing this command while interconnect multihoming is active results in unpredictable multihoming behavior, including traffic flooding/duplication, forwarding loops, and console warning/error messages. This configuration must remain active for the entire duration of interconnecting multihoming operation.
• Configure evpn interconnect-mh gw-vtep-ip first, before configuring any other multihoming-related settings (such as global multihoming enables evpn vxlan multihoming enable / evpn mpls multihoming enable or multi-homed iesi). If this command is configured after other multihoming settings are already applied, you must execute clear ip bgp * (or trigger a BGP route refresh) so that already-learned peer-GW routes are correctly reclassified into their respective DC and WAN domains.
Use the no parameter of this command to remove configured gateway VTEP IP addresses.
Command Syntax
evpn interconnect-mh gw-vtep-ip vxlan <A.B.C.D> mpls <A.B.C.D> (all|evpn|local)
no evpn interconnect-mh gw-vtep-ip vxlan
Parameters
vxlan <A.B.C.D>
Specifies the peer gateway VTEP IP address in the EVPN-VXLAN data center domain.
mpls <A.B.C.D>
Specifies the peer gateway VTEP/endpoint IP address in the EVPN-MPLS WAN domain.
Default
None
Command Mode
Config Mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for configuring peer gateway VTEP IP addresses for multihoming.
OcNOS# configure terminal
OcNOS(config)# evpn interconnect-mh gw-vtep-ip vxlan 1.1.1.1 mpls 10.10.10.10
evpn stitching
Use this command to enable EVPN stitching mode under a MAC-VRF or IP-VRF instance.
Use the no parameter of this command to remove the EVPN stitching configuration block.
Command Syntax
evpn stitching
no evpn stitching
Parameters
None
Default
None
Command Mode
VRF Stitching Mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for enabling EVPN stitching configuration mode under a VRF instance.
OcNOS# configure terminal
OcNOS(config)# ip vrf VRF1
OcNOS(config-vrf)# evpn stitching
OcNOS(config-vrf-evpn)#
hardware-profile filter evpn-stitch
Use this command to enable or disable the hardware profile filter for EVPN stitching functionality.
Command Syntax
hardware-profile filter evpn-stitch (disable | enable)
Parameters
enable
Enables the hardware profile filter group for EVPN stitching.
disable
Disables the hardware profile filter group for EVPN stitching.
Default
Disabled
Command Mode
Config mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for enabling the EVPN stitching hardware profile filter.
OcNOS# configure terminal
OcNOS(config)# hardware-profile filter evpn-stitch enable
host-route-extend-l2vni
Use this command to specify Layer-2 VNIs whose host routes are extended and re-advertised as Type-5 routes toward the DCI domain.
The iESI can be the same or different across MAC-VRFs; using the same iESI is recommended for scalability and simpler operations. (Note: it must still be unique per MAC‑VRF where distinct segments are intended.)
Each DC site's gateways must use an iESI distinct from the remote site's — the value identifies the site.
Use the no parameter of this command to remove host-route extension policies.
Command Syntax
host-route-extend-l2vni <VNI_LIST | all>
no host-route-extend-l2vni
Parameters
VNI_LIST
Specifies a single VNI or range of Layer-2 VNIs (For example, 10000-10050).
all
Specifies all configured Layer-2 VNIs for host-route extension.
Default
None
Command Mode
VRF Stitching Mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for extending host routes for a specific VNI range.
OcNOS# configure terminal
OcNOS(config)# ip vrf VRF1
OcNOS(config-vrf)# evpn stitching
OcNOS(config-vrf-evpn)# host-route-extend-l2vni 10000-10050
multi-homed iesi
Use this command to configure the Interconnect Ethernet Segment Identifier (iESI) for All-Active multihoming across Border Gateways.
Use the no parameter of this command to remove the iESI configuration.
Command Syntax
multi-homed iesi XX:XX:XX:XX:XX:XX:XX:XX:XX all-active
no multi-homed iesi
Parameters
XX:XX:XX:XX:XX:XX:XX:XX:XX
Specifies the 9-octet colon-separated hexadecimal string Interconnect Ethernet Segment Identifier (iESI) value.
all-active
Specifies All-Active multihoming redundancy mode for the interconnect segment.
Default
None
Command Mode
VRF Stitching Mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for configuring an All-Active iESI under EVPN stitching mode.
OcNOS# configure terminal
OcNOS(config)# mac vrf MAC_VRF1
OcNOS(config-vrf)# evpn stitching
OcNOS(config-vrf-evpn)# multi-homed iesi 01:02:03:04:05:06:07:08:09 all-active
neighbor peer-type fabric-external
Use this command to configure a BGP neighbor or peer-group as a site-external Border Gateway peer to enable route re-origination and D-PATH processings.
Use the no parameter of this command to reset the BGP peer fabric type.
Command Syntax
neighbor (A.B.C.D|X:X::X:X|PEER_GROUP) peer-type fabric-external
no neighbor
Parameters
A.B.C.D
Specifies the IPv4 peer address.
X:X::X:X
Specifies the IPv6 peer address.
PEER_GROUP
Specifies the name of a BGP peer group.
fabric-external
Identifies the neighbor as an external site/DCI Border Gateway peer.
Default
fabric-internal
Command Mode
Address Family Mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for configuring an external BGP neighbor under the L2VPN EVPN address family.
OcNOS# configure terminal
OcNOS(config)# router bgp 65000
OcNOS(config-router)# address-family l2vpn evpn
OcNOS(config-router-af)# neighbor 10.10.10.1 peer-type fabric-external
re-originate
Use this command to configure re-origination of route from one address family to another address family.
Use the no parameter of this command to disable route re-origination.
Command Syntax
re-originate l2vpn-evpn as vpnv4-unicast
re-originate l2vpn-evpn as ipv4-unicast
re-originate l2vpn-evpn as ipv6-unicast
re-originate vpnv4-unicast as l2vpn-evpn
re-originate ipv4-unicast as l2vpn-evpn
re-originate ipv6-unicast as l2vpn-evpn
no re-originate
Parameters
l2vpn-evpn
Specifies source routes received from the L2VPN EVPN address family.
vpnv4-unicast
Specifies source/target routes in the VPNv4 unicast address family.
ipv4-unicast
Specifies source/target routes in the IPv4 VRF unicast address family.
Default
Disabled
Command Mode
Address Family Mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for re-originating EVPN routes as VPNv4 unicast routes.
OcNOS# configure terminal
OcNOS(config)# router bgp 65000
OcNOS(config-router)# address-family ipv4 vrf VRF1
OcNOS(config-router-af)# re-originate l2vpn-evpn as vpnv4-unicast
show bgp l2vpn evpn interconnect-hash
Use this command to display the internal BGP EVPN interconnect hash mapping table on the Border Gateway (BGW).
Command Syntax
show bgp l2vpn evpn interconnect-hash
Parameters
None
Default
None
Command Mode
Privileged Exec Mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for displaying the internal BGP EVPN interconnect hash mapping table:
BGW-PE1# show bgp l2vpn evpn interconnect-hash
========================================================================================
NVO ID | Int NVO | UC Label | MC Label | ETREE Leaf | Core Type | VRF ID | Flags
========================================================================================
100 200 100 100 0 1 2 1
200 100 26242 26880 0 2 2 1
300 400 300 300 0 1 3 1
301 401 301 301 0 1 3 1
400 300 26243 26881 0 2 3 1
401 301 26244 26882 0 2 3 1
500 600 500 500 0 1 4 1
600 500 26245 26883 0 2 4 1
BGW-PE1#
show bgp l2vpn evpn domain-tracking-status
Use this command to the operational tracking status of BGP EVPN neighbor sessions across the Data Center (DC) and Wide Area Network (WAN) domains for Interconnect Ethernet Segment Identifier (iESI) multihoming.
Command Syntax
show bgp l2vpn evpn domain-tracking-status
Parameters
None
Default
None
Command Mode
Privileged Exec Mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for displaying the BGP EVPN interconnect hash mapping table between VXLAN VNIs and MPLS EVIs/labels:
BGW-PE2# show bgp l2vpn evpn domain-tracking-status
iESI Domain Tracking (peer GW excluded):
DC neighbor count : 3 => DC ACTIVE
WAN neighbor count : 0 => WAN ISOLATED
BGW-PE2#
show evpn multi-homing domain-tracking-status
Use this command to display the operational tracking and isolation status of Interconnect Ethernet Segment Identifiers (iESI) across Data Center (DC / VXLAN) and Wide Area Network (WAN / MPLS) domains on a Border Gateway (BGW).
Command Syntax
show evpn multi-homing domain-tracking-status
Parameters
None
Default
None
Command Mode
Exec mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for displaying Domain Tracking Status on Active Gateway (Both DC and WAN Active)
BGW-PE1# show evpn multi-homing domain-tracking-status
iESI Domain Tracking Status
===========================
iESI-configured VRFs : 2
Configured peer-GW VTEPs (BGP-pushed) : 88.88.88.88(DC),88.88.88.88(WAN)
Resolved-transit tunnels (peer GW excluded):
DC : 3 => DC ACTIVE
WAN : 4 => WAN ACTIVE
Per-VRF iESI object state:
VRF Domain ESI Isolated Withdrawn Tenants Peer GW(s)
--------------------------------------------------------------------------------------------------------
L2VRF1 DC 00:22:22:22:22:22:22:22:22:22 no no 6 -
L2VRF1 WAN 00:22:22:22:22:22:22:22:22:22 no no 6 -
L2VRF2 DC 00:22:22:22:22:22:22:22:22:22 no no 6 -
L2VRF2 WAN 00:22:22:22:22:22:22:22:22:22 no no 6 -
BGW-PE1#
The following example is for displaying Domain Tracking Status with WAN Isolation Detected:
BGW-PE2# show evpn multi-homing domain-tracking-status
iESI Domain Tracking Status
===========================
iESI-configured VRFs : 2
Configured peer-GW VTEPs (BGP-pushed) : 77.77.77.77(DC),77.77.77.77(WAN)
Resolved-transit tunnels (peer GW excluded):
DC : 3 => DC ACTIVE
WAN : 0 => WAN ISOLATED
Per-VRF iESI object state:
VRF Domain ESI Isolated Withdrawn Tenants Peer GW(s)
--------------------------------------------------------------------------------------------------------
L2VRF1 DC 00:22:22:22:22:22:22:22:22:22 no yes 6 -
L2VRF1 WAN 00:22:22:22:22:22:22:22:22:22 yes yes 6 77.77.77.77
L2VRF2 DC 00:22:22:22:22:22:22:22:22:22 no yes 6 -
L2VRF2 WAN 00:22:22:22:22:22:22:22:22:22 yes yes 6 77.77.77.77
BGW-PE2#
show hsl evpn interconnect iesi-bindings
Use this command to display HSL iESI binding entries.
Command Syntax
show hsl evpn interconnect iesi-bindings
Parameters
None
Default
None
Command Mode
Exec mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for displaying HSL iESI binding entries.
#show hsl evpn interconnect iesi-bindings
! [execution timestamp : 2026 Jul 13 22:32:07]
ESI Remote PE VXLAN-VNID MPLS-EVID ESI-Label MH-PEER VXLAN Tunnel
------------------------------------------------------------------------------------------------------------
00:01:00:00:01:02:00:00:00:00 257 5001 5101 26880 9.9.2.6 9.9.1.11
00:01:00:00:01:02:00:00:00:00 257 5002 5102 26880 9.9.2.6 9.9.1.11
00:01:00:00:01:02:00:00:00:00 257 5003 5103 26880 9.9.2.6 9.9.1.11
00:01:00:00:01:02:00:00:00:00 257 6001 6101 26880 9.9.2.6 9.9.1.11
00:01:00:00:01:02:00:00:00:00 257 6002 6102 26880 9.9.2.6 9.9.1.11
00:01:00:00:01:02:00:00:00:00 257 6003 6103 26880 9.9.2.6 9.9.1.11
00:01:00:00:01:02:00:00:00:00 257 5001 5101 26880 9.9.2.6 9.9.1.10
00:01:00:00:01:02:00:00:00:00 257 5002 5102 26880 9.9.2.6 9.9.1.10
00:01:00:00:01:02:00:00:00:00 257 5003 5103 26880 9.9.2.6 9.9.1.10
00:01:00:00:01:02:00:00:00:00 257 6001 6101 26880 9.9.2.6 9.9.1.10
00:01:00:00:01:02:00:00:00:00 257 6002 6102 26880 9.9.2.6 9.9.1.10
00:01:00:00:01:02:00:00:00:00 257 6003 6103 26880 9.9.2.6 9.9.1.10
00:02:00:00:01:02:00:00:00:00 258 7001 7101 26881 9.9.2.6 9.9.1.11
00:02:00:00:01:02:00:00:00:00 258 7002 7102 26881 9.9.2.6 9.9.1.11
00:02:00:00:01:02:00:00:00:00 258 7003 7103 26881 9.9.2.6 9.9.1.11
00:02:00:00:01:02:00:00:00:00 258 7001 7101 26881 9.9.2.6 9.9.1.10
00:02:00:00:01:02:00:00:00:00 258 7002 7102 26881 9.9.2.6 9.9.1.10
00:02:00:00:01:02:00:00:00:00 258 7003 7103 26881 9.9.2.6 9.9.1.10
show hsl evpn interconnect mac-table
Use this command to display HSL interconnect MAC address table entries across both interconnected tenant domains.
Command Syntax
show hsl evpn interconnect mac-table
Parameters
None
Default
None
Command Mode
Exec mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for displaying HSL EVPN interconnect MAC address table entries for both interconnected tenants.
#show hsl evpn interconnect mac-table
! [execution timestamp : 2026 Jul 13 22:30:47]
+------+----------+-----+--------------+------------------------------+---------------+------+---------------+
| VNID |Interface | VID | MAC-ADDR | Peer/ESI | TYPE | AGE | Etree-discard |
+------+----------+-----+--------------+------------------------------+---------------+------+---------------+
5001 ---- 4234 0010.9400.0003 00:00:00:10:11:00:01:00:00:00 Dynamic 0 ------- Yes
5101 ---- 4234 0010.9400.0009 00:01:00:00:05:06:00:00:00:00 Dynamic 0 ------- Yes
5002 ---- 4235 0010.9400.0004 00:00:00:10:11:00:01:00:00:00 Dynamic 0 ------- Yes
5102 ---- 4235 0010.9400.000a 00:01:00:00:05:06:00:00:00:00 Dynamic 0 ------- Yes
5003 ---- 4236 0010.9400.0005 00:00:00:10:11:00:01:00:00:00 Dynamic 0 ------- Yes
5103 ---- 4236 0010.9400.000b 00:01:00:00:05:06:00:00:00:00 Dynamic 0 ------- Yes
6001 ---- 4237 0010.9400.0006 00:00:00:10:11:00:01:00:00:00 Dynamic 0 ------- Yes
6101 ---- 4237 0010.9400.000c 00:01:00:00:05:06:00:00:00:00 Dynamic 0 ------- Yes
6002 ---- 4238 0010.9400.0007 00:00:00:10:11:00:01:00:00:00 Dynamic 0 ------- Yes
6102 ---- 4238 0010.9400.000d 00:01:00:00:05:06:00:00:00:00 Dynamic 0 ------- Yes
6003 ---- 4239 0010.9400.0008 00:00:00:10:11:00:01:00:00:00 Dynamic 0 ------- Yes
6103 ---- 4239 0010.9400.000e 00:01:00:00:05:06:00:00:00:00 Dynamic 0 ------- Yes
Total number of entries are 12
show hsl evpn mpls tunnels
Use this command to display HSL MPLS tunnel entries.
Command Syntax
show hsl evpn mpls tunnels
Parameters
None
Default
None
Command Mode
Exec mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for displaying HSL EVPN MPLS tunnel entries.
#show hsl evpn mpls tunnels
! [execution timestamp : 2026 Jul 21 22:56:14]
evpn_id dest_ip repl_ifp iml [ing:egr] uc_lbl [ing:egr] tun_nhlfe_id pe_id
7101 9.9.2.1 ce66.10 26889 :27528 24331 :0 11 101
7102 9.9.2.1 ce66.10 26888 :27529 24330 :0 11 101
7103 9.9.2.1 ce66.10 26890 :27530 24332 :0 11 101
4001 9.9.2.1 ce66.10 26881 :27521 24323 :0 11 101
4002 9.9.2.1 ce66.10 26880 :27520 24322 :0 11 101
6101 9.9.2.1 ce66.10 26886 :27525 24328 :0 11 101
6102 9.9.2.1 ce66.10 26885 :27526 24327 :0 11 101
6103 9.9.2.1 ce66.10 26887 :27527 24329 :0 11 101
5101 9.9.2.1 ce66.10 26883 :27522 24325 :0 11 101
5102 9.9.2.1 ce66.10 26882 :27523 24324 :0 11 101
5103 9.9.2.1 ce66.10 26884 :27524 24326 :0 11 101
show hsl evpn tenants
Use this command to display HSL tenant information, including specific tenant IDs, interconnect tenants, overall counts, or all tenant entries.
Command Syntax
show hsl evpn tenants (<1-16777215>|interconnect|all|count)
Parameters
<1-16777215>
Specifies the numerical EVPN tenant ID or VNI to display specific HSL tenant information.
interconnect
Displays HSL tenant entries configured for EVPN interconnect stitching.
all
Displays all HSL EVPN tenant entries programmed in the hardware layer.
count
Displays the total summary count of HSL EVPN tenants
Default
None
Command Mode
Exec mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for displaying HSL EVPN interconnect tenant details.
show hsl evpn tenants all
! [execution timestamp : 2026 Jul 13 22:24:03]
|vnid |nvo-type|fib-id |hw-vpn-id |mc-group |remap-mc-group|is_df|
3001 1 4 4243 0x1093 0x2126 1
3002 1 4 4244 0x1094 0x2128 1
4001 2 5 4232 0x1088 0x0 1
4002 2 5 4233 0x1089 0x0 1
5001 1 6 4234 0x108a 0x2114 0
5002 1 6 4235 0x108b 0x2116 1
5003 1 6 4236 0x108c 0x2118 0
5101 2 6 4234 0x108a 0x0 0
5102 2 6 4235 0x108b 0x0 1
5103 2 6 4236 0x108c 0x0 0
show hsl hw unit 0 evpn esi-hw-table
Use this command to display ESI hardware table entries for unit 0 from HSL.
Command Syntax
show hsl hw unit 0 evpn esi-hw-table
Parameters
None
Default
None
Command Mode
Exec mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for displaying hardware ESI table entries for unit 0.
#show hsl hw unit 0 evpn esi-hw-table
! [execution timestamp : 2026 Jul 13 22:34:31]
flags src_port out_class_id esi_label src_encap_id
0x1 0xffffffff 258 26881 0x40002060
0x1 0xffffffff 257 26880 0x40100001
0x1 0xffffffff 257 26880 0x40002058
0x1 0xffffffff 258 26881 0x40100001
0x1 0xffffffff 257 26880 0x40002056
0x1 0xffffffff 257 26880 0x40100002
0x1 0xffffffff 258 26881 0x40100002
0x1 0xffffffff 257 26880 0x40002054
0x1 0xffffffff 257 26880 0x4000205c
0x1 0xffffffff 257 26880 0x4000205a
0x1 0xffffffff 258 26881 0x40002062
0x1 0xffffffff 258 26881 0x40002064
0x1 0xffffffff 257 26880 0x4000205e
show hsl mac vrf
Use this command to display HSL Layer-2 VRF table information.
Command Syntax
show hsl mac vrf
Parameters
None
Default
None
Command Mode
Exec mode
Applicability
Introduced in OcNOSVersion7.1.0.
Example
The following example is for displaying HSL Layer-2 VRF table entries.
#show hsl mac vrf
! [execution timestamp : 2026 Jul 13 22:32:35]
fib_id |vpn cnt |iesi |is_up|esi_label |remote_lbl|
7 6 00:01:00:00:01:02:00:00:00:00 1 26880 26880
5 2 - - - -
4 2 - - - -
6 6 00:01:00:00:01:02:00:00:00:00 1 26880 26880
8 6 00:02:00:00:01:02:00:00:00:00 1 26881 26881
9 0 - - - -
Revised Commands
The following commands are revised for Interconnecting EVPN VxLAN to MPLS:
• arp-nd flood-suppress, refer to MPLS guide.
• encapsulation, refer to Layer 2 guide.
• evpn mpls id, refer to MPLS guide.
• rd, refer to Layer 3 guide.
• show evpn multi-homing (all|), refer to MPLS guide.
• show evpn multi-homing esi, refer to MPLS guide.
• show evpn esi (all|), refer to MPLS guide.
• show evpn mpls mac-table (info) (evid <1-16777215>|), refer to MPLS guide.
• show evpn mpls label (esi | alias), refer to MPLS guide.
• show evpn mpls arp-cache (evid <1-16777215>|) (summary |), refer to MPLS guide.
• show evpn mpls, refer to MPLS guide.
• show mac vrf, refer to Layer 3 guide.
• show mac vrf WORD, refer to Layer 3 guide.
• show ip route vrf <vrf-name>, refer to section System Limits and Counters Commands in OcNOS System Management guide.
Implementation Examples
Scenario 1: A service provider or enterprise operates a VXLAN-based Data Center (DC) fabric alongside an MPLS-based Wide Area Network (WAN) / Data Center Interconnect (DCI) domain. The organization needs to extend Layer-2 (E-LAN/E-TREE) and Layer-3 VPN services seamlessly across both domains without manual protocol conversions or static tunnels, while preventing routing loops and maintaining multi-homing redundancy across dual Border Gateways (BGWs).
Use Case 1: Configure Interconnecting EVPN VXLAN to MPLS on dual Border Gateways (BGWs) using separate Route Distinguishers (RDs) and Route Targets (RTs) for the LAN and WAN domains under MAC-VRF and IP-VRF sub-blocks. Enable Interconnect Ethernet Segment Identifiers (iESI) for All-Active multihoming, configure BGP Domain Path (D-PATH) attributes to prevent inter-domain loops, and enable BGP route re-origination (re-originate l2vpn-evpn as vpnv4-unicast) between the EVPN fabric and WAN IPVPN peers. This implementation enables automated encapsulation translation (VXLAN ↔ MPLS), end-to-end MAC/IP reachability, and resilient multi-homed traffic forwarding across data center and WAN boundaries.
Troubleshooting
1. EVPN Type-2 (MAC/IP) or Type-5 (IP Prefix) routes are not exchanged between the VXLAN data center fabric and the MPLS DCI network.
• Verify that BGP L2VPN EVPN and VPNv4/v6 neighbor sessions are established.
• Ensure that Border Gateway (BGW) peer connections toward external WAN peers are explicitly configured with neighbor <IP> peer-type fabric-external to allow re-originated route propagation.
• Inspect received routes using show bgp l2vpn evpn and show ip bgp vpnv4 unicast.
2. Committing the command evpn mpls enable fails with an error indicating that the hardware profile filter is missing.
• Enable the global hardware profile filter before committing EVPN MPLS configurations:
OcNOS(config)# hardware-profile filter evpn-arp-nd enable
OcNOS(config)# evpn mpls enable
OcNOS(config)# commit
Glossary
The following provides definitions for key terms or abbreviations and their meanings used throughout this document:
Field | Description |
BGW | Border Gateway: The interconnect/stitching node positioned at the boundary between a VXLAN data center fabric and an MPLS WAN domain that performs encapsulation translation (VXLAN ↔ MPLS) and control-plane route re-origination. |
BUM Traffic | Broadcast, Unknown Unicast, and Multicast Traffic: Data plane traffic that must be replicated and flooded to all members of an Ethernet Broadcast Domain. |
DCI | Data Center Interconnect: The architecture and transport technologies used to connect multiple geographically dispersed data centers across a service provider or WAN backbone. The architecture and transport technologies used to connect multiple geographically dispersed data centers across a service provider or WAN backbone. |
D-PATH | BGP Domain Path Attribute: A BGP path attribute that records the list of domain IDs traversed by a route, preventing routing loops when routes are re-originated across interconnected network domains. |
EVI | EVPN Instance / EVPN Identifier: A customer-specific EVPN routing and forwarding domain spanning one or more Provider Edge (PE) routers. |
EVPN | Ethernet Virtual Private Network: A BGP-based control plane protocol (RFC 7432) used to distribute MAC and IP reachability information for Layer-2 and Layer-3 VPN services across network overlay domains. |
iESI | Interconnect Ethernet Segment Identifier: A unique 9-octet, implicit trailing 0x00 → 10-byte ESI identifier assigned to multi-homed Border Gateways to enable All-Active multihoming, Designated Forwarder (DF) election, and traffic aliasing across stitching domains. |
IMET Route | Inclusive Multicast Ethernet Tag Route (EVPN Type-3): An EVPN control plane route used to discover remote PEs and set up transport tunnels for handling BUM traffic. |
IP-VRF | IP Virtual Routing and Forwarding: A virtual routing instance that maintains an independent IP routing table and interfaces for Layer-3 tenant segregation and inter-subnet routing. |
IRB | Integrated Routing and Bridging: An interface capability that allows a router to perform both Layer-2 switching and Layer-3 IP routing within the same VRF/subnet. |
MAC-VRF | MAC Virtual Routing and Forwarding: A virtual switching instance on an EVPN PE or Border Gateway that maintains an independent MAC address table and VLAN/VNI bindings for Layer-2 services. |
MPLS | Multiprotocol Label Switching: A transport mechanism that directs data packets through a network using short 20-bit path labels rather than long network addresses. |
NLRI | Network Layer Reachability Information: BGP routing payload containing network prefixes, labels, path attributes, and route types. |
VXLAN | Virtual Extensible LAN: An overlay encapsulation protocol that tunnels Layer-2 Ethernet frames over Layer-3 IP networks using 24-bit VXLAN Network Identifiers (VNIs). |